Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
OpenAI Enhances Codex with Continuous Security Monitoring

OpenAI Enhances Codex with Continuous Security Monitoring

Posted on September 30, 2026 By CWS

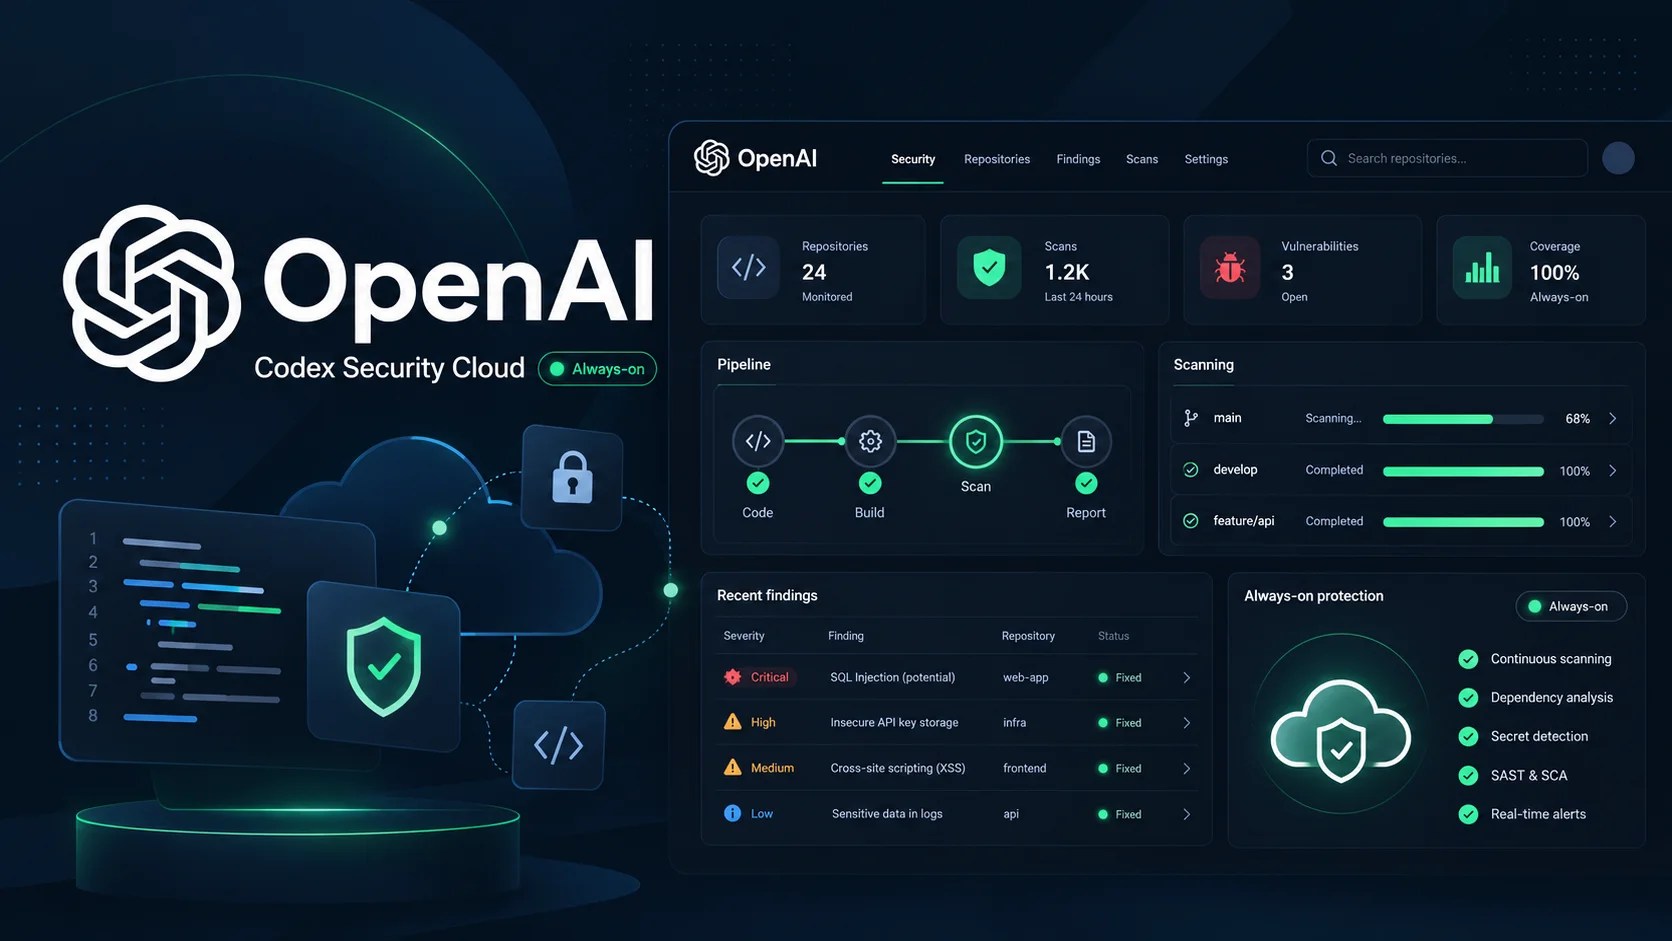
OpenAI has introduced an upgraded version of its Codex platform, now featuring the Codex Security Cloud. This service offers continuous application security by scanning GitHub repositories, monitoring new code commits, and addressing vulnerabilities. Designed to operate seamlessly even when developers are offline, Codex Security Cloud integrates comprehensive vulnerability analysis into everyday workflows.

Advanced Features of Codex Security Cloud

The latest iteration of Codex Security Cloud incorporates cyber-capable models from Daybreak Blue, enhancing its capacity to manage security tasks. By default, it can scan entire GitHub repositories, continuously review commits, and suggest fixes for developer review. This upgrade transforms Codex from a static code scanner into a dynamic security tool, akin to a security researcher, capable of understanding codebases, conducting realistic attack path analyses, and validating potential vulnerabilities in a controlled environment.

Accessible via a plugin on both desktop and web versions of Codex, the Security Cloud is currently available as a research preview to ChatGPT Pro, Business, Enterprise, and Edu users. Teams can connect their GitHub repositories, select suitable cloud environments, and choose between comprehensive scans or continuous monitoring of new commits. Initial scans develop a threat model specific to the project, while subsequent scans focus on newly added code.

Daybreak Blue Integration and Benefits

Daybreak Blue’s integration into Codex Security Cloud brings authorized defensive capabilities, including vulnerability discovery, triage, and secure code review. However, this access is exclusive to the Security Cloud and is not available through other Codex Security products or APIs. By pre-processing findings to eliminate duplicates, Codex Security Cloud aims to reduce alert fatigue, allowing security teams to prioritize significant issues over repeated alerts.

The cloud-based execution facilitates scheduled assessments and individual commit checks independent of local hardware, enhancing efficiency in identifying vulnerabilities. OpenAI stresses the importance of governance, recommending that repository permissions adhere to the principle of least privilege and that generated patches undergo thorough developer review.

Implications for Security Teams

Codex Security Cloud represents a significant evolution in security scanning, offering a persistent defensive resource for development teams. By providing repository-wide insights, continuous monitoring, and validation of findings, OpenAI positions Codex as an essential assistant in defensive engineering. Its success will depend on accurately identifying vulnerabilities without generating excessive noise, and on teams utilizing its automated suggestions as a tool for informed decision-making rather than as a substitute for human oversight.

As OpenAI continues to refine Codex Security Cloud, its potential impact on reducing the time and resources spent on vulnerability management could be substantial. By integrating these advanced features, OpenAI enhances the ability of security teams to respond swiftly and effectively to emerging threats.
Cyber Security News Tags:AI security, application security, automated testing, cloud security, Codex, continuous monitoring, Cybersecurity, Daybreak Blue, developer tools, GitHub, OpenAI, security plugins, security scanning, threat modeling, vulnerability analysis

Post navigation

Previous Post: Critical Flaw in MCP Python SDK Exposes AI Accounts

Related Posts

Citrix Warns Authentication Failures Following The Update of NetScaler to Fix Auth Vulnerability Citrix Warns Authentication Failures Following The Update of NetScaler to Fix Auth Vulnerability Cyber Security News
Hackers Exploiting Fake Battlefield 6 Popularity to Deploy Stealers and C2 Agents Hackers Exploiting Fake Battlefield 6 Popularity to Deploy Stealers and C2 Agents Cyber Security News
Iran-Linked Cyber Group Intensifies Attacks with New Methods Iran-Linked Cyber Group Intensifies Attacks with New Methods Cyber Security News
New MacOS Malware Targets Crypto Wallets with ClickFix New MacOS Malware Targets Crypto Wallets with ClickFix Cyber Security News
Threat Actors Tricks Target Users Via Impersonation and Fictional Financial Aid Offers Threat Actors Tricks Target Users Via Impersonation and Fictional Financial Aid Offers Cyber Security News
2025 Insider Risk Report Finds Most Organizations Struggle to Detect and Predict Insider Risks 2025 Insider Risk Report Finds Most Organizations Struggle to Detect and Predict Insider Risks Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • OpenAI Enhances Codex with Continuous Security Monitoring
  • Critical Flaw in MCP Python SDK Exposes AI Accounts
  • Critical Flaws Addressed in OpenSSL and WolfSSL Updates
  • Critical Citrix NetScaler Flaw Allows Remote Code Execution
  • OpenSSL Patches Critical DTLS Vulnerability

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • OpenAI Enhances Codex with Continuous Security Monitoring
  • Critical Flaw in MCP Python SDK Exposes AI Accounts
  • Critical Flaws Addressed in OpenSSL and WolfSSL Updates
  • Critical Citrix NetScaler Flaw Allows Remote Code Execution
  • OpenSSL Patches Critical DTLS Vulnerability

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark