Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical PHP2Shell Exploit Released for Security Testing

Critical PHP2Shell Exploit Released for Security Testing

Posted on October 21, 2026 By CWS

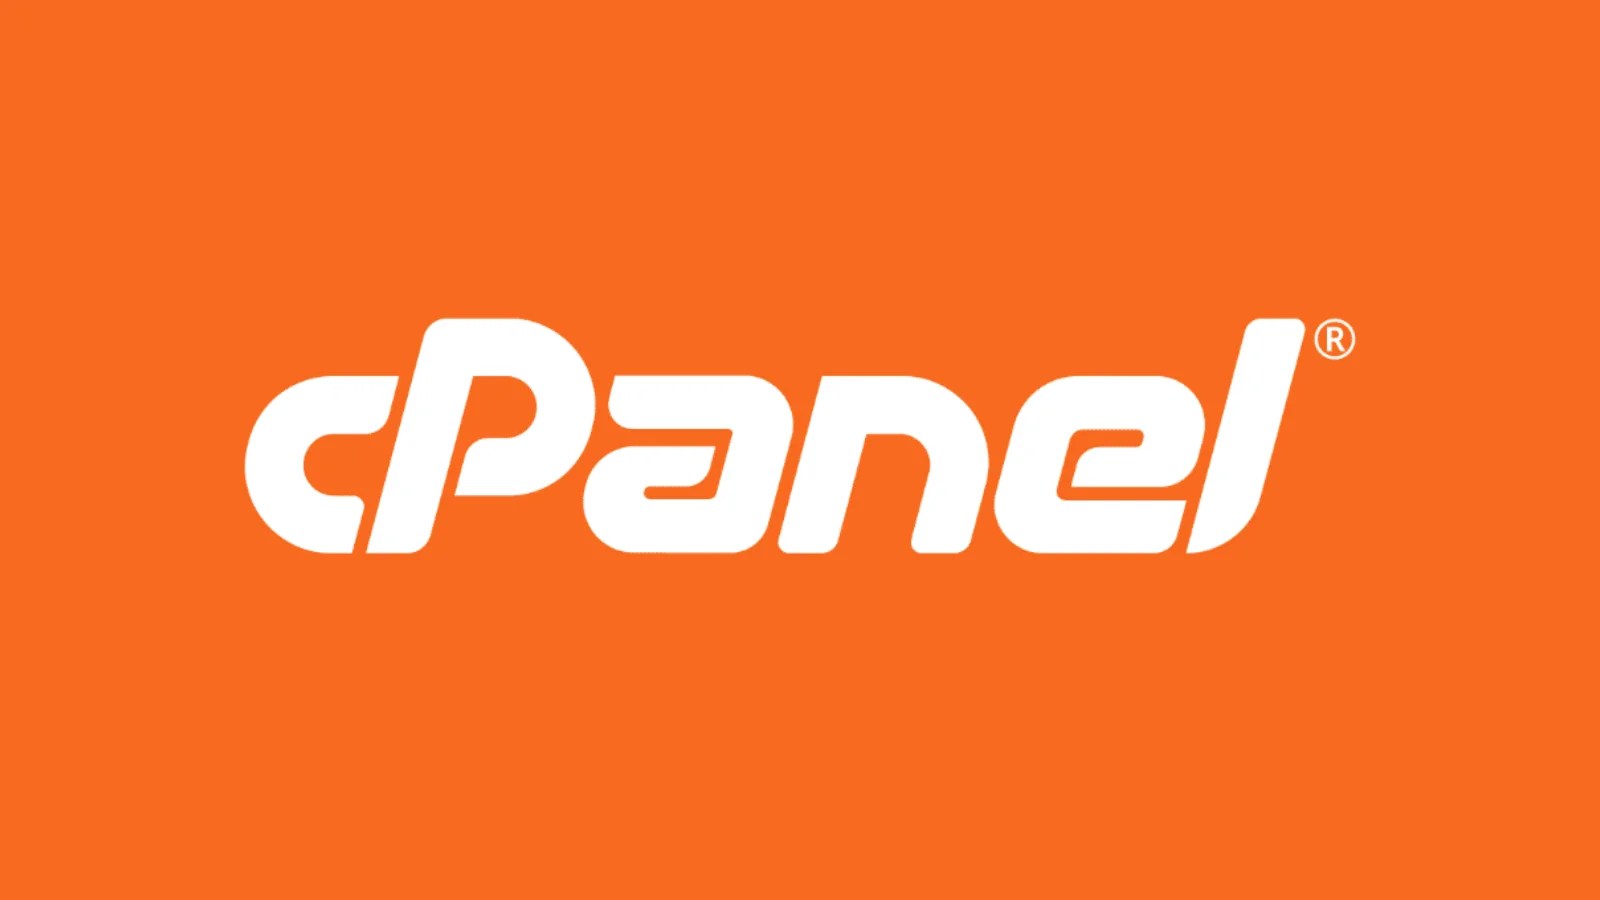
A recently released proof-of-concept repository has unveiled tools to verify and test two significant vulnerabilities within PHP, named php2shell. Identified as CVE-2026-109618 and CVE-2026-109619, these flaws are linked to the session.upload_progress feature in PHP and may lead to remote code execution under specific conditions.

Details of the PHP Vulnerabilities

The PHP security team has acknowledged these vulnerabilities and announced an urgent release to address them, rating each flaw at 9.2 according to CVSS v4.0 standards. This update is slated for release on October 21 at 14:00 UTC, though full technical details and the affected versions have yet to be confirmed by PHP’s official channels.

According to the research repository, these vulnerabilities impact PHP versions from 5.4.0 to 8.5.11. Planned fixes are anticipated in PHP versions 8.2.35, 8.3.36, 8.4.27, and 8.5.12. Administrators are advised to verify these details against the official PHP release advisory before proceeding with updates.

Understanding the Exploit Paths

The research highlights various methods to achieve code execution rather than a single exploit applicable to all PHP sites. One notable path exploits a combination of session-file injection and local file inclusion in applications where upload progress is enabled. This scenario arises when an application unintentionally loads a file from its server.

Additionally, the repository notes that PHP’s upload-progress handler may store a filename in session data without proper validation. It suggests that session identifiers sent via POST can bypass the intended restrictions of session.use_only_cookies. However, it’s critical to note that not all PHP sites are vulnerable through these paths.

Implications for PHP Deployments

The second significant issue involves a use-after-free error, where data is accessed after being released. This can occur when re-entering a var_destroy destructor, confirmed through tools like AddressSanitizer. The research also mentions potential issues with PHP-FPM serializer state persistence and handler mismatches post-deserialization.

Given PHP’s widespread use, a vulnerability in its session management could broadly impact deployments, especially if an application already presents file inclusion weaknesses. Mallory’s report highlights that, as of October 20, approximately 59% of PHP hosts are running unsupported versions, emphasizing the need for migration to secure versions.

Recommendations and Future Steps

Administrators are urged to inventory PHP installations and check for affected versions once PHP issues its security release. Until then, temporary measures like disabling session.upload_progress and enforcing session.use_only_cookies may reduce exposure. However, these are not replacements for comprehensive security updates.

The public proof-of-concept serves as a reminder to prepare and validate systems safely. The key step is to align research findings with PHP’s official updates and promptly apply patches to affected systems as they become available.

Cyber Security News Tags:CVE-2026-109618, CVE-2026-109619, Cybersecurity, PHP exploit, PHP security, PHP security update, PHP session handling, PHP session.upload_progress, PHP versions, PHP vulnerability, PHP-FPM, remote code execution, security patch, session management, Vulnerability

Post navigation

Previous Post: Browsers Block eMudhra Certificates Due to Security Breach
Next Post: Harnessing AI for Secure Pentesting: Key Challenges

Related Posts

Urgent Patch for QNAP QVR Pro Security Flaw Released Urgent Patch for QNAP QVR Pro Security Flaw Released Cyber Security News
Government Servers Compromised Through cPanel Vulnerability Government Servers Compromised Through cPanel Vulnerability Cyber Security News
Splunk Address Third-Party Packages Vulnerabilities in SOAR Versions Splunk Address Third-Party Packages Vulnerabilities in SOAR Versions Cyber Security News
Sandworm Hackers Shift Focus to Critical Infrastructure Sandworm Hackers Shift Focus to Critical Infrastructure Cyber Security News
New Sophisticated Phishing Attack Mimic as Google Support to Steal Logins New Sophisticated Phishing Attack Mimic as Google Support to Steal Logins Cyber Security News
New MacOS Malware Targets Crypto Wallets with ClickFix New MacOS Malware Targets Crypto Wallets with ClickFix Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Microsoft Enhances Azure Bug Bounty Incentives for Detailed Reports
  • China Criticizes US Ban on DeepSeek AI in Government Systems
  • Harnessing AI for Secure Pentesting: Key Challenges
  • Critical PHP2Shell Exploit Released for Security Testing
  • Browsers Block eMudhra Certificates Due to Security Breach

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Microsoft Enhances Azure Bug Bounty Incentives for Detailed Reports
  • China Criticizes US Ban on DeepSeek AI in Government Systems
  • Harnessing AI for Secure Pentesting: Key Challenges
  • Critical PHP2Shell Exploit Released for Security Testing
  • Browsers Block eMudhra Certificates Due to Security Breach

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark