Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
RAVEN Tool Exploits Elasticsearch Vulnerabilities

RAVEN Tool Exploits Elasticsearch Vulnerabilities

Posted on August 19, 2026 By CWS

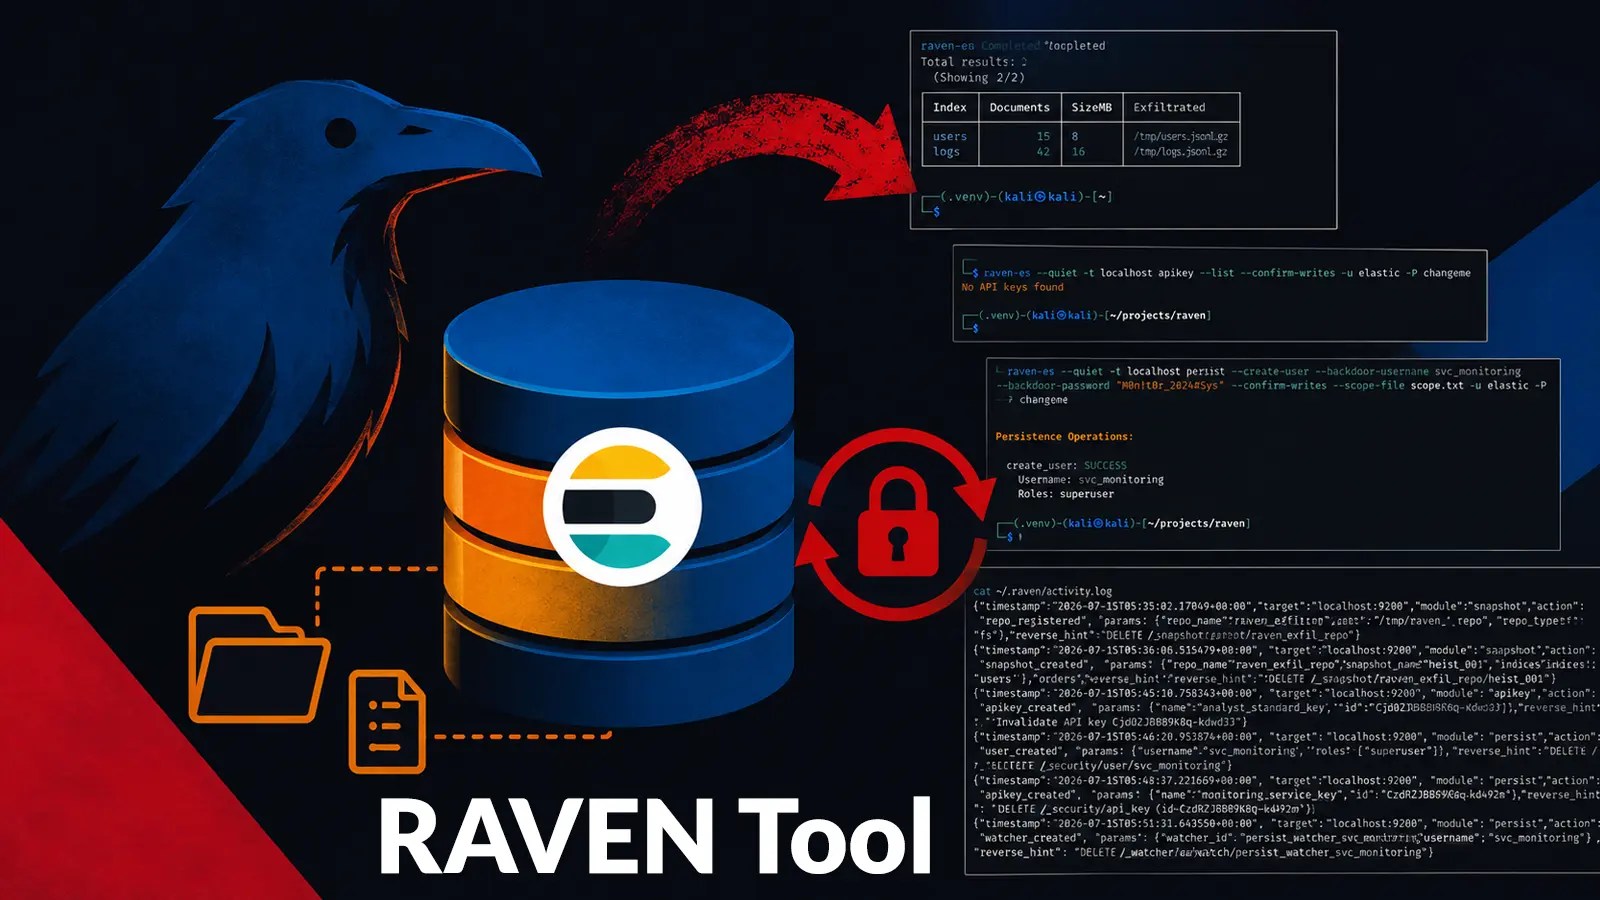
A newly uncovered offensive security tool, known as RAVEN, highlights potential data-loss scenarios through compromised Elasticsearch environments. This tool demonstrates how attackers maintain access even after security measures, such as password rotations, are implemented.

Understanding RAVEN’s Attack Path

RAVEN showcases the actions a malicious actor could undertake post-breach of an exposed cluster or following control over Kibana. The attack initiates after the reconnaissance phase, exploiting vulnerabilities to infiltrate the system.

Once inside, the attacker can query the Elasticsearch database, copy data, and establish alternate credentials. Moreover, they can install mechanisms to regain access, even after defenders attempt to clear the threat.

Capabilities and Risks of RAVEN

LevelBlue researchers, in a report shared with Cyber Security News, emphasize that RAVEN is intended for penetration testing rather than evidence of an ongoing criminal operation. However, its techniques underline the risks associated with inadequate data security.

The tool can exfiltrate data using the Point-in-Time API for newer Elasticsearch versions, or the Scroll API for older ones, making it possible to gather extensive datasets from compromised environments.

RAVEN can also create snapshots internally within Elasticsearch, minimizing network traffic and reducing detection likelihood. This poses a significant business risk, as sensitive data could be stealthily transferred to attacker-controlled servers.

Persistent Threats via API Keys

A critical aspect of RAVEN’s demonstration involves exploiting Elasticsearch API keys. These keys allow for authentication without user passwords, meaning attackers can maintain access even if passwords are changed.

The tool can list and create API keys with the same permissions as the compromised user, posing a continuous threat. Additionally, the presence of unauthorized Watcher tasks can recreate deleted users and keys, complicating cleanup efforts.

Mitigating the Risks of RAVEN

Organizations are urged to prioritize patching vulnerabilities such as those addressed in recent Elastic security updates. Limiting access to management ports and tightening credential management are critical steps in mitigating potential threats.

Security teams should conduct thorough audits of users, API keys, and Watcher configurations, revoking unknown credentials and monitoring for suspicious activities. Ongoing vigilance is essential to ensure that no unauthorized mechanisms remain within the environment.

As cyber threats evolve, integrating real-time intelligence from global security operations centers can help preemptively address new phishing and malware threats, safeguarding businesses from potential compromises.
Cyber Security News Tags:API keys, cyber threat, Cybersecurity, data exfiltration, data protection, Elasticsearch, Kibana, penetration testing, persistent access, Raven, security patches, Vulnerability

Post navigation

Previous Post: US Indicts 17 Iranian Hackers, Offers $10M Rewards
Next Post: Active Exploitation of Critical Software Vulnerabilities

Related Posts

20-Year-Old Vulnerability Allows Hackers to Control Train Brakes 20-Year-Old Vulnerability Allows Hackers to Control Train Brakes Cyber Security News
Hackers Abuse Microsoft Teams to Gain Remote Access With PowerShell-based Malware Hackers Abuse Microsoft Teams to Gain Remote Access With PowerShell-based Malware Cyber Security News
How Simple Prompts Can Lead to Major Breaches How Simple Prompts Can Lead to Major Breaches Cyber Security News
Beware of Phishing Email from Kimusky Hackers With Subject Spetember Tax Return Due Date Notice Beware of Phishing Email from Kimusky Hackers With Subject Spetember Tax Return Due Date Notice Cyber Security News
Acer Control Center Vulnerability Let Attackers Execute Malicious Code as a Privileged User Acer Control Center Vulnerability Let Attackers Execute Malicious Code as a Privileged User Cyber Security News
Hackers Utilize Open Banking for Credential Testing Hackers Utilize Open Banking for Credential Testing Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Armornet Launches AI Security for Software Supply Chains
  • Critical NGINX HTTP/2 Vulnerability Allows Remote Code Execution
  • SpyCloud Predicts 2027 Cyber Threats: AI and Trusted Access Risks
  • 2027 Cybersecurity Awards: New AI Categories Announced
  • Malicious Agent Framework Releases Threaten Credentials

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Armornet Launches AI Security for Software Supply Chains
  • Critical NGINX HTTP/2 Vulnerability Allows Remote Code Execution
  • SpyCloud Predicts 2027 Cyber Threats: AI and Trusted Access Risks
  • 2027 Cybersecurity Awards: New AI Categories Announced
  • Malicious Agent Framework Releases Threaten Credentials

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark