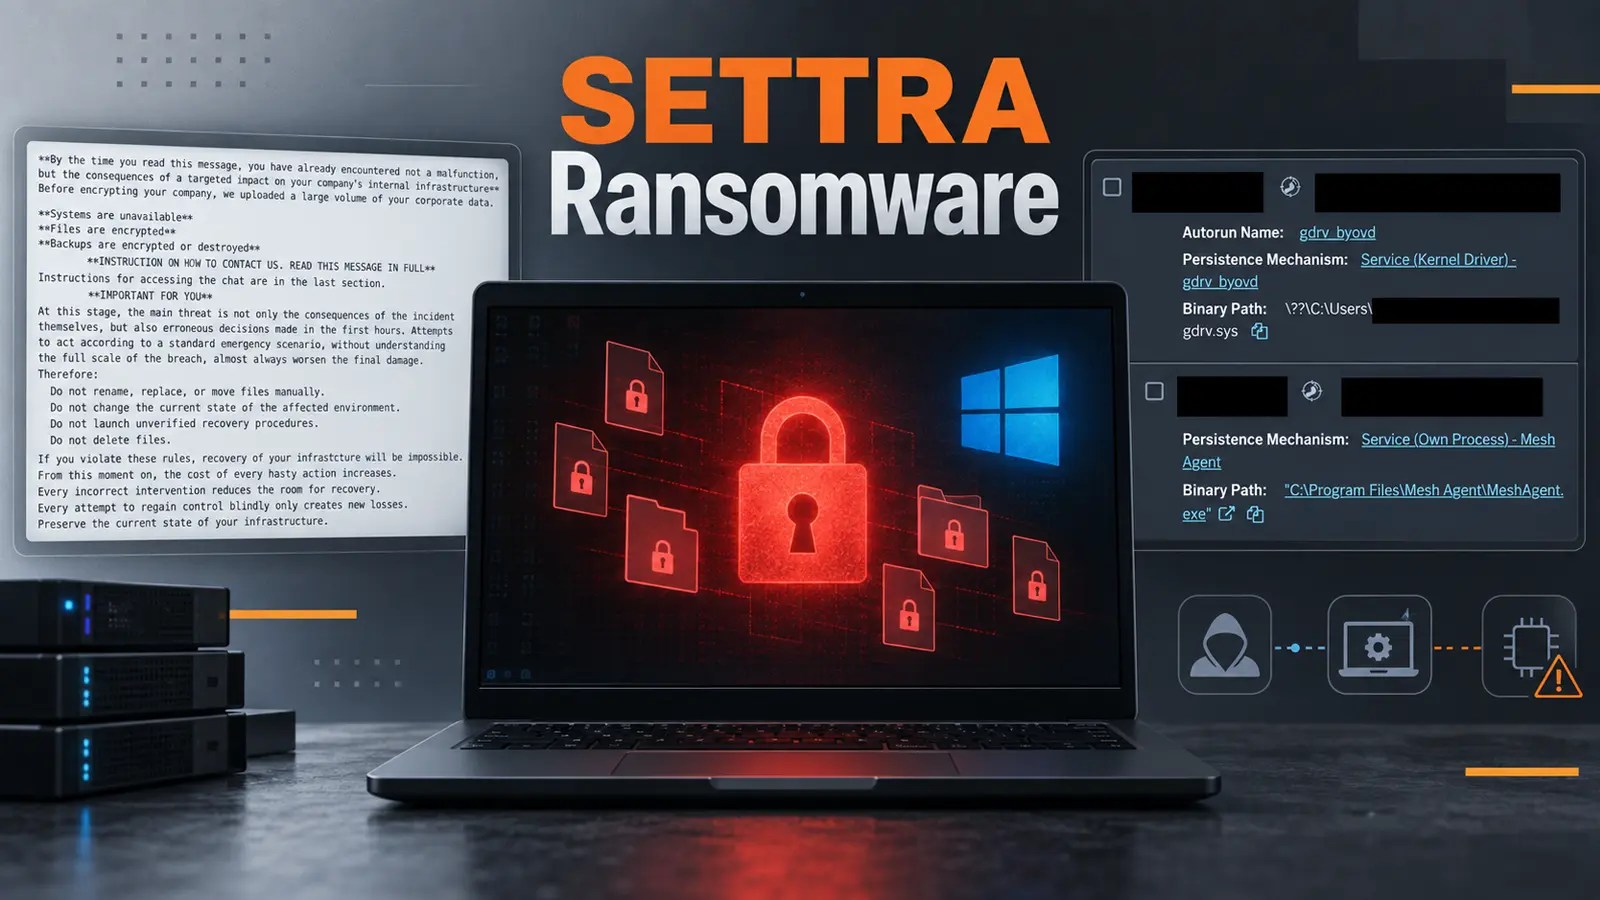
Settra ransomware has been identified as a significant threat to Windows networks, as security experts link it to recent breaches involving remote-management software and recovery-blocking tactics. The ransomware encrypts files and complicates both investigation and data recovery, raising concerns about network vulnerabilities.
Emerging Threats in Cybersecurity
Settra’s operators gain access through compromised virtual private networks (VPNs) or stolen credentials. This highlights the critical need for robust remote access security and vigilant account controls. The misuse of legitimate administration tools in network intrusions is becoming increasingly common, complicating detection and response efforts.
Analysts from Huntress identified two incidents involving Settra: one in July affecting a consumer services and retail firm, and another in September targeting a manufacturer. While the initial access methods remain unclear, post-compromise activities in both cases were notably similar.
Use of MeshAgent and BYOVD Techniques
After infiltrating a network, Settra operators deploy MeshAgent, a remote monitoring and management tool, to execute commands and maintain system control. This strategy allows attackers to advance their operations without relying solely on custom malware, complicating mitigation efforts. In one incident, MeshAgent was renamed and linked to an attacker-controlled command-and-control server.
The September attack utilized a ‘Bring Your Own Vulnerable Driver’ (BYOVD) approach, employing a flawed driver to disable security defenses, facilitating the encryption process. This method underscores the persistent threat posed by previously trusted Windows drivers in ransomware attacks.
Implications for Network Security
The ransomware operations involved disabling Windows Event Logs and the Windows Recovery Environment, utilizing DiskPart to remove recovery partitions, and clearing DNS caches to obstruct recovery processes. Such actions increase the difficulty of forensic investigations and prolong system downtime.
Organizations must prioritize basic security controls to mitigate these threats. Strong VPN authentication, restricted remote management tool usage, and vigilance against unexpected driver installations are essential. Maintaining offline or secure backups and testing incident response plans against simulated ransomware attacks are critical steps to enhance preparedness.
Conclusion and Recommendations
Settra ransomware demonstrates that attackers can cause significant disruptions without new tools, leveraging familiar software and vulnerable drivers to pressure defenders. Fast detection of unusual RMM activities, securing logs, and rehearsed recovery strategies are vital defenses. These measures can help prevent incidents from escalating into full-blown crises.
Indicators of compromise (IoCs) include specific IP addresses, renamed executables, and particular file extensions used in these incidents. Awareness and proactive measures are crucial for safeguarding against such sophisticated threats.