Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Microsoft Patches Severe Azure AI Foundry Vulnerability

Microsoft Patches Severe Azure AI Foundry Vulnerability

Posted on September 18, 2026 By CWS

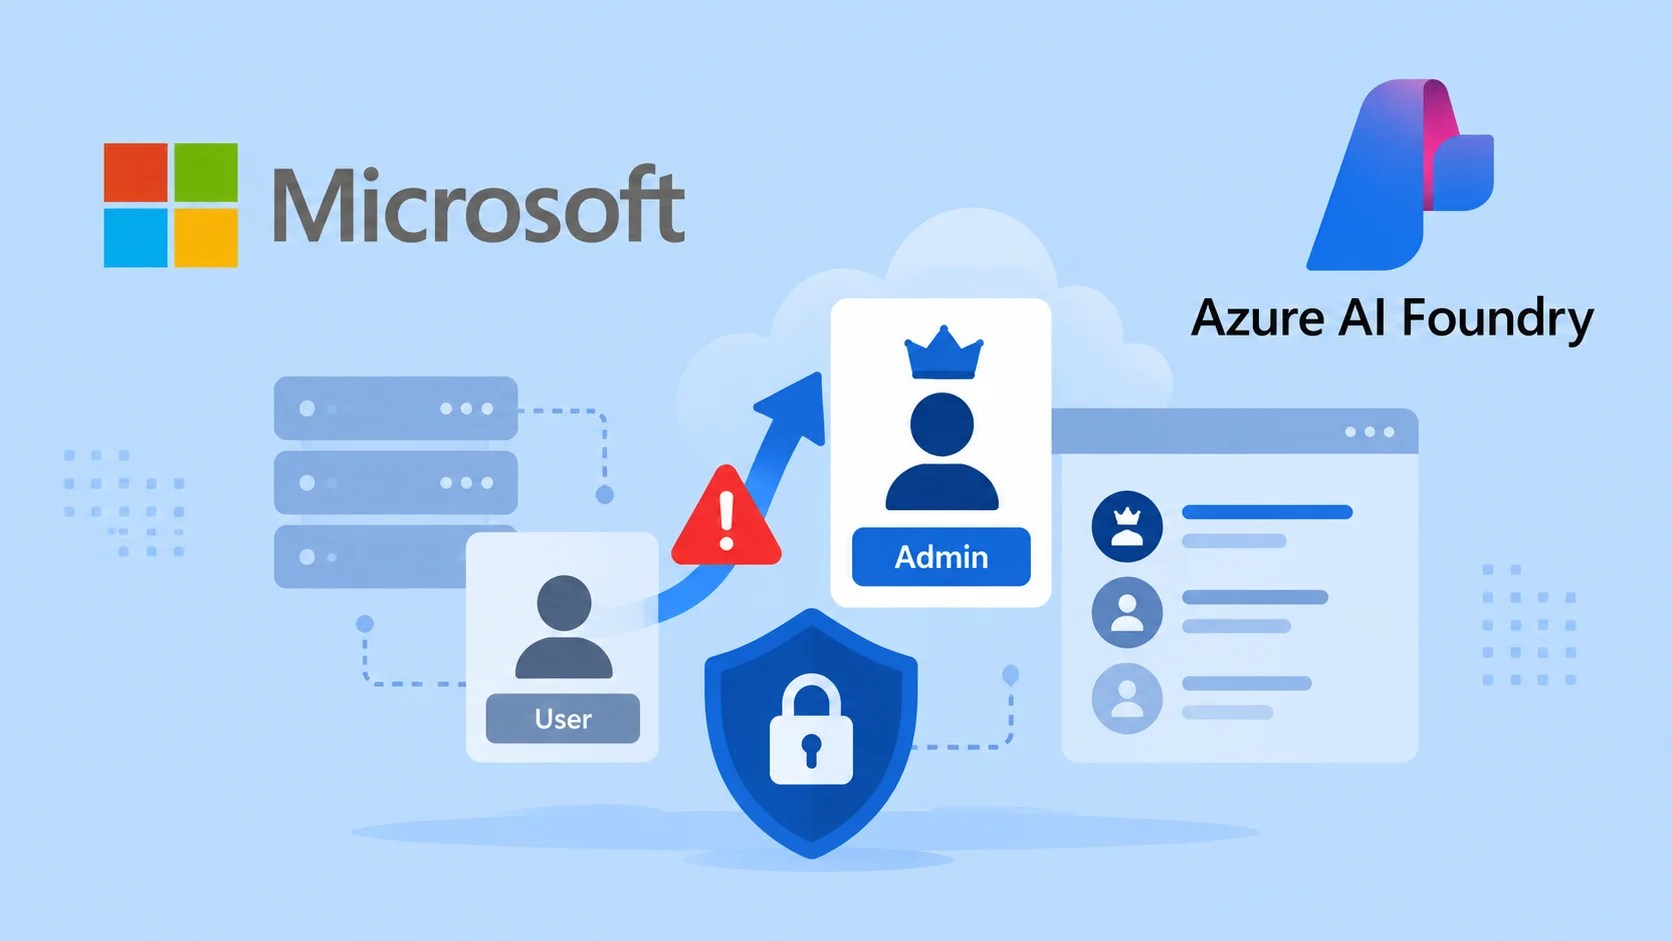
Microsoft has recently resolved a critical security vulnerability in its Azure AI Foundry platform, which is used for developing and managing generative AI applications. This flaw, identified as CVE-2026-85889, had the potential to allow unauthorized attackers to elevate their privileges on the network without user interaction. The vulnerability was given the highest CVSS score of 10.0, highlighting its severity among cloud security threats disclosed this year.

Details of the Vulnerability

According to a Microsoft advisory dated September 17, 2026, the vulnerability stemmed from an absent authentication check within a crucial function of Azure AI Foundry, categorized under CWE-306. This oversight could have enabled attackers without valid credentials to exploit a backend function, bypassing existing identity and access controls designed to protect privileged operations.

The flaw was accessible through a network-based attack vector, characterized by low complexity and not requiring any user interaction or privileges, making it theoretically easy to exploit. However, Microsoft reported no evidence of active exploitation or public availability of proof-of-concept code.

Implications for Enterprises

Azure AI Foundry, also known as Microsoft Foundry, serves as a pivotal platform for enterprises deploying generative AI models, agents, and workflow orchestrations. A vulnerability of this nature on such a platform is particularly alarming, as successful exploitation could grant external attackers the same level of control as a legitimate privileged user. This could potentially expose sensitive AI models, training data, and interconnected enterprise resources or systems.

The discovery of this flaw is credited to security researcher Rémy Marot, who responsibly disclosed the issue via Microsoft’s coordinated vulnerability disclosure program. As a result, Microsoft has implemented a complete backend fix, ensuring that users of Azure AI Foundry do not need to take any further action, such as installing patches or modifying configurations.

Context and Additional Fixes

This disclosure coincides with several other critical Microsoft fixes, including CVE-2026-85885, a command injection vulnerability in Microsoft 365 Copilot with a CVSS score of 9.9, and CVE-2026-85878, an authorization issue in Azure Database for PostgreSQL also rated 9.9. Both issues, like the Foundry flaw, have the potential to allow privilege escalation over a network.

Furthermore, Microsoft released an out-of-band update for Windows 11 version 26H1, addressing a Windows User-Mode Power Service vulnerability and a Secure Kernel Mode double-free bug capable of granting SYSTEM or Virtual Trust Level 1 privileges. These efforts follow closely after Microsoft’s record-breaking Patch Tuesday, which addressed 974 vulnerabilities, with two actively being exploited through an exploit kit named BlueMoon.

Although there is no current indication of active exploitation of CVE-2026-85889, its critical nature and the increasing reliance on AI platforms by enterprises emphasize the necessity for organizations to monitor Microsoft’s security advisories diligently, even for cloud services with vendor-managed patching.

Cyber Security News Tags:AI, Azure AI Foundry, BlueMoon, cloud security, CVE-2026-85889, CWE-306, Cybersecurity, Enterprise, Microsoft, Patch, Patch Tuesday, privilege escalation, Remy Marot, Security, Vulnerability

Post navigation

Previous Post: Brevo Security Breach Impacts Over 100,000 Websites
Next Post: Abandoned CDN Domain Re-Registered, Impacting Thousands

Related Posts

AI-Powered DockSec Enhances Docker Security AI-Powered DockSec Enhances Docker Security Cyber Security News
Hackers Exploit Job Offers on LinkedIn to Spread Malware Hackers Exploit Job Offers on LinkedIn to Spread Malware Cyber Security News
SSH Bot Analyzes Linux Systems for Cryptomining Potential SSH Bot Analyzes Linux Systems for Cryptomining Potential Cyber Security News
ASP.NET Developers Targeted by Malicious NuGet Packages ASP.NET Developers Targeted by Malicious NuGet Packages Cyber Security News
Chaos Ransomware Exploits Browsers as Secret Command Channels Chaos Ransomware Exploits Browsers as Secret Command Channels Cyber Security News
Delta Dental of Virginia Data Breach Exposes 146,000+ Customers Personal Details Delta Dental of Virginia Data Breach Exposes 146,000+ Customers Personal Details Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Securely Unlock BYDFi’s 8,100 USDT Welcome Rewards
  • Critical Flaw in CryptoPayment Plugin Endangers Wallet Security
  • ARTEX AI Exploit Leads to WorkOS Security Breach
  • Siemens IoT2050 Vulnerability Allows Remote Command Exploits
  • Anthropic Introduces EDR Monitoring in Claude Cowork

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Securely Unlock BYDFi’s 8,100 USDT Welcome Rewards
  • Critical Flaw in CryptoPayment Plugin Endangers Wallet Security
  • ARTEX AI Exploit Leads to WorkOS Security Breach
  • Siemens IoT2050 Vulnerability Allows Remote Command Exploits
  • Anthropic Introduces EDR Monitoring in Claude Cowork

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark