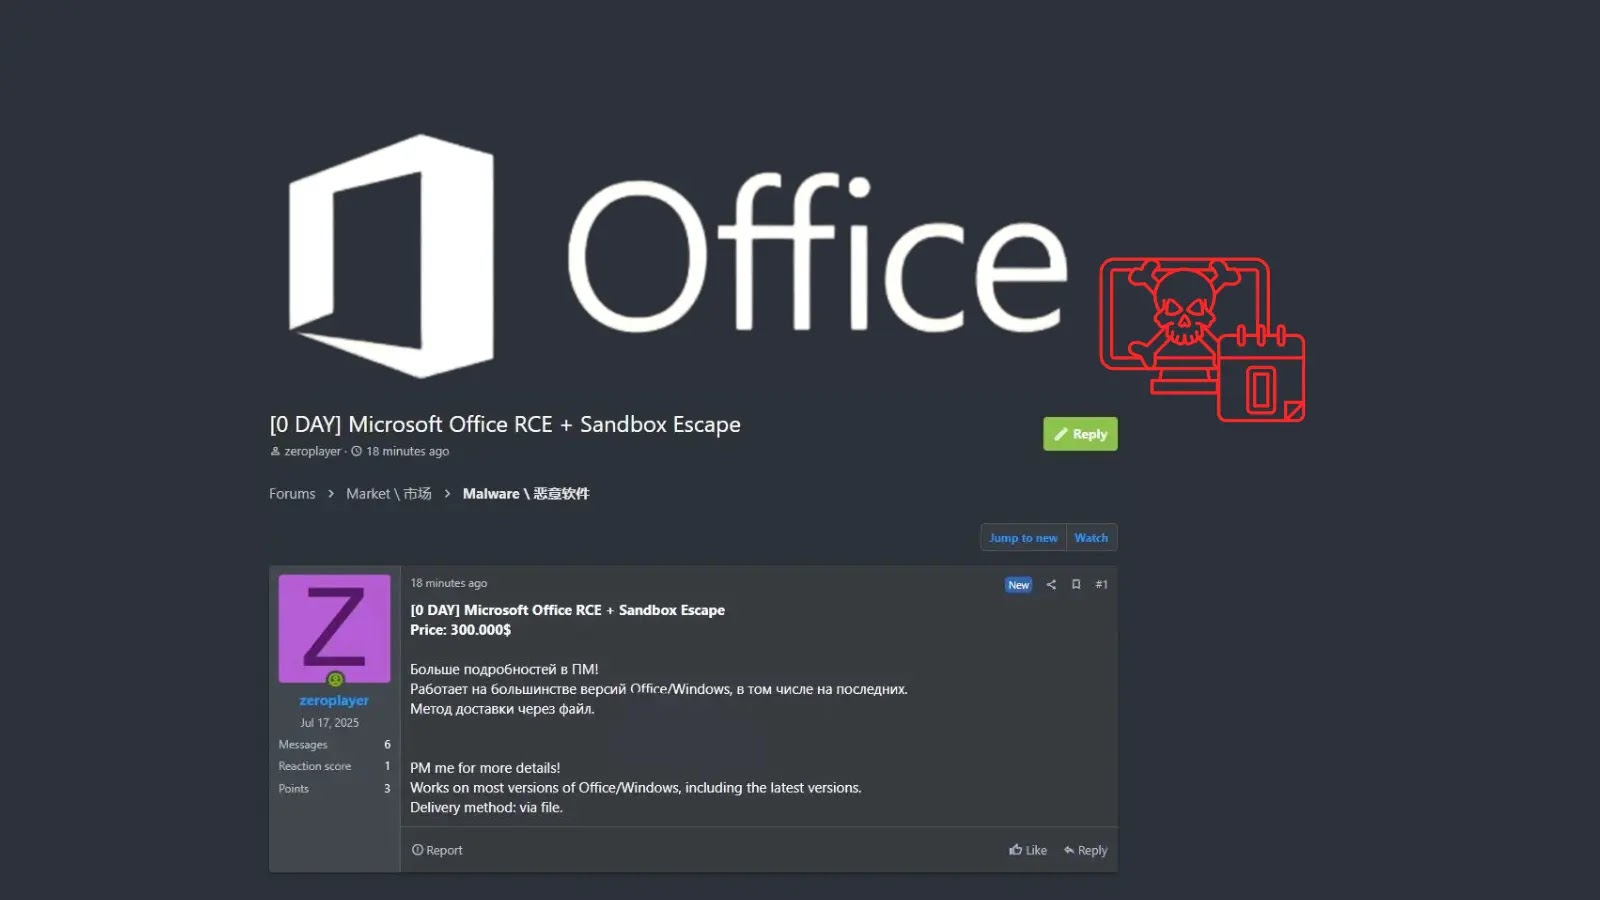
A risk actor generally known as Zeroplayer has reportedly listed a zero-day distant code execution (RCE) vulnerability, mixed with a sandbox escape, concentrating on Microsoft Workplace and Home windows programs on the market on underground hacking boards.
Priced at $30,000, the exploit purportedly works on most Workplace file codecs, together with the most recent variations, and impacts absolutely patched Home windows installations.
This growth raises alarms within the cybersecurity group, because it may allow attackers to bypass Microsoft’s sturdy sandbox protections and execute arbitrary code with minimal person interplay.
The commercial, posted in Russian on a outstanding hacking discussion board, describes the vulnerability as a high-impact 0-day able to delivering payloads by way of malicious Workplace paperwork.
Zeroplayer claims the exploit chain permits distant attackers to flee the Workplace sandbox a important safety characteristic designed to isolate doubtlessly dangerous code—and obtain full system compromise on Home windows.
Supply strategies contain embedding the exploit in widespread file sorts like Phrase or Excel paperwork, which might be distributed by way of phishing emails or compromised web sites.
Alleged Microsoft Workplace 0-Day Declare
Particulars of the Hacker Discussion board Itemizing
The vendor invitations non-public messages for demonstrations and proof-of-concept particulars, emphasizing compatibility with latest updates to mitigate detection by antivirus instruments.
This isn’t Zeroplayer’s first foray into the exploit market; the actor beforehand provided a WinRAR zero-day RCE for $80,000 in July 2025, highlighting a sample of concentrating on extensively used productiveness and archiving software program.
Such gross sales underscore the profitable underground economic system for zero-days, the place exploits fetch premium costs earlier than public disclosure or patching.
Microsoft’s November 2025 Patch Tuesday addressed a number of important RCE flaws in Workplace, together with CVE-2025-62199, a use-after-free vulnerability exploitable by way of malicious paperwork.
Nevertheless, that patch centered on identified points and didn’t reference this alleged 0-day, suggesting it stays unpatched and doubtlessly extra harmful as a result of its sandbox escape part.
Sandbox escapes are notably regarding, as they neutralize one in all Workplace’s major defenses in opposition to macro-based assaults, permitting malware to unfold laterally throughout networks.
Specialists notice that Russian-language boards just like the one internet hosting this itemizing usually function hubs for state-affiliated or opportunistic risk actors, who might weaponize such exploits for ransomware, espionage, or knowledge theft.
Comparable previous incidents, such because the 2023 exploitation of CVE-2023-36884 by the Russian group Storm-0978, concerned Workplace RCE for backdoor deployment in opposition to Western targets.
The potential fallout from this 0-day is important, particularly for enterprises reliant on Microsoft 365. Attackers may leverage it to compromise provide chains or conduct focused intrusions, evading endpoint detection responses.
Given Workplace’s ubiquity throughout over 1.4 billion gadgets globally, unpatched programs face a heightened threat of an infection by way of spear-phishing.
Organizations ought to prioritize macro disabling in Workplace insurance policies, allow Protected View for all paperwork, and deploy superior risk safety instruments.
Monitoring for anomalous discussion board exercise and making use of upcoming patches urgently is suggested, as Microsoft might speed up fixes if exploitation proof emerges.
Observe us on Google Information, LinkedIn, and X for each day cybersecurity updates. Contact us to characteristic your tales.