Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
US Indicts Two Companies for Cybercrime Support

US Indicts Two Companies for Cybercrime Support

Posted on July 15, 2026 By CWS

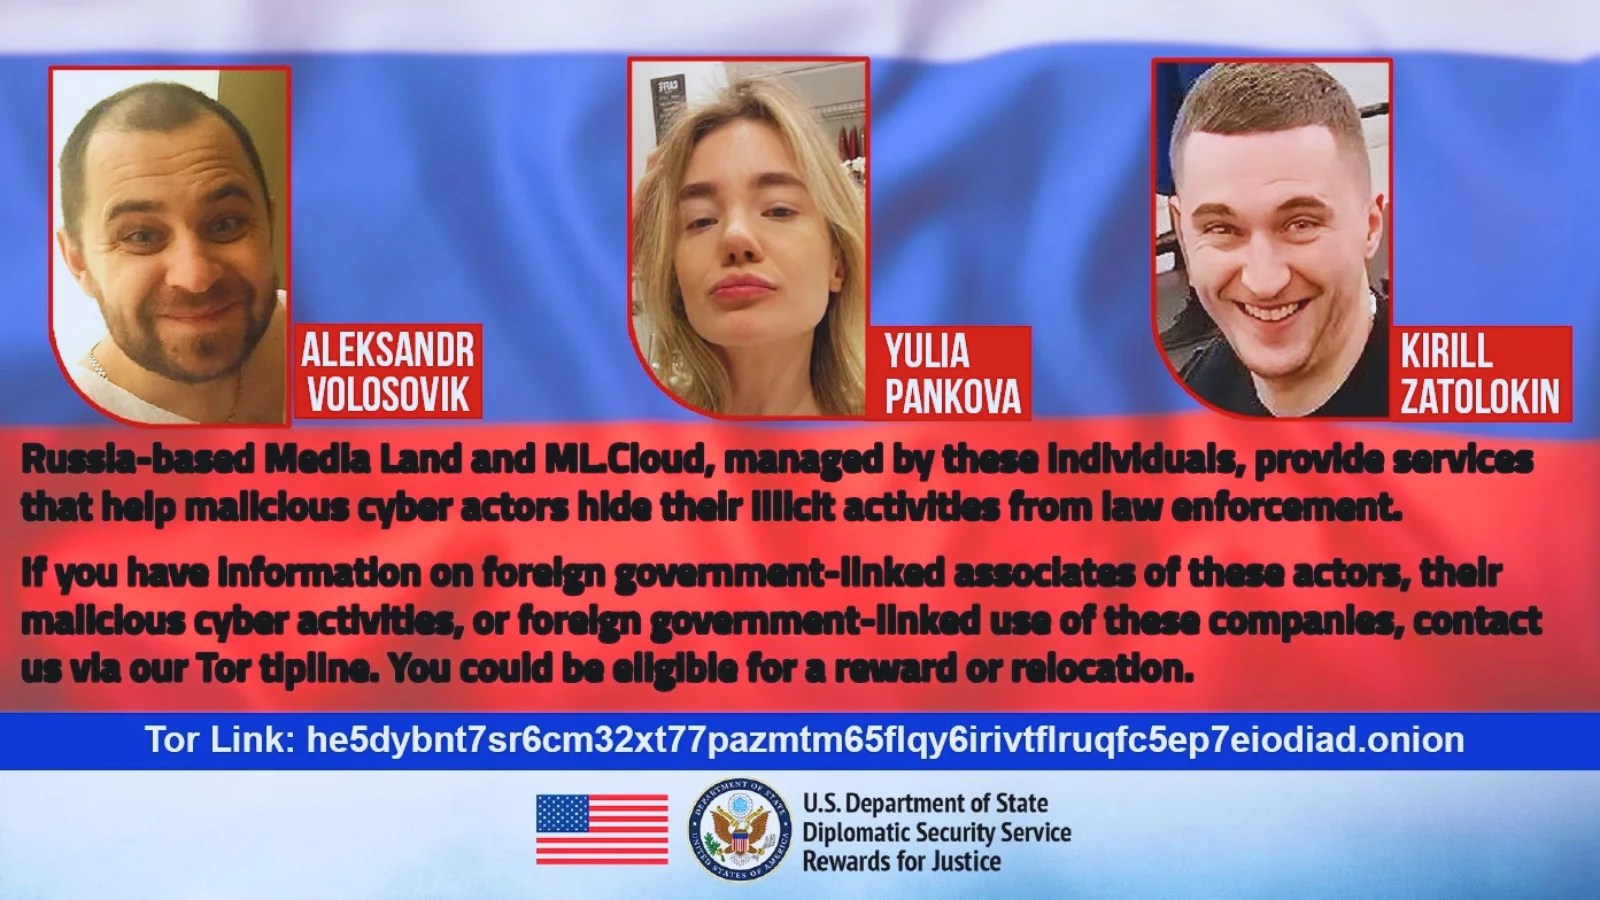
The United States Department of Justice has unveiled charges against three Russian individuals and two Russian-based companies, accused of facilitating extensive cybercriminal activities. These actions have reportedly resulted in financial damages amounting to tens of millions across the US.

Details of the Indictment

The charges, initially filed in December 2024 in Ohio’s Northern District, include conspiracy, aiding computer fraud, wire fraud, and money laundering. The accused individuals are Alexander Alexandrovich Volosovik, Kirill Andreevich Zatolokin, and Yulia Vladimirovna Pankova, all residents of St. Petersburg, Russia. The implicated companies are Medialand LLC and ML.Cloud LLC, both based in the same city.

Role of Hosting Companies

According to prosecutors, Medialand and ML.Cloud provided server infrastructure that circumvented law enforcement detection, assisting in various cybercrimes. Volosovik promoted these services in online criminal forums, highlighting their capability to support global operations. Such infrastructure was allegedly used for malware deployment, digital currency extortion, and other illicit activities, paralleling tactics used in prior ransomware cases.

Impact and International Collaboration

The operations reportedly affected 42 organizations across 21 states, targeting sectors like healthcare, finance, education, media, and government. To combat these threats, security teams are advised to regularly audit system traffic and watch for signs of malicious activities akin to gitpaste-12 malware.

The US government has also announced a $10 million reward for information linking the accused to foreign entities. Meanwhile, the Treasury Department and international allies, including the UK and Australia, have imposed sanctions on the individuals and their corporate entities.

Investigation and Future Outlook

This indictment is part of a broader initiative, Operation Riptide, led by the FBI’s Cleveland Division. This operation aims to counteract the rising tide of cybercrime, which has led to significant financial losses. The investigation received support from various agencies, including CISA, OFAC, and international law enforcement partners from the Netherlands, the UK, and Australia.

As cyber threats continue to evolve, strengthening cybersecurity measures remains crucial. The DOJ’s actions underscore the importance of international cooperation in tackling global cybercrime networks.
Cyber Security News Tags:bulletproof hosting, cyber security, Cybercrime, DoJ, FBI, indictment, Operation Riptide, Russian nationals, Sanctions, US Department of Justice

Post navigation

Previous Post: Hackers Exploit Claude AI and Google Ads to Spread MacSync Stealer
Next Post: FaceTime Exploited in New Bank Impersonation Scam

Related Posts

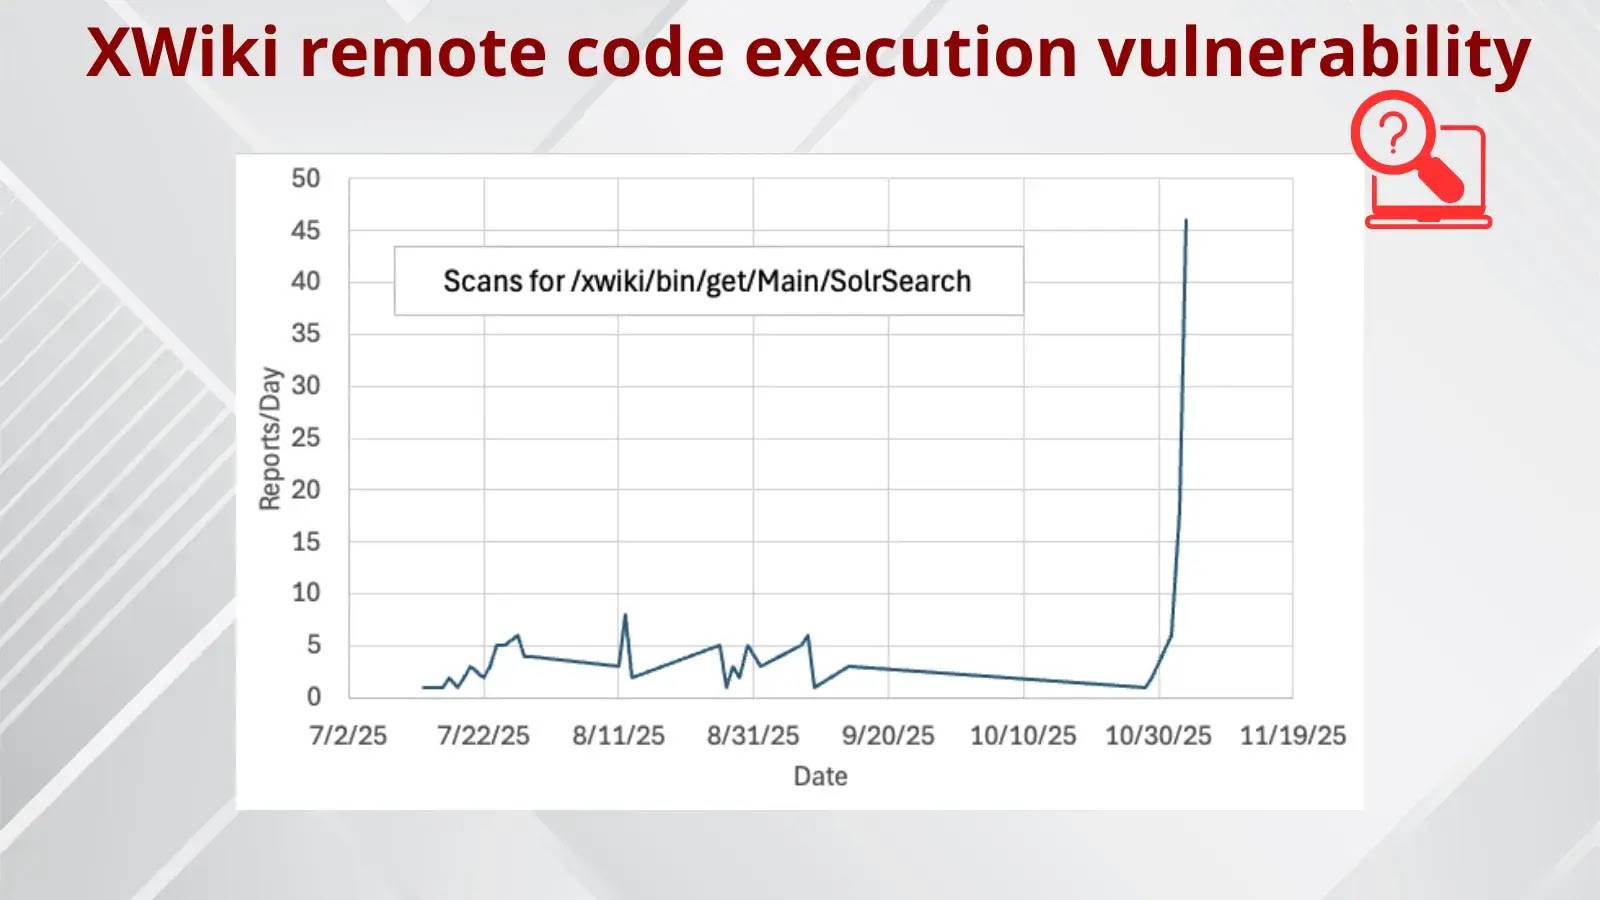
Hackers Actively Scanning Internet to Exploit XWiki Remote Code Execution Vulnerability Hackers Actively Scanning Internet to Exploit XWiki Remote Code Execution Vulnerability Cyber Security News
DigiCert Breach Exposes EV Code Signing Vulnerabilities DigiCert Breach Exposes EV Code Signing Vulnerabilities Cyber Security News
Notepad++ DLL Hijacking Vulnerability Let Attackers Execute Malicious Code Notepad++ DLL Hijacking Vulnerability Let Attackers Execute Malicious Code Cyber Security News
Anthropic’s MCP Server Vulnerability Let Attackers Escape Server’s Sandbox and Execute Arbitrary Code Anthropic’s MCP Server Vulnerability Let Attackers Escape Server’s Sandbox and Execute Arbitrary Code Cyber Security News
Microsoft Confirms Teams Outage for Users, Investigation Underway Microsoft Confirms Teams Outage for Users, Investigation Underway Cyber Security News
Recurring Supply‑Chain Lapses Expose UEFI Firmware to Pre‑OS Threats Recurring Supply‑Chain Lapses Expose UEFI Firmware to Pre‑OS Threats Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • KGB RAT Evades Detection to Compromise Windows PCs
  • New Fixes for AhsayCBS Vulnerabilities to Stop Attacks
  • Online Ads Pose Spyware Threat Without User Interaction
  • Critical Linux Kernel Flaw Exposes Host Memory to Virtual Machines
  • Chinese Phishing Network Targets Global Organizations

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • KGB RAT Evades Detection to Compromise Windows PCs
  • New Fixes for AhsayCBS Vulnerabilities to Stop Attacks
  • Online Ads Pose Spyware Threat Without User Interaction
  • Critical Linux Kernel Flaw Exposes Host Memory to Virtual Machines
  • Chinese Phishing Network Targets Global Organizations

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark