Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
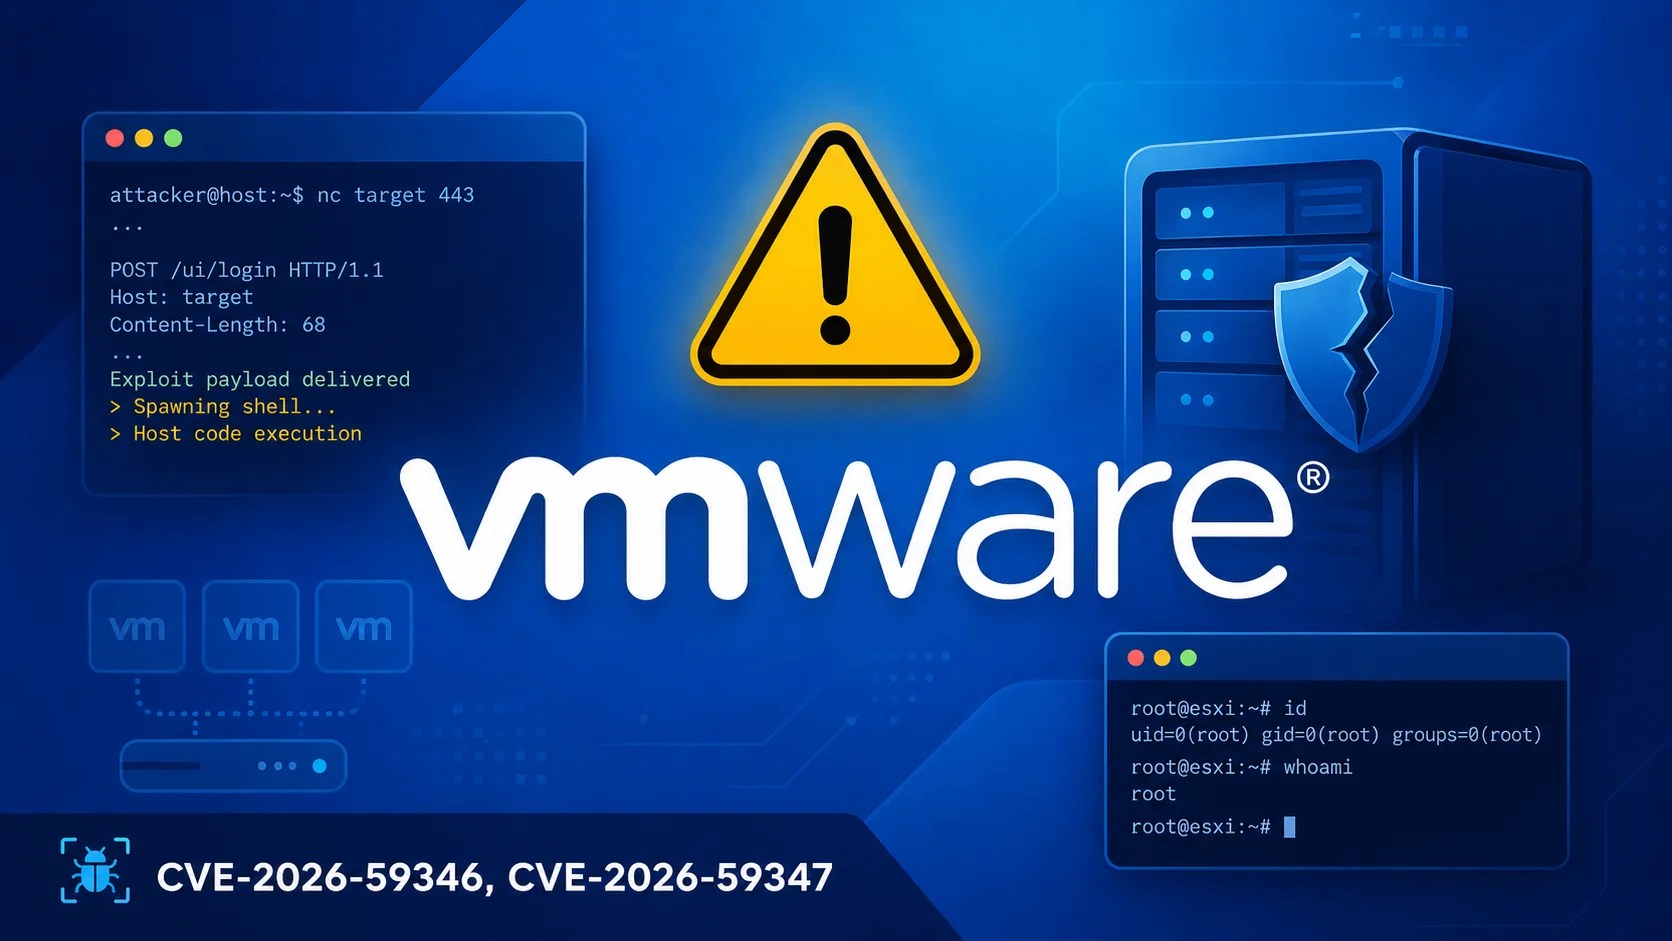
VMware Vulnerabilities Allow Host Code Execution

VMware Vulnerabilities Allow Host Code Execution

Posted on September 3, 2026 By CWS

Broadcom has issued a crucial security advisory concerning two recently identified vulnerabilities in VMware Workstation and Fusion. These flaws pose a significant risk as they enable attackers to escape from a virtual machine (VM) and execute malicious code on the underlying host system. This development challenges the fundamental security assurances provided by virtualization technology.

Details of the Security Flaws

The advisory, labeled VMSA-2026-0007 and released on September 3, 2026, highlights two vulnerabilities affecting VMware’s desktop virtualization solutions. The more critical of the two, CVE-2026-59346, involves an integer-overflow issue in the VMXNET3 network adapter. This flaw has been assigned a CVSSv3 score of 9.3, indicating its critical severity.

As outlined in the advisory, an attacker with local administrative rights on a VM that uses a VMXNET3 adapter can exploit this flaw to run code on the host machine. This allows the attacker to breach the VM’s sandboxed environment.

Understanding the Second Vulnerability

The second vulnerability, CVE-2026-59347, is a stack-based buffer overflow in the Host-Guest File System (HGFS), which manages shared folders between a VM and the host. This flaw has a CVSSv3 score of 8.1 and is considered important rather than critical. Exploiting it enables an attacker with administrative access within a guest VM to execute code as the VMX process on the host, thus gaining unauthorized access to host-level operations.

These vulnerabilities were reported to Broadcom by independent research teams, rather than being identified through public exploitation. CVE-2026-59346 was reported by h4urek of secsys lab and researchers Y² and Stan S through Trend Micro’s Zero Day Initiative. CVE-2026-59347 was reported by Yeonghyeon Choi and Tianchu Chen from Tencent’s Xuanwu Lab.

Impact and Mitigation Measures

The vulnerabilities impact VMware Workstation versions 25H2 and 26H1 on any host OS, and VMware Fusion versions 25H2 and 26H1 on macOS. Broadcom has released version 26H1u1 to address these flaws. Notably, no workarounds are available, making the patch essential for protection.

Given that these vulnerabilities only necessitate local administrative rights within a guest VM to compromise the host, it is imperative for security teams using VMware Workstation or Fusion in testing or malware-analysis environments to prioritize this update.

Virtualization platforms are integral for isolating untrusted code, and a breach of this nature could allow attackers to move from a contained environment into production systems. Administrators should immediately upgrade to version 26H1u1 and review which VMs utilize VMXNET3 adapters or shared folder functionalities.

In conclusion, ensuring timely updates is critical to mitigate risks associated with these vulnerabilities and maintain the integrity of virtualization infrastructure.
Cyber Security News Tags:Broadcom, CVE-2026-59346, CVE-2026-59347, Cybersecurity, Fusion, HGFS, host code execution, Patch, Security, Virtualization, VMware, VMXNET3, Vulnerabilities, Workstation

Post navigation

Previous Post: AIR Security Unveils AI Firewall with $50M Funding
Next Post: US Leads in Global Phishing Scheme Targeting 46 Nations

Related Posts

Google Cloud and Cloudflare Suffers Massive Widespread Outages Google Cloud and Cloudflare Suffers Massive Widespread Outages Cyber Security News
Hundreds of GitHub Malware Repos Targeting Novice Cybercriminals Linked to Single User Hundreds of GitHub Malware Repos Targeting Novice Cybercriminals Linked to Single User Cyber Security News
WAFs protection Bypassed to Execute XSS Payloads Using JS Injection with Parameter Pollution WAFs protection Bypassed to Execute XSS Payloads Using JS Injection with Parameter Pollution Cyber Security News
Chrome Vulnerabilities Let Attackers Execute Malicious Code Remotely Chrome Vulnerabilities Let Attackers Execute Malicious Code Remotely Cyber Security News
Ghostwriter Hackers Target Gmail with Phishing Emails Ghostwriter Hackers Target Gmail with Phishing Emails Cyber Security News
Pulsar RAT Using Memory-Only Execution & HVNC to Gain Invisible Remote Access Pulsar RAT Using Memory-Only Execution & HVNC to Gain Invisible Remote Access Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Urgent Patch for Major Check Point Vulnerability Released
  • Google Fixes Pixel Zero-Day Vulnerability Amid Attacks
  • Russian Enterprises Face Threats from Cyber Groups
  • TP-Link Camera Vulnerabilities Threaten User Privacy
  • AI-Driven Data Breach Notified to Spanish Authorities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Urgent Patch for Major Check Point Vulnerability Released
  • Google Fixes Pixel Zero-Day Vulnerability Amid Attacks
  • Russian Enterprises Face Threats from Cyber Groups
  • TP-Link Camera Vulnerabilities Threaten User Privacy
  • AI-Driven Data Breach Notified to Spanish Authorities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark