Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
VS Code Extension Security Flaw Exposes Files Outside Workspaces

VS Code Extension Security Flaw Exposes Files Outside Workspaces

Posted on November 16, 2026 By CWS

Security experts have identified a vulnerability in the Claude Code extension for Visual Studio Code that can potentially expose files located outside the designated trusted workspaces. This extension, widely used with over 29 million installations, was found to display misleading permission prompts, making it difficult for users to determine the actual location of files.

Understanding the Symlink Vulnerability

The issue revolves around symlinks, which are shortcuts that point to files or folders elsewhere. In tests, a directory named ./helpdocs within the workspace was linked to an external location. When attempting to write a file, the permission prompt only displayed the workspace path, not indicating that the file was outside the trusted area.

This flaw is not new; it has been previously detected in the command-line version of Claude Code. Despite Anthropic addressing a similar display flaw in past iterations, the VS Code extension remains vulnerable, as highlighted by researcher Carl Pearson in his November 2026 report.

Consequences of Misleading Prompts

The symlink issue presents significant risks, especially if a malicious agent exploits it. Attackers could manipulate users into granting access to seemingly safe paths, potentially exposing sensitive information such as SSH keys. The severity of the risk is contingent on the existence of symlinks that lead to sensitive data locations.

Anthropic’s response to this finding has been to categorize the report as informative, asserting that the prompt alone suffices for security. However, this stance has been questioned, as the prompt’s accuracy is crucial for maintaining a secure boundary within workspaces.

Recommended Precautions and Future Outlook

Given the absence of an official patch, developers are advised to manually verify file paths using the realpath command before approving any access requests. This step can help identify if a symlink is redirecting files outside the intended workspace.

Additionally, it is crucial for teams to routinely examine repositories for unexpected symlinks following each synchronization. The emergence of malicious extensions in marketplaces further underscores the importance of vigilance when utilizing such tools.

The reliance on AI tools in development environments emphasizes the need for robust permission controls. As organizations continue to integrate these technologies, addressing these vulnerabilities becomes imperative to safeguard sensitive data and maintain trust in development tools.

Cyber Security News Tags:AI tools, Anthropic, Claude Code, Cybersecurity, developer tools, Extension, Permissions, programming security, Security, software development, source control, Symlink, trusted workspace, versioning, VS Code

Post navigation

Previous Post: Weekly Cybersecurity Recap: Major 0-Day Vulnerabilities Exposed
Next Post: Top Patch Management Solutions for 2026

Related Posts

Critical Cisco IOS XR Vulnerabilities Demand Immediate Attention Critical Cisco IOS XR Vulnerabilities Demand Immediate Attention Cyber Security News
Autonomous AI Agents Pose New Cybersecurity Threats Autonomous AI Agents Pose New Cybersecurity Threats Cyber Security News
Critical Ivanti Endpoint Manager Flaw Raises Security Concerns Critical Ivanti Endpoint Manager Flaw Raises Security Concerns Cyber Security News
New Lawsuit Claims that Meta Can Read All the WhatsApp Users Messages New Lawsuit Claims that Meta Can Read All the WhatsApp Users Messages Cyber Security News
Critical Citrix 0-Day Vulnerability Exploited Since May, Leaving Global Entities Exposed Critical Citrix 0-Day Vulnerability Exploited Since May, Leaving Global Entities Exposed Cyber Security News
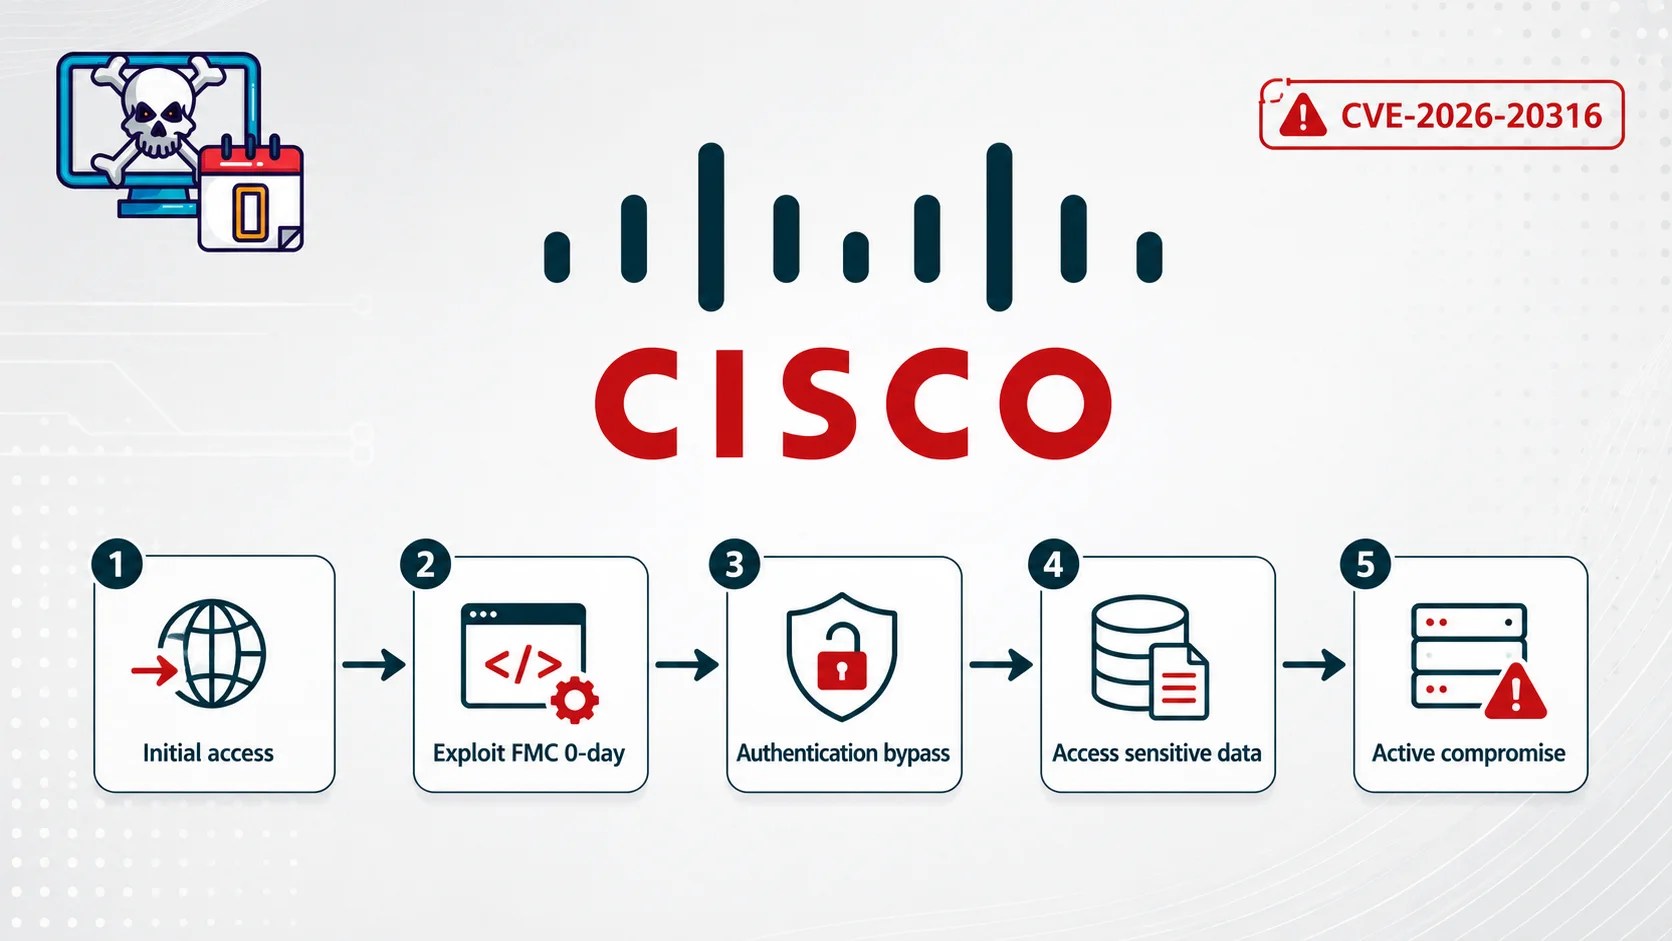
Cisco Urges Update Amid Firewall Vulnerability Exploit Cisco Urges Update Amid Firewall Vulnerability Exploit Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AI-Driven Marketplace Threatens Corporate Security
  • Top Patch Management Solutions for 2026
  • VS Code Extension Security Flaw Exposes Files Outside Workspaces
  • Weekly Cybersecurity Recap: Major 0-Day Vulnerabilities Exposed
  • AI-Powered Cyberattacks Surge, Google Warns

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AI-Driven Marketplace Threatens Corporate Security
  • Top Patch Management Solutions for 2026
  • VS Code Extension Security Flaw Exposes Files Outside Workspaces
  • Weekly Cybersecurity Recap: Major 0-Day Vulnerabilities Exposed
  • AI-Powered Cyberattacks Surge, Google Warns

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark