Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Warlock Ransomware Targets Infrastructure via SharePoint

Warlock Ransomware Targets Infrastructure via SharePoint

Posted on October 1, 2026 By CWS

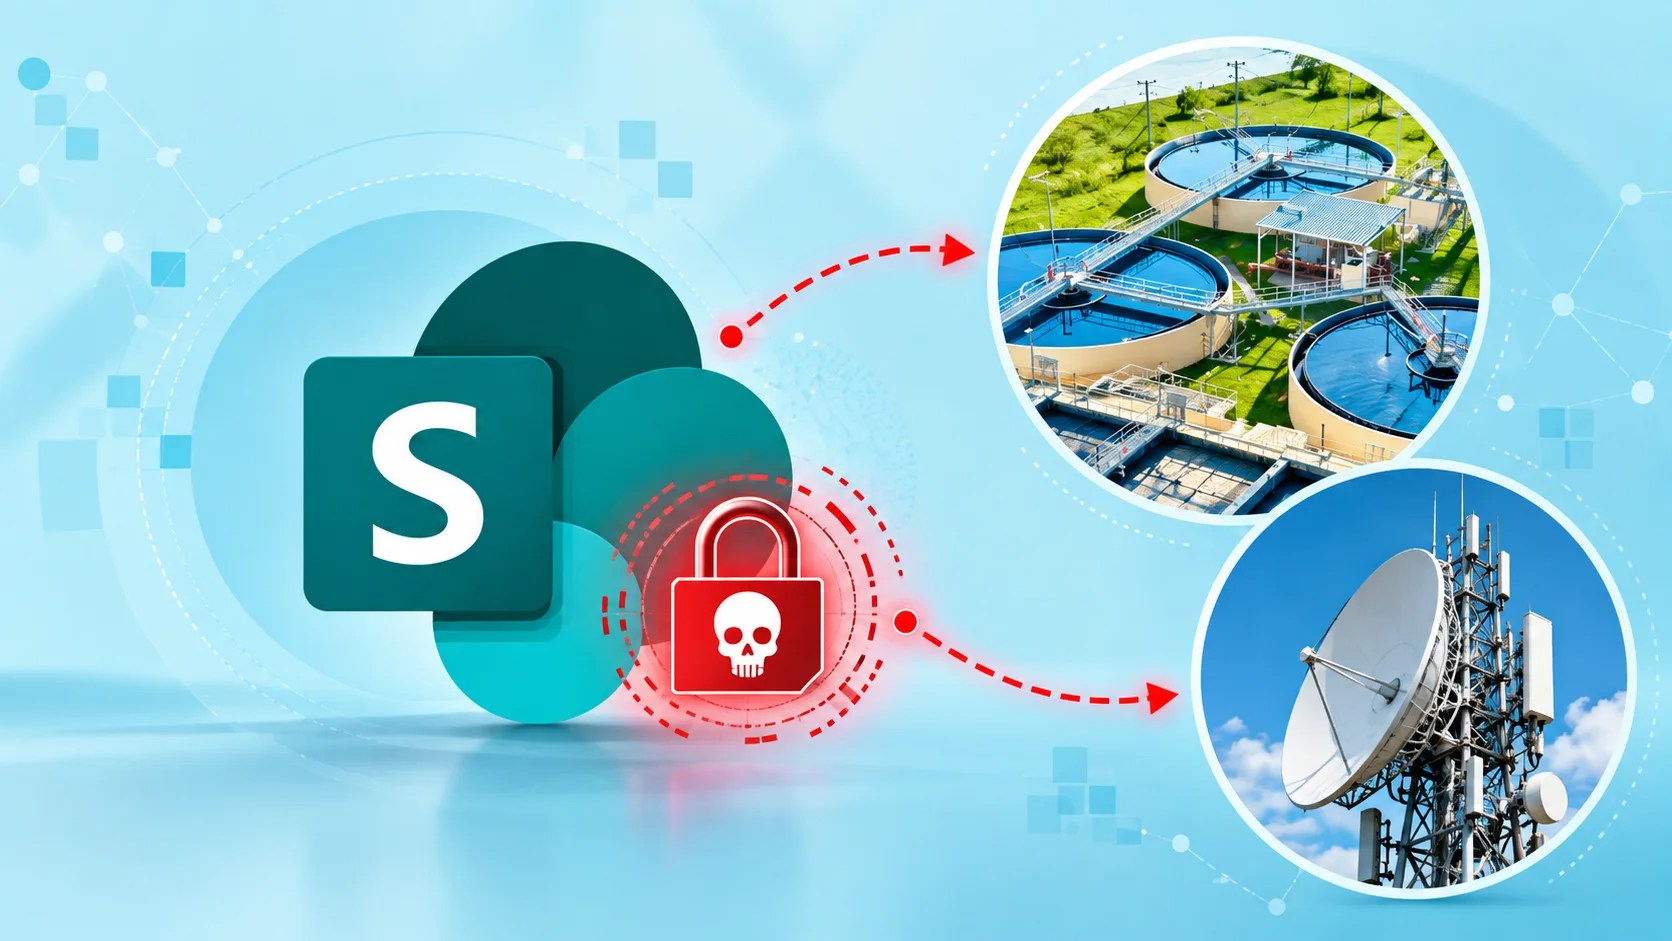
A cyber threat actor linked to China is actively exploiting vulnerabilities in Microsoft SharePoint Server to deploy Warlock ransomware. Recent incidents have impacted vital service providers and public sector entities in regions where Portuguese and Spanish are predominantly spoken.

Threat Actor Activity and Identification

This threat actor, known as Longlegs by Symantec and Storm-2603 by Microsoft, has previously been associated with other aliases like CL-CRI-1040, CamoFei, and ChamelGang. Over the past two months, they have successfully breached at least four organizations, including a water utility, a telecom company, a regional government, and a university across Europe, Africa, and Latin America.

Exploitation of SharePoint Vulnerabilities

The Warlock ransomware first emerged in June 2025, gaining notoriety for its deployment via the SharePoint “ToolShell” exploit chain. This chain includes vulnerabilities identified as CVE-2025-49704 and CVE-2025-49706, with further bypasses tagged as CVE-2025-53770 and CVE-2025-53771. These exploits allow unauthorized access to on-premises SharePoint servers, exposing configurations and enabling remote code execution. Despite patches, newer SharePoint vulnerabilities disclosed in 2026 continue to be exploited.

Technical Details and Defensive Measures

Research by Symantec reveals that Longlegs typically installs an ASPX webshell in the SharePoint LAYOUTS directory to target multiple product versions simultaneously. This webshell extracts ASP.NET machine keys, allowing attackers to craft signed __VIEWSTATE payloads for code execution within the SharePoint application pool. Subsequent malware is introduced via DLL sideloading, with installers sourced from legitimate cloud services like Catbox and Wasabi to camouflage malicious activity.

In a significant breach recorded on July 22, 2026, attackers deployed a webshell on a SharePoint server. They executed commands such as whoami and net user /domain while using NetExec for Active Directory exploration. This attack included deploying Microsoft-signed code-insiders.exe as a service and exploiting Visual Studio Code’s tunnel function for covert access.

Impact and Recommendations

The rapid spread of Warlock ransomware across at least 33 systems underscores the critical nature of cyber defense. Infected systems had files like run.exe, rune.exe, and ransom notes distributed via the SYSVOL share, exploiting the trusted infrastructure to propagate the ransomware. This campaign highlights the inadequacy of patching alone against potential SharePoint exploitations. Security experts advise proactive measures such as hunting for webshells, rotating machine keys, enabling AMSI in Full Mode, and restricting SharePoint’s internet exposure.

For sectors like water, telecom, and government, delayed remediation could lead to widespread operational disruptions. Immediate asset discovery, containment, and recovery planning are essential to counteract these sophisticated threats.

Cyber Security News Tags:CISA warnings, critical infrastructure, Cybersecurity, Longlegs, Malware, network security, public sector, ransomware threats, SharePoint vulnerabilities, Storm-2603, Telecommunications, ToolShell exploit, Warlock ransomware, water utilities

Post navigation

Previous Post: Rob Juncker’s Journey from Hacking to Cybersecurity Leadership
Next Post: Teen Arrested in Spain for Leading Ransomware Group

Related Posts

Critical Microsoft SharePoint Flaw Added to CISA KEV List Critical Microsoft SharePoint Flaw Added to CISA KEV List Cyber Security News
ShinyHunters Takes Responsibility for EY Data Breach ShinyHunters Takes Responsibility for EY Data Breach Cyber Security News
Beware of North Korean Fake Job Platform Targeting U.S. Based AI-Developers Beware of North Korean Fake Job Platform Targeting U.S. Based AI-Developers Cyber Security News
Agenda Ransomware Actors Deploying Linux RAT on Windows Systems Targeting VMware Deployments Agenda Ransomware Actors Deploying Linux RAT on Windows Systems Targeting VMware Deployments Cyber Security News
Hackers Started Exploiting CitrixBleed 2 Vulnerability Before Public PoC Disclosure Hackers Started Exploiting CitrixBleed 2 Vulnerability Before Public PoC Disclosure Cyber Security News
AI ScamAgent Exposes Flaws in Autonomous Scam Prevention AI ScamAgent Exposes Flaws in Autonomous Scam Prevention Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Hackers Exploit Microsoft 365 for Windows Backdoor
  • Police Dismantle KillSec Ransomware, Identify Teen Leader
  • Teen Arrested in Spain for Leading Ransomware Group
  • Warlock Ransomware Targets Infrastructure via SharePoint
  • Rob Juncker’s Journey from Hacking to Cybersecurity Leadership

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Hackers Exploit Microsoft 365 for Windows Backdoor
  • Police Dismantle KillSec Ransomware, Identify Teen Leader
  • Teen Arrested in Spain for Leading Ransomware Group
  • Warlock Ransomware Targets Infrastructure via SharePoint
  • Rob Juncker’s Journey from Hacking to Cybersecurity Leadership

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark