
Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Windows Defender Vulnerability: New Flaw Discovered

Windows Defender Vulnerability: New Flaw Discovered

Posted on September 9, 2026 By CWS

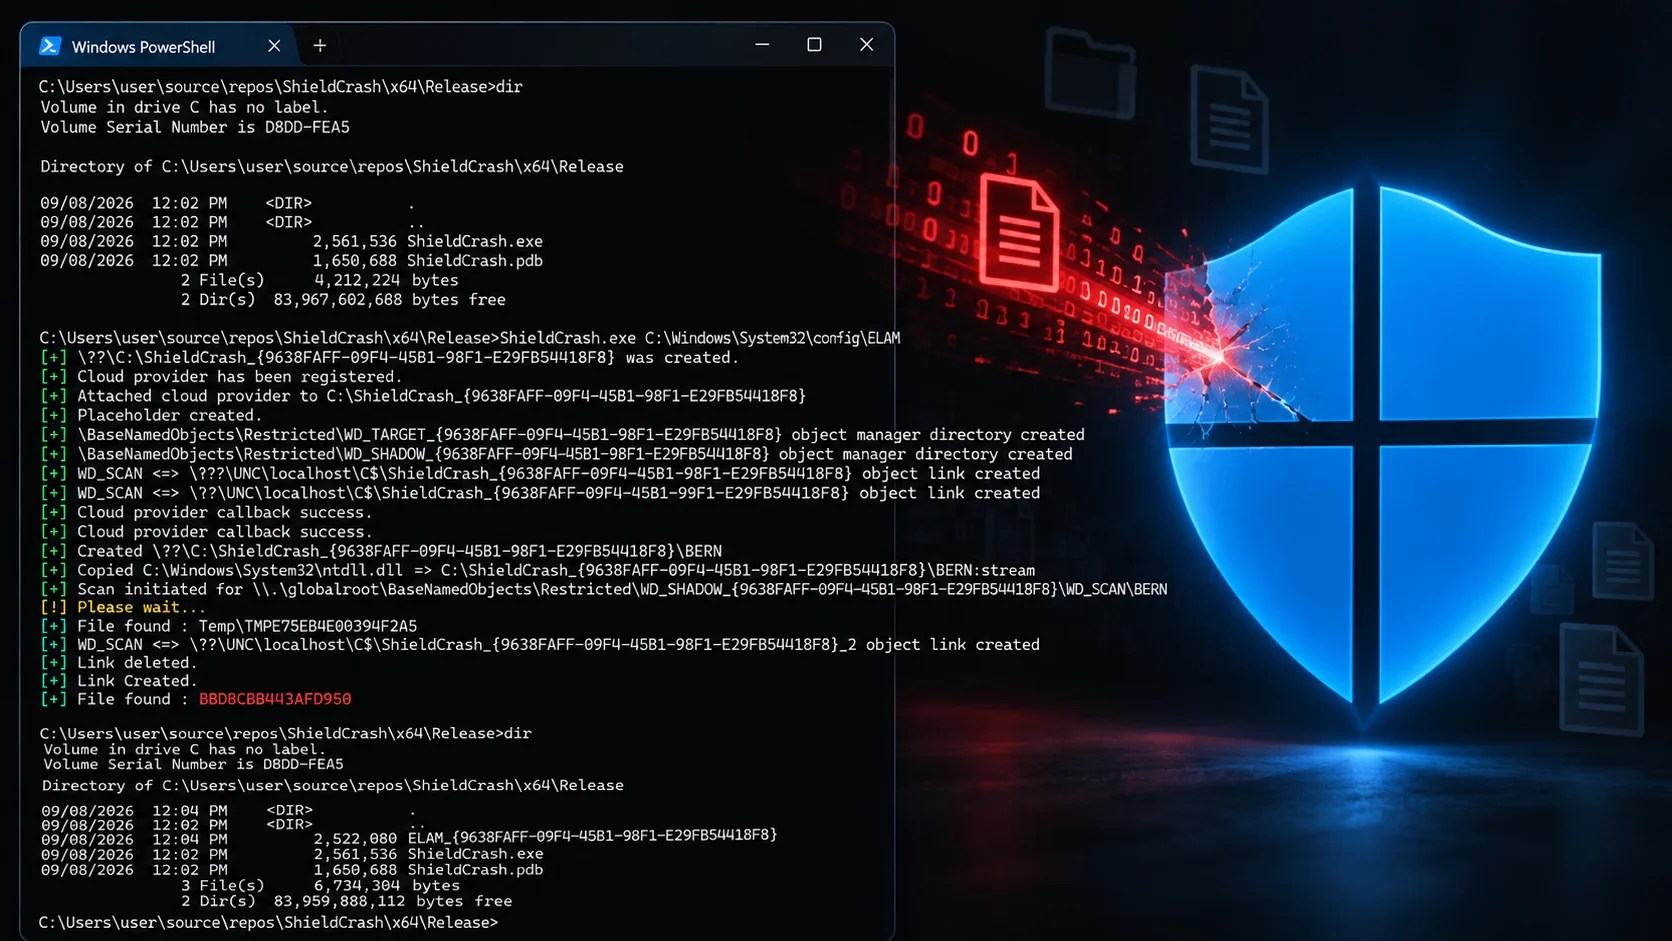
A recent discovery by security researcher MSNightmare has revealed a new vulnerability in Microsoft Defender. Despite a previous patch for the ShieldBreak issue, identified as CVE-2026-69414, a fresh flaw dubbed ShieldCrash allows attackers to access files with SYSTEM-level privileges, posing a significant security risk.

Understanding the New Vulnerability

The vulnerability enables local attackers to manipulate Defender into reading files with elevated SYSTEM privileges on Windows systems that are fully updated and supported. MSNightmare claims that while Microsoft addressed multiple aspects of the original ShieldBreak vulnerability, a specific attack vector was left unpatched, which can recreate the core security issue.

This flaw is particularly concerning because the SYSTEM account on Windows has extensive permissions, surpassing those of regular users and most administrators. Critical system processes and security components typically operate under this account, highlighting the potential for unauthorized data exposure.

Potential Impact of ShieldCrash

The impact of this vulnerability largely depends on the files targeted by an attacker and their ability to retrieve the file contents. Sensitive information at risk includes application configurations, credentials, security settings, private keys, and data from other user accounts on the system.

While the current proof of concept (PoC) demonstrates file reading capabilities as SYSTEM, it does not provide a complete exploit for privilege escalation. The researcher has indicated that further development of the proof of concept might occur, emphasizing that file access alone can still compromise system security.

Precautionary Measures and Future Outlook

Security experts advise against executing untrusted proof-of-concept code on production systems, particularly those interacting with antivirus software or privileged components. Monitoring for unusual activities related to Microsoft Defender, such as unexpected DLL usage or attempts to access protected files, is recommended.

Keeping Microsoft Defender and its security intelligence updates current is crucial. Organizations should promptly apply future patches from Microsoft and enforce application control policies to limit the execution of unauthorized code. As of now, Microsoft has not confirmed this newly reported bypass, which remains under review pending further verification or a security advisory.

To maintain robust security posture, monitoring and proactive measures are essential as the cybersecurity landscape continues to evolve with new threats.

Cyber Security News Tags:Antivirus, CVE-2026-69414, Cybersecurity, file access, Microsoft, MSNightmare, proof-of-concept, security flaw, security patch, ShieldBreak, ShieldCrash, system privileges, Vulnerability, Windows Defender

Post navigation

Previous Post: Ivanti Releases Vital Security Updates for Key Products
Next Post: F5 BIG-IP APM Malware Hides PHP Web Shell in Memory

Related Posts

Bluekit Phishing Kit Revolutionizes Cyber Attacks Bluekit Phishing Kit Revolutionizes Cyber Attacks Cyber Security News
PoisonSeed Phishing Kit Bypasses MFA to Acquire Credentials from Individuals and Organizations PoisonSeed Phishing Kit Bypasses MFA to Acquire Credentials from Individuals and Organizations Cyber Security News
Critical Apache ActiveMQ Flaw Exploited for Ransomware Attack Critical Apache ActiveMQ Flaw Exploited for Ransomware Attack Cyber Security News
Google Forms Exploited in New PureHVNC Malware Attack Google Forms Exploited in New PureHVNC Malware Attack Cyber Security News
Critical Litecoin Flaw Triggers Network Disruption Critical Litecoin Flaw Triggers Network Disruption Cyber Security News
Malicious Bing Ads Exploit AI Interests to Spread Malware Malicious Bing Ads Exploit AI Interests to Spread Malware Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Google AI Features May Influence Targeted Ads
  • LiteLLM Security Breach Exposes GitHub Tokens
  • Brotli Decoder Flaw Impacts Major Software Platforms
  • Security Firm Halts Botnet Threat from Popcorn Time Updater
  • PHP Vulnerabilities Impact Palo Alto PAN-OS Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Google AI Features May Influence Targeted Ads
  • LiteLLM Security Breach Exposes GitHub Tokens
  • Brotli Decoder Flaw Impacts Major Software Platforms
  • Security Firm Halts Botnet Threat from Popcorn Time Updater
  • PHP Vulnerabilities Impact Palo Alto PAN-OS Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark