Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical WooCommerce Flaw Exploited by Hackers

Critical WooCommerce Flaw Exploited by Hackers

Posted on September 15, 2026 By CWS

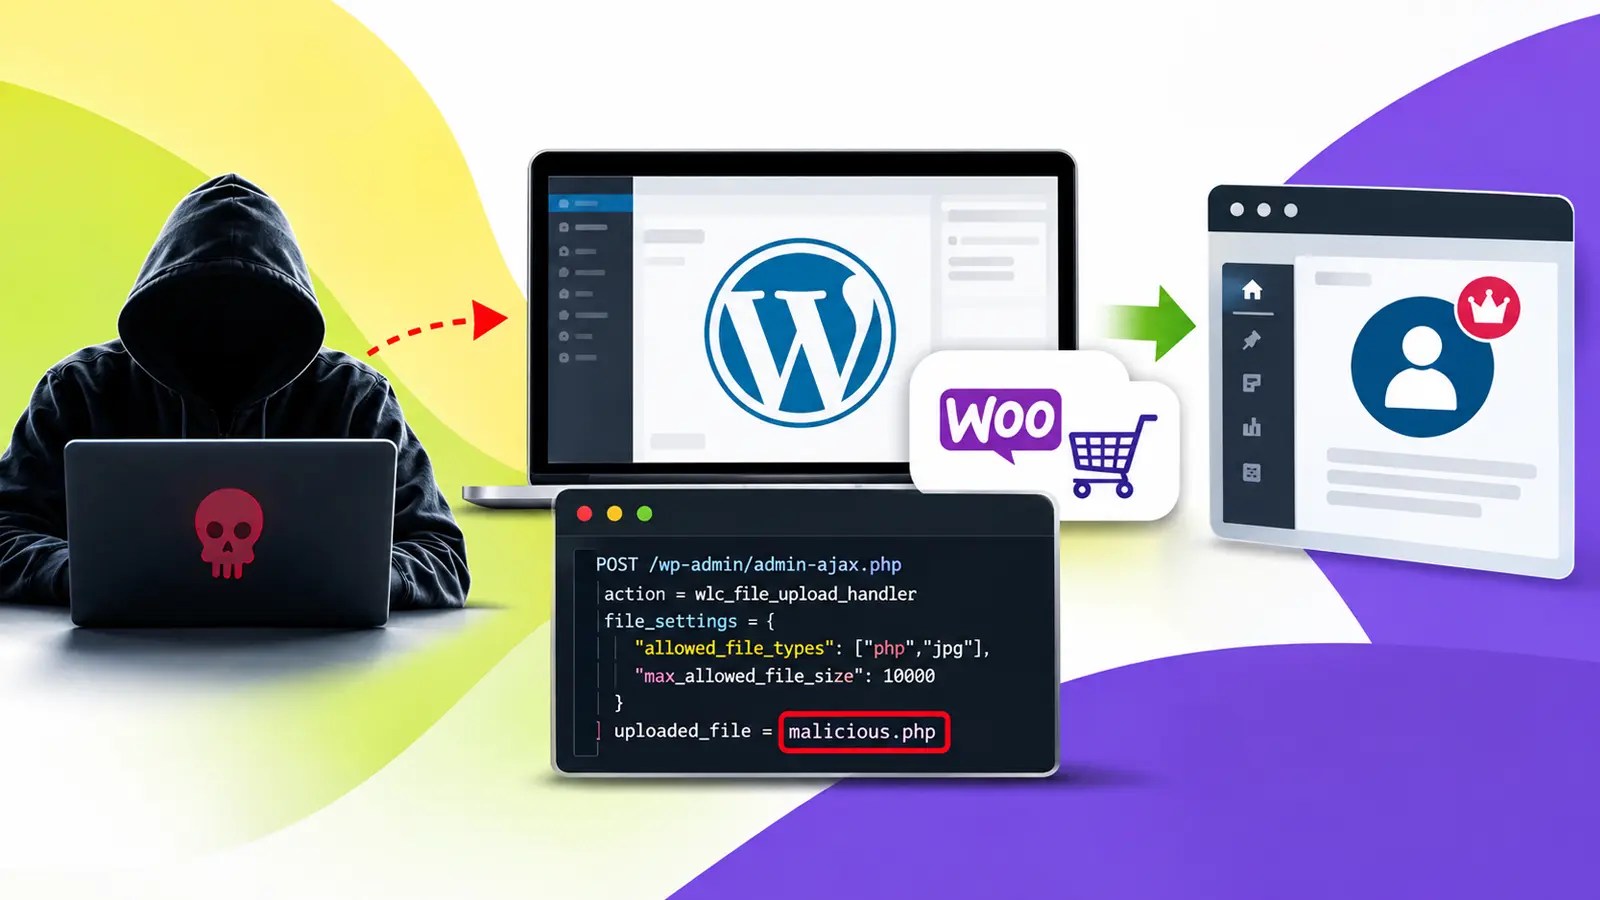
Cybercriminals have identified a significant vulnerability in a WooCommerce plugin, enabling them to gain unauthorized control over WordPress websites. This critical issue, found within the Wholesale Lead Capture extension, allows attackers to bypass login protocols and directly access server functions.

Understanding the Vulnerability

The flaw, designated as CVE-2026-27540, carries a high CVSS severity score of 9.8 and impacts all versions up to 2.0.3.1. This vulnerability allows malicious users to exploit the plugin’s file-upload feature, enabling them to execute malicious code on unprotected websites, potentially compromising them before owners are aware.

Wordfence has observed a significant number of exploit attempts, with over 100,000 cases blocked. These attempts were particularly prevalent during specific periods, notably from June 4 to June 17, and again on July 1 and August 30.

Potential Consequences of Exploitation

Wordfence reports that the compromised plugin is used on approximately 6,000 active sites. Successful breaches could lead to the exposure of sensitive customer data, enable fraudulent transactions, or turn affected sites into platforms for further cyber attacks. The risk underscores the importance of addressing such vulnerabilities promptly.

The loophole is located in the plugin’s file-upload process, which improperly relies on user-supplied information rather than server-secured settings. This allows attackers to upload unauthorized PHP files, granting them remote access to the site.

Mitigation and Future Prevention

To mitigate this threat, users are advised to update the Wholesale Lead Capture plugin to version 2.0.3.2 immediately. Additionally, administrators should conduct thorough reviews of their WordPress installations, ensuring all plugins are up-to-date and monitoring for any signs of unauthorized access.

It’s crucial to inspect server logs for unusual activities and remove any suspicious files. Maintaining verified backups is essential to restore systems without reintroducing vulnerabilities. Developers should enforce strict file-type validations and avoid relying on client-side settings.

Organizations should also assess checkout pages and scheduled tasks for anomalies and ensure logs are preserved for potential investigations. Fast patching and regular security evaluations are vital to safeguarding against known vulnerabilities.

Cyber Security News Tags:CVE-2026-27540, cyber attack, Cybersecurity, Exploit, Malware, plugin vulnerability, website security, WooCommerce, Wordfence, WordPress

Post navigation

Previous Post: Data Breach at Texas Utility CenterPoint Energy Confirmed
Next Post: BambooToken Malware Exploits MQTT to Control Systems

Related Posts

Craneware Confirms Cyberattack, Data Compromised Craneware Confirms Cyberattack, Data Compromised Cyber Security News
Google Unveils AI-Powered CodeMender for Enhanced Security Google Unveils AI-Powered CodeMender for Enhanced Security Cyber Security News
GitHub’s Advisory Database Faces Surge in Vulnerability Reports GitHub’s Advisory Database Faces Surge in Vulnerability Reports Cyber Security News
Global Authorities Share IoCs and TTPs of Scattered Spider Behind Major ESXi Ransomware Attacks Global Authorities Share IoCs and TTPs of Scattered Spider Behind Major ESXi Ransomware Attacks Cyber Security News
Developers Frustrated by ‘No Server Available’ Message Developers Frustrated by ‘No Server Available’ Message Cyber Security News
CISA Red Team Uncovers Security Flaws in Critical Infrastructure CISA Red Team Uncovers Security Flaws in Critical Infrastructure Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical Flaw in Drupal Commerce Threatens Online Stores
  • Scammers Mimic Polymarket to Defraud Cryptocurrency Users
  • Aur0ra Hackers Leverage AI for Domain Admin Access
  • NetamLoader Malware Targets Asian Government Windows 10 Systems
  • Enhancing Security in a Rapidly Evolving Threat Landscape

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical Flaw in Drupal Commerce Threatens Online Stores
  • Scammers Mimic Polymarket to Defraud Cryptocurrency Users
  • Aur0ra Hackers Leverage AI for Domain Admin Access
  • NetamLoader Malware Targets Asian Government Windows 10 Systems
  • Enhancing Security in a Rapidly Evolving Threat Landscape

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark