Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
1,000+ Servers Hit in Law Enforcement Takedown of Rhadamanthys, VenomRAT, Elysium

1,000+ Servers Hit in Law Enforcement Takedown of Rhadamanthys, VenomRAT, Elysium

Posted on November 13, 2025November 13, 2025 By CWS

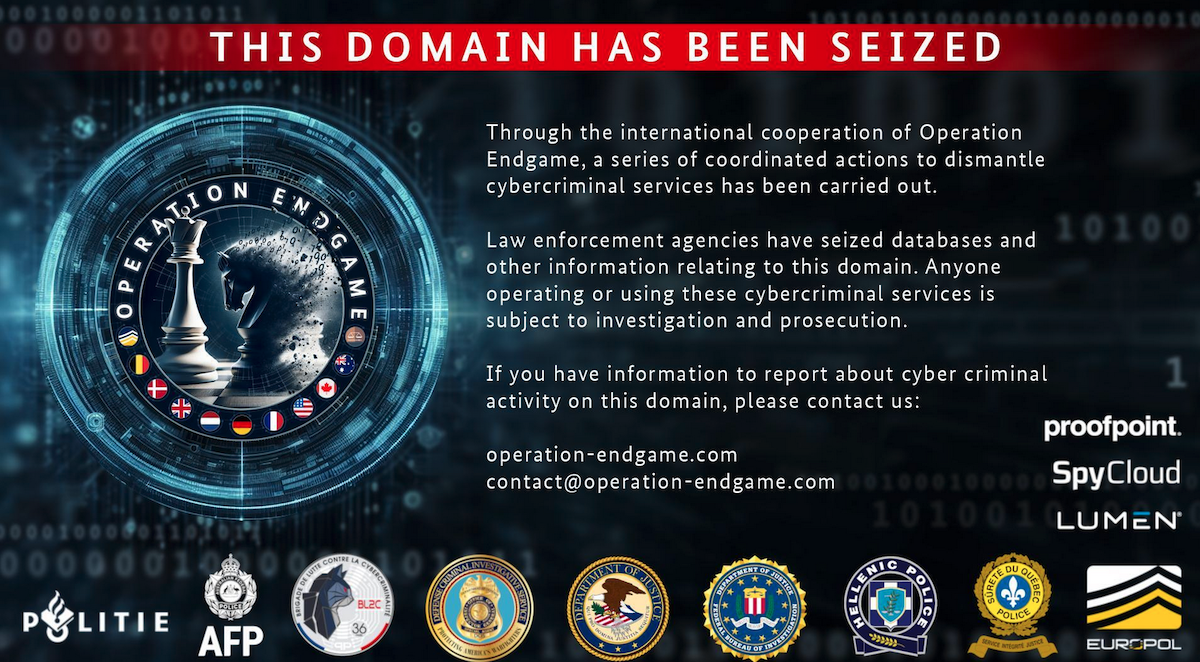
A serious worldwide legislation enforcement operation has dealt a major blow to cybercrime actions involving the Rhadamanthys infostealer, the VenomRAT distant entry trojan, and the Elysium botnet, Europol introduced on Thursday.

The motion, a part of the long-running Operation Endgame, concerned authorities in the USA, Australia, Canada, and eight European international locations, in addition to a number of cybersecurity corporations and non-profit organizations. 

The newest takedown efforts, dubbed Operation Endgame 3.0, have focused Rhadamanthys, VenomRAT, and Elysium, which authorities have described as “three massive cybercrime enablers”.

Legislation enforcement searched 11 places in Germany, Greece, and the Netherlands. One particular person was arrested in Greece over his alleged function within the operation of the VenomRAT malware. 

On the technical aspect, 20 domains had been seized and greater than 1,000 servers worldwide had been disrupted or taken down. 

“The dismantled malware infrastructure consisted of tons of of hundreds of contaminated computer systems containing a number of million stolen credentials,” Europol stated. “Lots of the victims weren’t conscious of the an infection of their methods. The principle suspect behind the infostealer had entry to over 100 000 crypto wallets belonging to those victims, doubtlessly value hundreds of thousands of euros.” 

[ Read: Infostealers: The Silent Smash-and-Grab Driving Modern Cybercrime ]

Police recognized greater than 2 million compromised electronic mail addresses and seven.4 million passwords, which have been shared with the information breach notification service Have I Been Pwned to allow customers to test whether or not they’re impacted by the cybercrime operations. Commercial. Scroll to proceed studying.

In accordance with The Shadowserver Basis, one of many non-profits concerned in Operation Endgame 3.0, Rhadamanthys has been “one of many main infostealers”. Shadowserver has shared some knowledge on Rhadamanthys infections around the globe. 

Associated: Interpol Targets Infostealers: 20,000 IPs Taken Down, 32 Arrested, 216,000 Victims Notified

Associated: Counter Antivirus Service AVCheck Shut Down by Legislation Enforcement

Associated: TrickBot and Different Malware Droppers Disrupted by Legislation Enforcement

Security Week News Tags:Elysium, Enforcement, Hit, Law, Rhadamanthys, Servers, Takedown, VenomRAT

Post navigation

Previous Post: CISA Updates Guidance on Patching Cisco Devices Targeted in China-Linked Attacks
Next Post: MastaStealer Weaponizes Windows LNK Files, Executes PowerShell Command, and Evades Defender

Related Posts

Spur Secures 0M to Enhance IP Intelligence Services Spur Secures $200M to Enhance IP Intelligence Services Security Week News
UEFI Vulnerability in Major Motherboards Enables Early-Boot Attacks UEFI Vulnerability in Major Motherboards Enables Early-Boot Attacks Security Week News
CISA Warns Water Sector of Rising Cyber Threats CISA Warns Water Sector of Rising Cyber Threats Security Week News
OneDrive Gives Web Apps Full Read Access to All Files OneDrive Gives Web Apps Full Read Access to All Files Security Week News
Siemens Notifies Customers of Microsoft Defender Antivirus Issue Siemens Notifies Customers of Microsoft Defender Antivirus Issue Security Week News
WhatsApp Introduces Scam Alert to Enhance Security WhatsApp Introduces Scam Alert to Enhance Security Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark