Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
CISA Warns of Attacks Exploiting N-able Vulnerabilities

CISA Warns of Attacks Exploiting N-able Vulnerabilities

Posted on August 14, 2025August 14, 2025 By CWS

The cybersecurity company CISA is warning organizations that use the N-central distant monitoring and administration (RMM) product from N-able about two just lately patched vulnerabilities being exploited within the wild.

N-central is designed to offer administration, automation, and orchestration capabilities to MSPs and IT groups.

N-able knowledgeable clients on August 13 {that a} new model of the product, 2025.3, features a “vital safety repair” for 2 vulnerabilities tracked as CVE-2025-8875 and CVE-2025-8876. 

“These vulnerabilities require authentication to use. Nevertheless, there’s a potential threat to the safety of your N-central surroundings, if unpatched,” the seller mentioned.

CVE-2025-8875 has been described as an insecure deserialization difficulty, whereas CVE-2025-8876 is a command injection flaw. N-able mentioned particulars shall be made out there after three weeks.

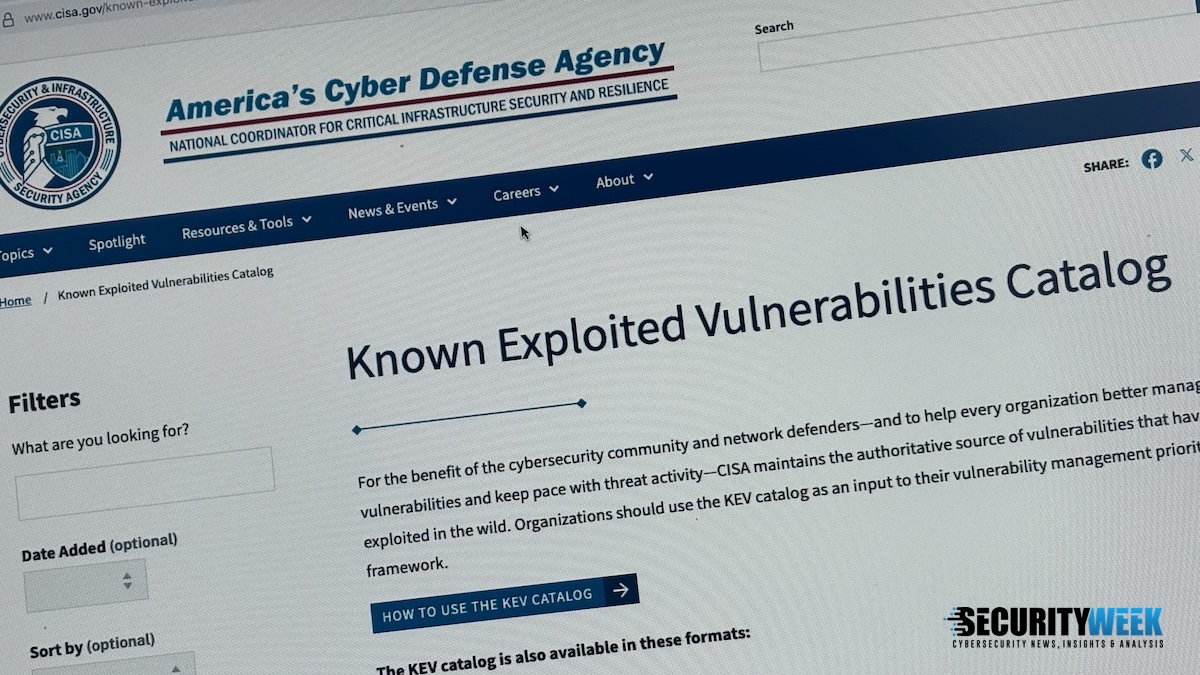
N-able’s advisory doesn’t point out in-the-wild exploitation of the failings, however CISA has added them to its Recognized Exploited Vulnerabilities (KEV) catalog. The company has instructed authorities organizations to patch the safety holes by August 20.

Contemplating that CISA added them to its KEV catalog on the identical day they had been disclosed, and contemplating that no technical data or PoC exploits seem like publicly out there, it’s attainable that the failings have been exploited as zero-days. 

Business professionals have warned that given N-central’s use by MSPs, risk actors may exploit the vulnerabilities to entry MSP clients’ environments. Commercial. Scroll to proceed studying.

It’s price noting that N-able was created in 2021 as a spin-off of SolarWinds, which in 2020 was focused in a high-impact provide chain assault. 

SecurityWeek has reached out to N-able for remark and can replace this text if the corporate responds.

Associated: CISA Warns of SysAid Vulnerability Exploitation

Associated: CitrixBleed 2 Flaw Poses Unacceptable Danger: CISA

Associated: CISA Warns of Two Exploited TeleMessage Vulnerabilities

Security Week News Tags:Attacks, CISA, Exploiting, Nable, Vulnerabilities, Warns

Post navigation

Previous Post: Hackers Using Dedicated Phishlet to Launch FIDO Authentication Downgrade Attacks
Next Post: SmartLoader Malware via Github Repository as Legitimate Projects Infection Users Computer

Related Posts

StrongestLayer Secures .1M to Enhance Email Security StrongestLayer Secures $4.1M to Enhance Email Security Security Week News
UK Student Sentenced to Prison for Selling Phishing Kits UK Student Sentenced to Prison for Selling Phishing Kits Security Week News
Oracle PeopleSoft Vulnerability Exploited by ShinyHunters Oracle PeopleSoft Vulnerability Exploited by ShinyHunters Security Week News
Security Flaw in UK Companies House Web Application Exposed Security Flaw in UK Companies House Web Application Exposed Security Week News
Critical Vulnerability in Arista VeloCloud Exploited Critical Vulnerability in Arista VeloCloud Exploited Security Week News
Cloudflare Tunnels Abused in New Malware Campaign Cloudflare Tunnels Abused in New Malware Campaign Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CrowdStrike Debuts SafeMind: Innovative AI Cybersecurity
  • MikroTik RouterOS Flaw Exploited: Urgent Patch Required
  • Critical Flaw in ASUS Control Center Exposes Systems
  • REVSTEALER Modules Disable Security to Run Crypto Miner
  • MikroTik Routers Vulnerable to Unauthenticated SSH Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CrowdStrike Debuts SafeMind: Innovative AI Cybersecurity
  • MikroTik RouterOS Flaw Exploited: Urgent Patch Required
  • Critical Flaw in ASUS Control Center Exposes Systems
  • REVSTEALER Modules Disable Security to Run Crypto Miner
  • MikroTik Routers Vulnerable to Unauthenticated SSH Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark