Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
CISA Warns of Exploited Apple, Kentico, Microsoft Vulnerabilities

CISA Warns of Exploited Apple, Kentico, Microsoft Vulnerabilities

Posted on October 21, 2025October 21, 2025 By CWS

The US cybersecurity company CISA on Monday warned that not too long ago disclosed vulnerabilities in Home windows SMB Consumer and Kentico Xperience CMS have been exploited within the wild.

The Home windows flaw, tracked as CVE-2025-33073 (CVSS rating of 8.8), was patched in June, when Microsoft warned that proof-of-concept (PoC) exploit code focusing on it existed.

Exploitable over the community, the bug is described as an improper entry management subject that might permit authenticated attackers to raise their privileges to System.

“To take advantage of this vulnerability, an attacker may execute a specifically crafted malicious script to coerce the sufferer machine to attach again to the assault system utilizing SMB and authenticate. This might lead to elevation of privilege,” Microsoft’s advisory reads.

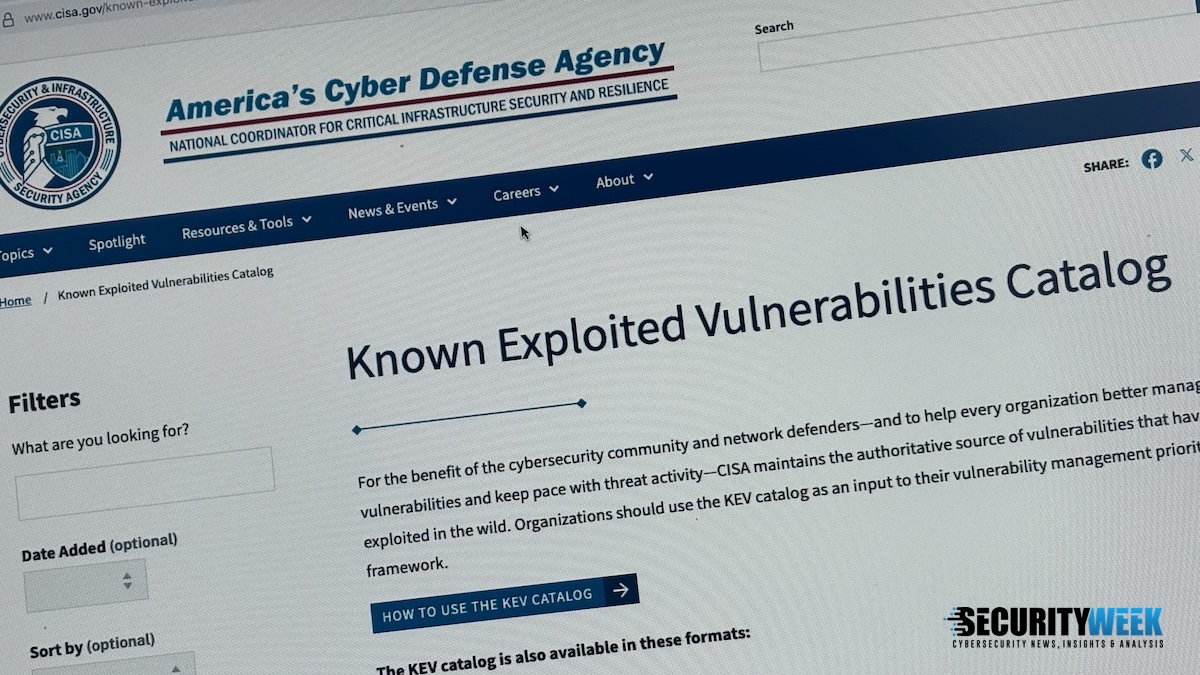
On Monday, CISA added the Home windows SMB defect to its Recognized Exploited Vulnerabilities (KEV) listing together with two authentication bypass flaws within the Kentico Xperience CMS.

The Kentico bugs, tracked as CVE-2025-2746 and CVE-2025-2747 (CVSS rating of 9.6), influence the CMS’s Staging Sync Server password dealing with and will permit attackers to regulate administrative objects.

The 2 vulnerabilities, WatchTowr defined in March, may very well be chained with an authenticated distant code execution defect to compromise Xperience CMS deployments.

CISA on Monday additionally warned that CVE-2022-48503 (CVSS rating of 8.8), an arbitrary code execution subject in Apple merchandise, has been abused within the wild.Commercial. Scroll to proceed studying.

Apple patched the safety gap in July 2022 within the JavaScriptCore element of macOS Monterey 12.5, iOS 15.6, iPadOS 15.6, Safari 15.6, tvOS 15.6, and watchOS 8.7.

Kentico resolved the authentication bypass bugs in Xperience variations 13.0.173 and 13.0.178.

Per Binding Operational Directive (BOD) 22-01, now that the issues had been added to the KEV catalog, federal companies have three weeks to establish weak situations of their environments and apply the obtainable fixes.

There don’t seem like any reviews of those bugs’ exploitation previous to CISA’s warning.

Associated: CISA Confirms Exploitation of Newest Oracle EBS Vulnerability

Associated: Over 73,000 WatchGuard Firebox Gadgets Impacted by Current Important Flaw

Associated: Gladinet Patches Exploited CentreStack Vulnerability

Associated: Organizations Warned of Exploited Adobe AEM Varieties Vulnerability
Security Week News Tags:Apple, CISA, Exploited, Kentico, Microsoft, Vulnerabilities, Warns

Post navigation

Previous Post: New LOSTKEYS Malware Linked to Russia State-Sponsored Hacker Group COLDRIVER
Next Post: CISA Warns Of Oracle E-Business Suite SSRF Vulnerability Actively Exploited In Attacks

Related Posts

Docker Makes 1,000 Hardened Images Free and Open Source Docker Makes 1,000 Hardened Images Free and Open Source Security Week News
Massachusetts Hospital Faces Cyberattack, Diverts Ambulances Massachusetts Hospital Faces Cyberattack, Diverts Ambulances Security Week News
Urgent Patch Needed for Cleo Harmony Security Flaw Urgent Patch Needed for Cleo Harmony Security Flaw Security Week News
Google Enhances Vertex AI Security After AI Agent Risks Exposed Google Enhances Vertex AI Security After AI Agent Risks Exposed Security Week News
AppSignal Raises  Million for Application Monitoring Solution AppSignal Raises $22 Million for Application Monitoring Solution Security Week News
Trio-Tech Subsidiary Faces Ransomware Attack Impact Trio-Tech Subsidiary Faces Ransomware Attack Impact Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Citrix Faces Critical NetScaler RCE Vulnerabilities
  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Citrix Faces Critical NetScaler RCE Vulnerabilities
  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark