Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Iranian Hackers Implicated in LA Metro Cyberattack

Iranian Hackers Implicated in LA Metro Cyberattack

Posted on May 27, 2026 By CWS

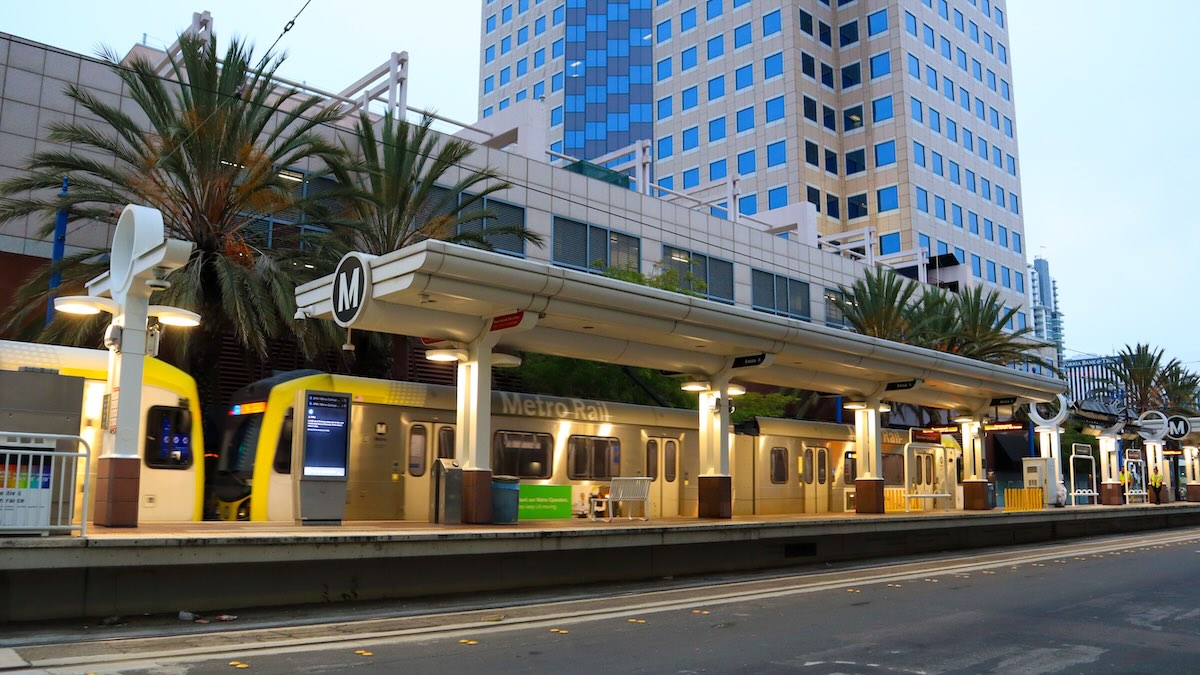
The Los Angeles County Metropolitan Transportation Authority (LACMTA) recently faced a significant cybersecurity breach, attributed to hackers linked with the Iranian government. The attack, identified in mid-March, affected internal operations, though it left rail and bus services unaffected.

Extent of the Cyber Breach

Following the breach, LA Metro officials conducted thorough checks on hundreds of servers to identify any signs of compromise before they could be safely reactivated. Early in April, it was revealed that a group called Ababil of Minab, claiming to be pro-Iranian hacktivists, was behind the cyberattack. The group allegedly wiped substantial amounts of data and extracted over 1 terabyte of files.

Ababil of Minab demonstrated their breach of LA Metro’s systems by sharing screenshots and videos, showcasing access to various internal platforms. These included a core virtualization management platform, a Microsoft IIS web server hosting both internal and public-facing assets, and an operational technology system monitoring train operations.

Analysis and Attribution

According to Dataminr, a threat and risk intelligence firm, Ababil of Minab is a relatively new entity with minimal public history in prior intelligence reports, making it challenging to conclusively assess their capabilities or intentions. Meanwhile, Israeli cyber resilience company Gambit conducted an analysis, finding connections between Ababil of Minab and infrastructure previously linked to Iranian state-sponsored hackers.

Gambit’s investigation suggests that Ababil of Minab is not an independent group as they claim. Instead, forensic evidence indicates a connection to Black Shadow, a group linked to Iran’s Ministry of Intelligence and Security, according to the Israel National Cyber Directorate.

Impact and Future Implications

The attacks attributed to Ababil of Minab have extended beyond LA Metro, targeting organizations in the United States, Israel, Saudi Arabia, and Turkey. These attacks typically involved data exfiltration, and in some cases, destructive activities. Notable victims include entities from various sectors, such as media, education, insurance, and digital services.

The implications of this cyberattack are significant, highlighting ongoing cyber threats from state-linked actors. As investigations continue, further insights into the capabilities and motives of such groups may emerge, prompting enhanced cybersecurity measures across critical infrastructure sectors.

As the threat landscape evolves, organizations must remain vigilant and proactive in fortifying their cybersecurity defenses to counteract potential breaches from sophisticated actors.

Security Week News Tags:Ababil of Minab, Black Shadow, cyber threat, Cyberattack, Cybersecurity, data breach, Dataminr, Gambit, hacktivist group, Iranian government, Iranian hackers, LA Metro, public transportation

Post navigation

Previous Post: Cybercriminals Target FIFA World Cup Fans with Fake Sites
Next Post: Grandoreiro Malware Threatens Portuguese and Latin American Banks

Related Posts

Under Armour Looking Into Data Breach Affecting Customers’ Email Addresses Under Armour Looking Into Data Breach Affecting Customers’ Email Addresses Security Week News
160,000 Impacted by Valsoft Data Breach 160,000 Impacted by Valsoft Data Breach Security Week News
CoChat Introduces Platform to Manage Shadow AI Risks CoChat Introduces Platform to Manage Shadow AI Risks Security Week News
Hackers Exploit Vulnerabilities in MiniOrange WordPress Plugin Hackers Exploit Vulnerabilities in MiniOrange WordPress Plugin Security Week News
Fuji Electric HMI Configurator Flaws Expose Industrial Organizations to Hacking Fuji Electric HMI Configurator Flaws Expose Industrial Organizations to Hacking Security Week News
Mobile Security: Verizon Says Attacks Soar, AI-Powered Threats Raise Alarm Mobile Security: Verizon Says Attacks Soar, AI-Powered Threats Raise Alarm Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Windows 11 Update Disrupts Remote Desktop Connectivity
  • Cisco Alerts on Exploited Vulnerability in Email Gateway
  • Optimize MSSP Efficiency by Reducing Tier 1 Bottlenecks
  • SAP Addresses Critical Vulnerabilities in NetWeaver and S/4HANA
  • Microsoft Fixes Record 1,413 Vulnerabilities Including Exploited Bug

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Windows 11 Update Disrupts Remote Desktop Connectivity
  • Cisco Alerts on Exploited Vulnerability in Email Gateway
  • Optimize MSSP Efficiency by Reducing Tier 1 Bottlenecks
  • SAP Addresses Critical Vulnerabilities in NetWeaver and S/4HANA
  • Microsoft Fixes Record 1,413 Vulnerabilities Including Exploited Bug

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark