API key security has become a critical concern for organizations worldwide. The Open Revocable Key Standard (ORKS) has been introduced to address API keys found in public repositories, offering a solution that integrates a built-in self-destruct feature.
The Current Challenge with API Keys
Many security incidents start with exposed API keys in public code repositories, leaving organizations vulnerable to attacks. These keys often remain active for years, posing significant risks as attackers can exploit them rapidly. Despite the existence of standardized solutions like OAuth’s token revocation, API keys have lacked a universal revocation method.
GitHub’s Secret Scanning Partner Program offers a proprietary solution by scanning public commits and revoking keys via webhook, yet it remains limited to specific partners. The open-source community is pushing towards automatic revocation through provider APIs, but the lack of a standard method complicates efforts.
ORKS: A Proposed Solution
The ORKS initiative aims to fill this gap by proposing a standardized way to manage API key revocation. This proposal includes a structured key format, a discoverable revocation endpoint, and declared constraints to ensure better management and security.
Each key under ORKS will include the issuer’s domain, making it easy for any scanner to identify the responsible organization. Revocation is simplified through a JSON file hosted at a well-known URL, detailing revocation and introspection endpoints, security contacts, and key constraints.
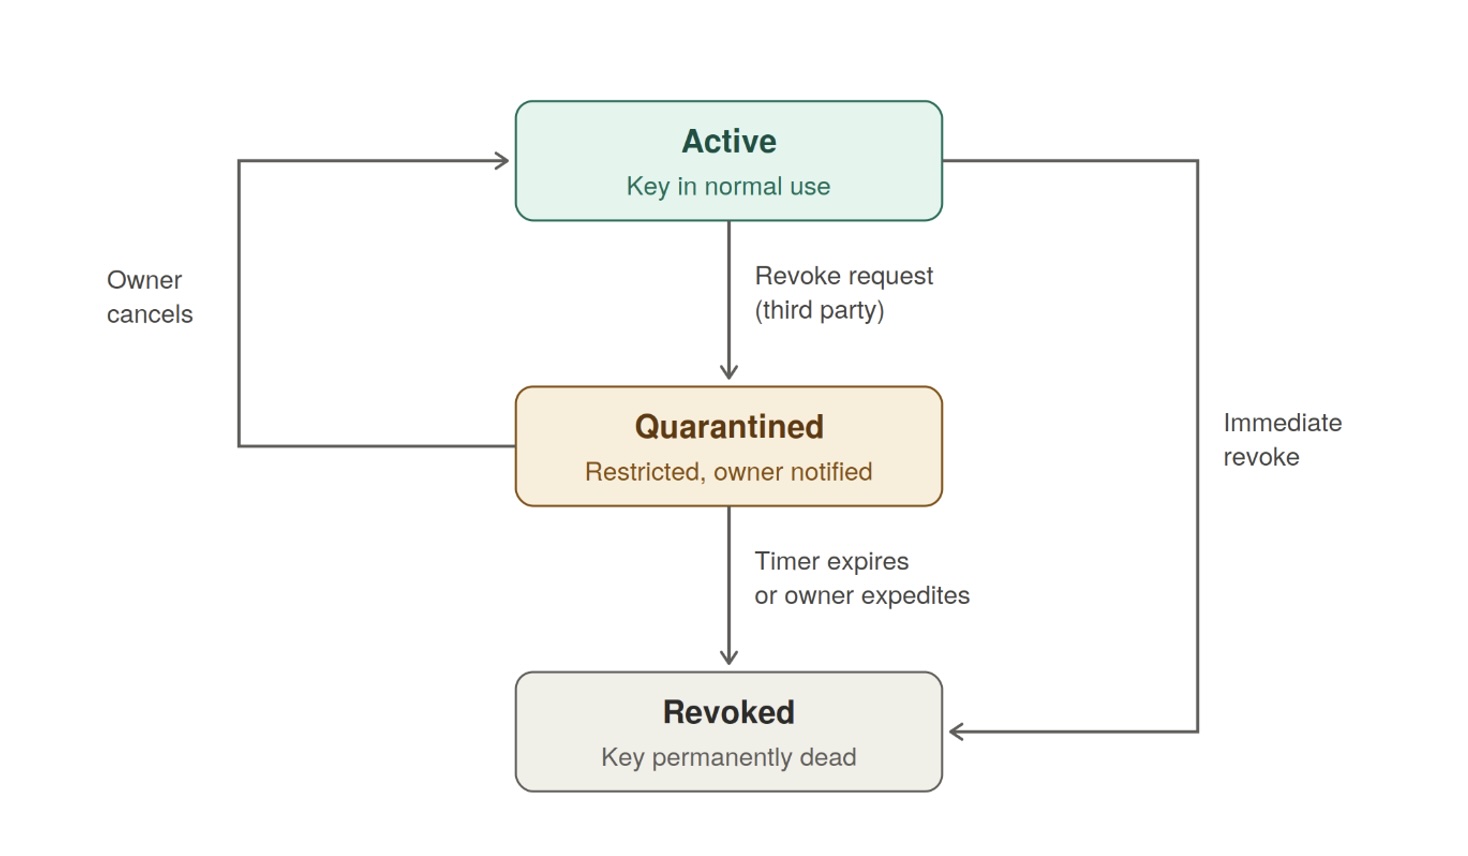
Importantly, ORKS proposes revocation by possession, where submitting the full key to the endpoint can deactivate it without further authentication. This approach prioritizes security by enabling immediate action upon key discovery.
Addressing Modern Security Challenges
ORKS is designed to accommodate the evolving landscape of API security, particularly with the rise of autonomous AI agents. These agents hold multiple keys, increasing the risk of leaks. ORKS provides a machine-readable interface for systems to automatically handle key revocation, crucial for minimizing the window between compromise and remediation.
The standard allows for constraints such as IP restrictions and limited key lifetimes, offering a safeguard against misuse. Moreover, agents can be configured to revoke their own keys once a task is complete, ensuring minimal exposure.
Future Implications and Adoption
ORKS offers a decentralized approach, enabling providers to adopt it independently by implementing key prefixes, a static JSON configuration file, and a revocation endpoint. This simplicity encourages widespread adoption, potentially transforming API key security practices.
The proposed standard envisions a future where API keys are no longer a weak point in security. Developers and organizations are encouraged to review the ORKS draft specification available on GitHub and provide feedback or contributions to refine and enhance the standard.
The adoption of ORKS could lead to a paradigm shift in how API keys are managed, making them more secure and manageable. Implementing ORKS could significantly reduce the risks associated with leaked keys, ensuring a more robust security posture for organizations relying on API integrations.