Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Ransomware Group Claims Attack on Belk

Ransomware Group Claims Attack on Belk

Posted on July 15, 2025July 15, 2025 By CWS

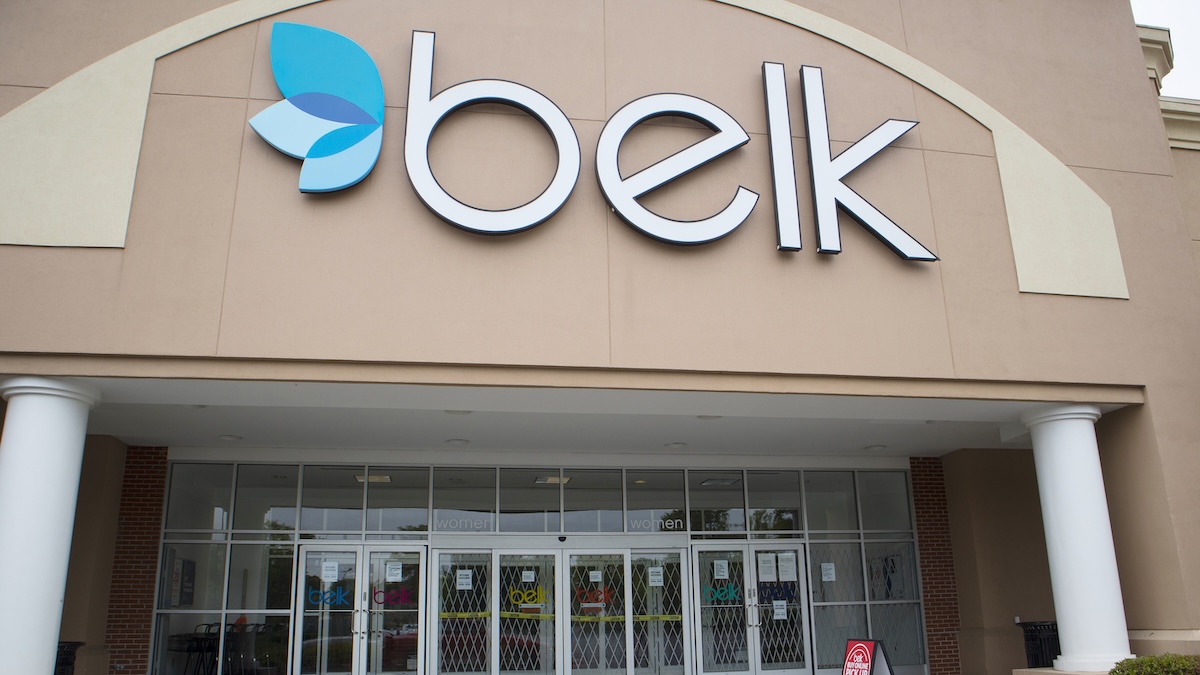
The DragonForce ransomware gang has claimed duty for a disruptive cyberattack on US division retailer chain Belk.

The incident was recognized on Could 8 and prompted Belk to disconnect affected methods, prohibit community entry, reset passwords, and rebuild impacted methods, which disrupted the chain’s on-line and bodily operations for a number of days. The corporate’s on-line retailer continues to be offline on the time of publication.

Belk’s investigation into the assault decided that hackers had entry to its community between Could 7 and Could 11, and that they exfiltrated sure paperwork, together with recordsdata containing private data.

In a knowledge breach notification submitted to the New Hampshire Legal professional Common’s Workplace, Belk mentioned at the very least names and Social Safety numbers have been compromised within the assault.

The corporate is offering the impacted people with 12 months of free credit score monitoring and id restoration providers, which additionally embody as much as $1 million id theft insurance coverage.

The corporate has not named the group answerable for the assault, however the DragonForce ransomware gang has claimed the incident on Monday, including Belk to its Tor-based leak website.

DragonForce says it exfiltrated 156 gigabytes of knowledge from the division retailer chain, and has made all of it accessible for obtain, which means that Belk didn’t pay a ransom.

Energetic since at the very least December 2023, DragonForce is a ransomware-as-a-service (RaaS) operation that supposedly hit round 210 organizations, albeit solely 38 incidents have been confirmed to this point.Commercial. Scroll to proceed studying.

The hacking group made headlines not too long ago, after a collection of disruptive assaults on UK retail chains like Co-op, Harrods, and Marks & Spencer. These assaults have been linked to the infamous Scattered Spider cybercrime group. 

Based within the late 1800s in Monroe, North Caroline, Belk operates over 300 department shops throughout 16 states, together with an internet retailer, providing attire, equipment, cosmetics, sneakers, house furnishings, and a marriage registry.

Associated: Ingram Micro Restores Techniques Impacted by Ransomware

Associated: Chain IQ, UBS Information Stolen in Ransomware Assault

Associated: DragonForce Ransomware Hackers Exploiting SimpleHelp Vulnerabilities

Associated: US Insurance coverage Business Warned of Scattered Spider Assaults
Security Week News Tags:Attack, Belk, Claims, Group, Ransomware

Post navigation

Previous Post: North Korean Hackers Flood npm Registry with XORIndex Malware in Ongoing Attack Campaign
Next Post: Zip Security Raises $13.5 Million in Series A Funding

Related Posts

All SonicWall Cloud Backup Users Had Firewall Configurations Stolen All SonicWall Cloud Backup Users Had Firewall Configurations Stolen Security Week News
Third DraftKings Hacker Pleads Guilty Third DraftKings Hacker Pleads Guilty Security Week News
AdaptHealth Data Breach Exposes 4.1 Million Records AdaptHealth Data Breach Exposes 4.1 Million Records Security Week News
Microsoft Patches Actively Exploited Windows Kernel Zero-Day Microsoft Patches Actively Exploited Windows Kernel Zero-Day Security Week News
Code Execution Vulnerability Patched in GitHub Enterprise Server Code Execution Vulnerability Patched in GitHub Enterprise Server Security Week News
New Python-Based Malware Deep#Door Targets Windows New Python-Based Malware Deep#Door Targets Windows Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Microsoft SharePoint Vulnerability CVE-2026-65660 Under Attack
  • Unpatched Citrix NetScaler Flaws Pose Security Threat
  • Citrix Faces Critical NetScaler RCE Vulnerabilities
  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Microsoft SharePoint Vulnerability CVE-2026-65660 Under Attack
  • Unpatched Citrix NetScaler Flaws Pose Security Threat
  • Citrix Faces Critical NetScaler RCE Vulnerabilities
  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark