Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Trezor Customer Data Exposed in ShipMonk Breach

Trezor Customer Data Exposed in ShipMonk Breach

Posted on August 14, 2026 By CWS

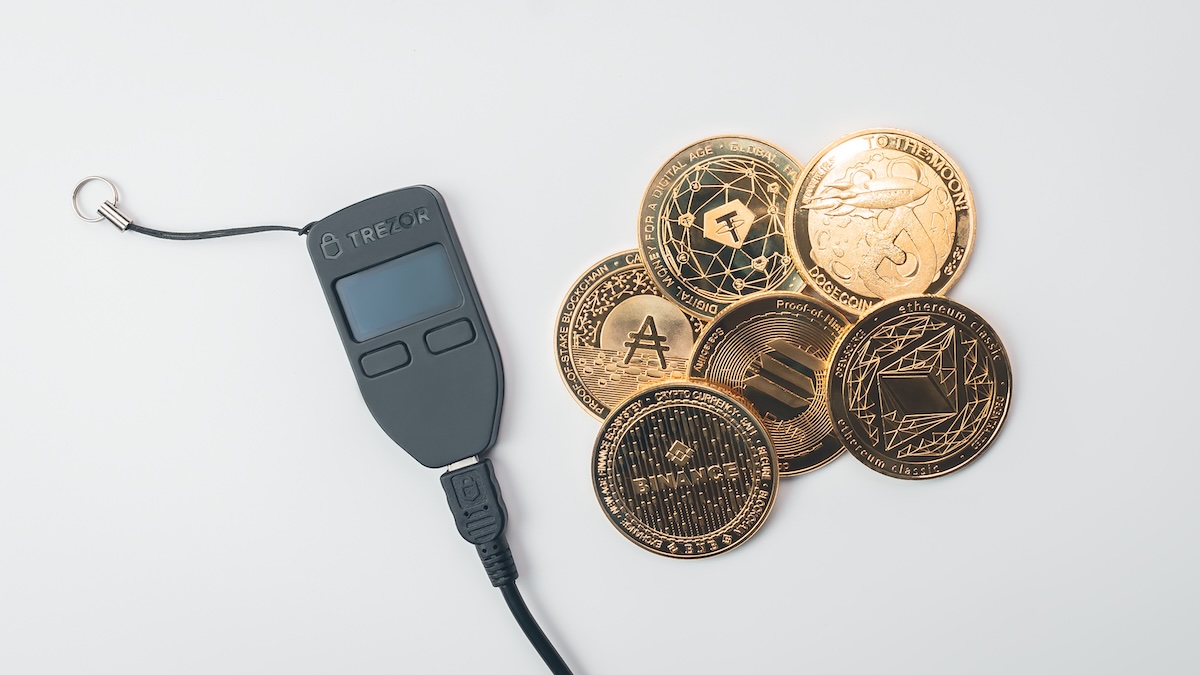
The personal information of nearly 14,000 Trezor customers has been compromised due to a data breach involving their third-party shipping partner, ShipMonk, as reported by Trezor. The breach, which did not affect Trezor’s own systems, was disclosed to the company on August 10.

Details of the Data Breach

Affected customers are from several countries, including the United States, United Kingdom, Sweden, Colombia, Brazil, Italy, and Portugal, who made purchases between May 10 and August 8. Trezor has expressed deep regret for the incident, confirming that the breach involved unauthorized access to full names, phone numbers, email addresses, and shipping details.

In total, hackers obtained the personal information of 11,742 customers, alongside partial data from an additional 1,947 customers. This information was shared with ShipMonk solely for delivery purposes.

Impact and Response

Trezor has assured users that their devices remain secure, emphasizing that only personal data was exposed. However, the company warns that affected customers could face sophisticated phishing attacks. To mitigate the risk, Trezor has contacted all impacted individuals via email, advising vigilance against any suspicious communications.

Despite the breach, Trezor’s strict data retention policy, which limits storage to 90 days, helped contain the extent of the exposure. However, they noted that older orders of the partially affected customers might have been accessed.

Investigation and Security Measures

Currently, Trezor is working closely with ShipMonk to establish a detailed timeline and understand the breach’s full scope. ShipMonk reportedly communicated to its customers that the breach exploited a vulnerability in Metabase, potentially linked to a recently patched SQL injection zero-day flaw.

The attack has been claimed by the notorious ShinyHunters group, who allegedly leaked data from Metabase. While ShipMonk has not publicly addressed the breach, investigations continue to assess the broader impact on other companies and individuals.

As the situation develops, SecurityWeek has reached out to ShipMonk for additional comments and will provide updates as new information becomes available.
Security Week News Tags:crypto wallet, customer data, Cybersecurity, data breach, Metabase, Phishing, ShinyHunters, ShipMonk, SQL injection, Trezor

Post navigation

Previous Post: Aeternum Botnet’s Blockchain Strategy Challenges Security
Next Post: New RAM Exploit Bypasses Windows Security Barriers

Related Posts

Security Flaws in Claude Code Exposed Developer Systems Security Flaws in Claude Code Exposed Developer Systems Security Week News
Louis Vuitton Data Breach Hits Customers in Several Countries Louis Vuitton Data Breach Hits Customers in Several Countries Security Week News
ConductorOne Raises  Million in Series B Funding ConductorOne Raises $79 Million in Series B Funding Security Week News
SafeHill Emerges from Stealth With .6 Million Pre-Seed Funding SafeHill Emerges from Stealth With $2.6 Million Pre-Seed Funding Security Week News
Ivanti Patches Two EPMM Zero-Days Exploited to Hack Customers Ivanti Patches Two EPMM Zero-Days Exploited to Hack Customers Security Week News
In Other News: PromptPwnd Attack, Small macOS Bounties, Chinese Hackers Trained in Cisco Academy In Other News: PromptPwnd Attack, Small macOS Bounties, Chinese Hackers Trained in Cisco Academy Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CISA Alerts on Citrix NetScaler Vulnerabilities Exploitation
  • DC Health Data Breach Affects Nearly 400,000 Records
  • Critical Citrix NetScaler Flaws Exploited Globally, Warns CISA
  • PHP Addresses Security Flaw Exposing Sensitive Data
  • Jury Rules Facebook Misled Users on Privacy in New Mexico

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CISA Alerts on Citrix NetScaler Vulnerabilities Exploitation
  • DC Health Data Breach Affects Nearly 400,000 Records
  • Critical Citrix NetScaler Flaws Exploited Globally, Warns CISA
  • PHP Addresses Security Flaw Exposing Sensitive Data
  • Jury Rules Facebook Misled Users on Privacy in New Mexico

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark