Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Unauthenticated RCE Flaw Patched in DrayTek Routers

Unauthenticated RCE Flaw Patched in DrayTek Routers

Posted on October 3, 2025October 3, 2025 By CWS

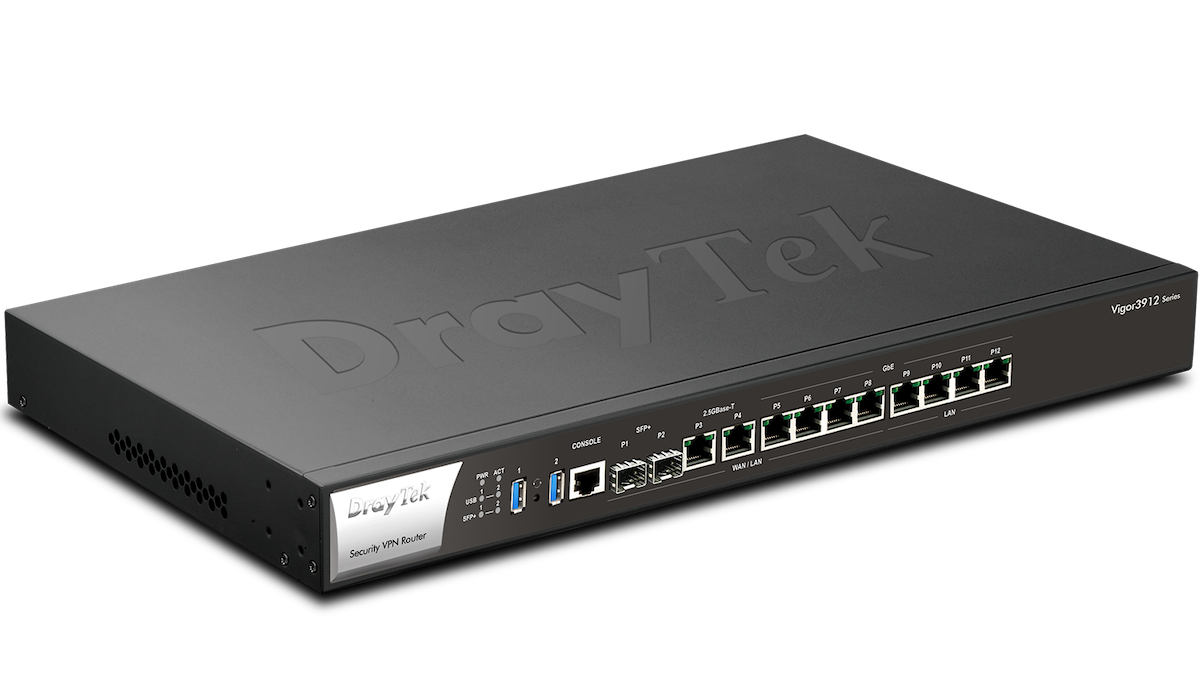
DrayTek on Thursday introduced patches for an unauthenticated distant code execution (RCE) vulnerability affecting DrayOS routers.

Tracked as CVE-2025-10547, the difficulty could be exploited through crafted HTTP or HTTPS requests despatched to a susceptible gadget’s internet consumer interface.

Profitable exploitation of the bug, DrayTek explains in its advisory, might lead to reminiscence corruption and a system crash. In sure circumstances, it might be used to execute arbitrary code remotely, it says.

“Routers are shielded from WAN-based assaults if distant entry to the WebUI and SSL VPN providers is disabled, or if Entry Management Lists (ACLs) are correctly configured,” DrayTek notes.

“Nonetheless, an attacker with entry to the native community might nonetheless exploit the vulnerability through the WebUI. Native entry to the WebUI could be managed on some fashions utilizing LAN facet VLANs and ACLs,” the corporate provides.

The corporate credited ChapsVision safety researcher Pierre-Yves Maes for reporting the vulnerability on July 22.

DrayTek has launched firmware updates that deal with the safety defect in 35 Vigor router fashions, urging customers to replace their gadgets as quickly as potential. Nonetheless, it made no point out of the bug being exploited within the wild.

DrayTek gadgets are broadly utilized by prosumers and SMBs, and are recognized to be widespread targets for hackers. Ransomware teams final yr hit lots of of organizations by exploiting an unknown flaw in DrayTek routers.Commercial. Scroll to proceed studying.

Earlier this yr, widespread Vigor router reboots reported throughout the UK, Australia, and different nations had been blamed on probably malicious TCP connection makes an attempt concentrating on older fashions.

Associated: Organizations Warned of Exploited Meteobridge Vulnerability

Associated: Broadcom Fails to Disclose Zero-Day Exploitation of VMware Vulnerability

Associated: Cisco Patches Zero-Day Flaw Affecting Routers and Switches

Associated: Vulnerabilities Expose Helmholz Industrial Routers to Hacking

Security Week News Tags:DrayTek, Flaw, Patched, RCE, Routers, Unauthenticated

Post navigation

Previous Post: How Passwork 7 Addresses Complexity of Enterprise Security
Next Post: DrayOS Routers Vulnerability Let Attackers Execute Malicious Code Remotely

Related Posts

AI Agents Exploit Supply Chains in New Cyber Attacks AI Agents Exploit Supply Chains in New Cyber Attacks Security Week News
Fraud Prevention Firm Resistant AI Raises  Million Fraud Prevention Firm Resistant AI Raises $25 Million Security Week News
Cybersecurity Leaders Request Easing of AI Model Restrictions Cybersecurity Leaders Request Easing of AI Model Restrictions Security Week News
‘Whisper Leak’ LLM Side-Channel Attack Infers User Prompt Topics ‘Whisper Leak’ LLM Side-Channel Attack Infers User Prompt Topics Security Week News
ShinyHunters-Branded Extortion Activity Expands, Escalates ShinyHunters-Branded Extortion Activity Expands, Escalates Security Week News
Cisco Fixes Critical Security Flaw in Identity Services Cisco Fixes Critical Security Flaw in Identity Services Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers
  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers
  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark