Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Zimbra Servers Under Fire: New Exploit Campaign Detected

Zimbra Servers Under Fire: New Exploit Campaign Detected

Posted on August 20, 2026 By CWS

A critical vulnerability affecting Zimbra Collaboration servers is currently being exploited, as reported by CERT Polska. The flaw, identified as CVE-2026-73570, poses a significant threat to enterprise email and collaboration software users.

Zimbra Vulnerability Details

Recently patched by Zimbra’s development team, the vulnerability was addressed with the release of version 10.1.20 on July 20. The security issue arises when the ‘zimbra-snmp’ package is installed and SNMP notifications are activated, leading to potential exploitation without requiring user authentication.

This allows attackers to execute arbitrary commands on the operating system as the Zimbra user, compromising the security of the affected servers.

Active Exploitation and Indicators

CERT Polska has observed active attacks exploiting this flaw but has not disclosed specific details about the campaign. However, it did provide some indicators of compromise (IoCs) to help organizations identify potential breaches.

The motivation and identity of the attackers remain unknown. Nonetheless, the risk is significant, as successful exploitation can lead to complete server control, allowing intruders to maintain access, gather email credentials, and potentially infiltrate other systems.

Implications and Historical Context

The Cybersecurity and Infrastructure Security Agency (CISA) has not yet added CVE-2026-73570 to its Known Exploited Vulnerabilities (KEV) catalog, which currently lists 18 Zimbra vulnerabilities. Four of these vulnerabilities were added in the current year, underscoring the ongoing risks associated with Zimbra’s software.

Historically, Zimbra vulnerabilities have been exploited by state-sponsored groups, particularly from Russia and China, targeting sensitive intelligence sectors. Additionally, opportunistic cybercriminals have exploited these flaws for financial motives.

As organizations grapple with this emerging threat, vigilance and prompt patch application remain crucial to safeguarding sensitive information and maintaining operational integrity.

Security Week News Tags:CERT Polska, CISA, CVE-2026-73570, cyber threats, Cybersecurity, email server, enterprise security, exploit campaign, Hacking, Malware, SNMP, state-sponsored attacks, Vulnerability, Zimbra

Post navigation

Previous Post: Citrix Patches Critical NetScaler Authentication Flaw
Next Post: ToxicPanda Malware Threatens Android Users with PIN Theft

Related Posts

Node.js Maintainers Targeted by North Korean Hackers Node.js Maintainers Targeted by North Korean Hackers Security Week News
Navia Data Breach Affects Millions Navia Data Breach Affects Millions Security Week News
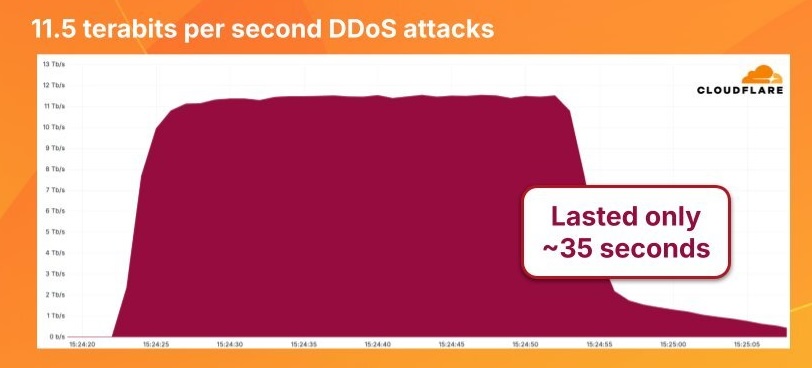
Cloudflare Blocks Record-Breaking 11.5 Tbps DDoS Attack Cloudflare Blocks Record-Breaking 11.5 Tbps DDoS Attack Security Week News
Vibe Coding: When Everyone’s a Developer, Who Secures the Code? Vibe Coding: When Everyone’s a Developer, Who Secures the Code? Security Week News
Russian Hacker Pleads Guilty Over Phobos Ransomware Russian Hacker Pleads Guilty Over Phobos Ransomware Security Week News
Managing the Trust-Risk Equation in AI: Predicting Hallucinations Before They Strike Managing the Trust-Risk Equation in AI: Predicting Hallucinations Before They Strike Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Trump Appoints Clayton to Lead Federal AI Task Force
  • South Korea Initiates Security Overhaul After Bank Data Breaches
  • China-Linked TA419 Targets U.S. AI Experts with Phishing
  • Key Arrest in ShinyHunters Case Aids FBI Investigation
  • Vercel Unveils KVM Zero-Day Flaw, Rewards Researcher $50K

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Trump Appoints Clayton to Lead Federal AI Task Force
  • South Korea Initiates Security Overhaul After Bank Data Breaches
  • China-Linked TA419 Targets U.S. AI Experts with Phishing
  • Key Arrest in ShinyHunters Case Aids FBI Investigation
  • Vercel Unveils KVM Zero-Day Flaw, Rewards Researcher $50K

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark