Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
CISA Alerts on SharePoint Flaw Amidst Active Exploitation

CISA Alerts on SharePoint Flaw Amidst Active Exploitation

Posted on July 2, 2026 By CWS

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has recently emphasized a significant security flaw affecting Microsoft SharePoint Server by adding it to its Known Exploited Vulnerabilities (KEV) catalog. This comes after evidence surfaced pointing to its active exploitation.

Details of the SharePoint Vulnerability

Identified as CVE-2026-45659, this vulnerability scores a 8.8 on the CVSS scale, highlighting its severity. The flaw is linked to remote code execution caused by the deserialization of untrusted data. Microsoft had previously patched this issue in May 2026, specifically for the SharePoint Server Subscription Edition, SharePoint Server 2019, and SharePoint Enterprise Server 2016.

According to Microsoft’s advisories, the vulnerability can be triggered by any authenticated attacker without needing elevated privileges. A network-based attack can be initiated by an attacker with basic Site Member permissions to execute code remotely on the server.

Current Exploitation and Recommendations

CISA has noted Microsoft’s assessment that the likelihood of exploitation is low. However, details on the exploitation methods, responsible parties, or the objectives behind these activities remain undisclosed. Federal Civilian Executive Branch (FCEB) agencies have been instructed to implement the necessary fixes by July 4, 2026, to mitigate this risk.

Parallel Threat Activities Detected by Microsoft

In a related investigation, Microsoft discovered two separate threat actors operating within the same network. This finding arose during a routine ransomware probe, revealing that these actors used sophisticated methods to maintain access and complicate response efforts.

One group, identified as Storm-2603, is known for using the Warlock ransomware. They have been exploiting known vulnerabilities in on-premises SharePoint servers since mid-2025. Their initial access attempts involved probing for local file inclusion vulnerabilities, potentially through CVE-2025-11371. Post-access, the attackers deployed tools to blend malicious activities with legitimate ones and created multiple remote access channels.

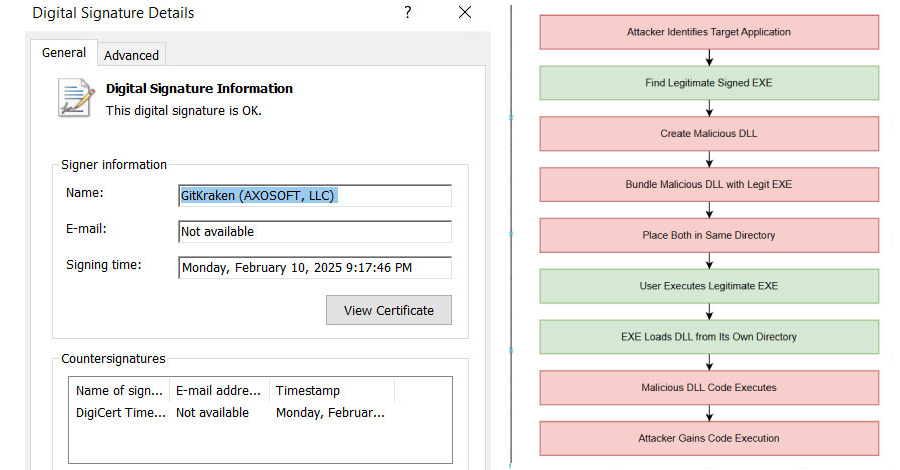
Simultaneously, another unrelated actor was detected using different techniques such as DLL side-loading. This overlap made attribution challenging and highlighted the complexity of cyber threats.

Conclusion and Future Outlook

The overlapping threat activities have shown how a single incident can evolve into a multi-faceted threat involving various actors and tactics. This underscores the importance for cybersecurity teams to look beyond isolated signals and consider the broader context of security incidents.

The Hacker News Tags:CISA, CVE-2026-45659, Cybersecurity, Microsoft, network security, Ransomware, remote code execution, SharePoint, threat intelligence, Vulnerability

Post navigation

Previous Post: WhatsApp Introduces Username Reservations Ahead of Launch
Next Post: Microsoft Vulnerabilities 2026: Key Insights Revealed

Related Posts

Device Code Phishing: A Rapidly Escalating Threat in 2026 Device Code Phishing: A Rapidly Escalating Threat in 2026 The Hacker News
30,000 Facebook Accounts Hacked in Phishing Scam 30,000 Facebook Accounts Hacked in Phishing Scam The Hacker News
Hackers Exploit c-ares DLL Side-Loading to Bypass Security and Deploy Malware Hackers Exploit c-ares DLL Side-Loading to Bypass Security and Deploy Malware The Hacker News
Europol and Eurojust Dismantle €600 Million Crypto Fraud Network in Global Sweep Europol and Eurojust Dismantle €600 Million Crypto Fraud Network in Global Sweep The Hacker News
Chrome Targeted by Active In-the-Wild Exploit Tied to Undisclosed High-Severity Flaw Chrome Targeted by Active In-the-Wild Exploit Tied to Undisclosed High-Severity Flaw The Hacker News
Microsoft Addresses 206 Security Vulnerabilities, Including Zero-Days Microsoft Addresses 206 Security Vulnerabilities, Including Zero-Days The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Retadup Worm Resurfaces with CoffeeLoader Malware
  • U.S. Imposes New Limits on China’s AI Chip Access
  • AI-Driven Marketplace Threatens Corporate Security
  • Top Patch Management Solutions for 2026
  • VS Code Extension Security Flaw Exposes Files Outside Workspaces

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Retadup Worm Resurfaces with CoffeeLoader Malware
  • U.S. Imposes New Limits on China’s AI Chip Access
  • AI-Driven Marketplace Threatens Corporate Security
  • Top Patch Management Solutions for 2026
  • VS Code Extension Security Flaw Exposes Files Outside Workspaces

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark