Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Drupal Core SQL Vulnerability Exploitation Reported

Drupal Core SQL Vulnerability Exploitation Reported

Posted on May 23, 2026 By CWS

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has recently highlighted a critical security issue in Drupal Core, emphasizing its addition to the Known Exploited Vulnerabilities (KEV) catalog. This development follows evidence of the flaw being actively exploited in the wild.

The identified vulnerability, labeled CVE-2026-9082 and rated with a CVSS score of 6.5, involves an SQL injection flaw affecting all currently supported versions of Drupal Core. According to CISA, this flaw could potentially lead to privilege escalation and remote code execution through specifically crafted database requests.

Immediate Patch Release and Exploit Detection

Just days after Drupal released security patches to address this issue, reports of active exploitation have surfaced. The precise methods and objectives of these attacks remain unclear at this moment. Nonetheless, patches have been made available for several Drupal versions, including 11.3.10, 11.2.12, and others. Notably, manual patching is required for versions 9.5 and 8.9.

On May 22, 2026, Drupal updated its security advisory to acknowledge the detection of exploit attempts. Security firm Imperva, owned by Thales, has reported over 15,000 attack attempts targeting nearly 6,000 unique websites across 65 countries.

Targeted Sectors and Attack Patterns

According to Imperva, the primary targets of these attacks include the gaming and financial services sectors, making up approximately 50% of the observed activity. The current attack pattern suggests that malicious actors are mainly engaged in reconnaissance, probing sites for vulnerabilities, particularly those using PostgreSQL-backed configurations of Drupal.

This reconnaissance activity indicates that attackers are seeking out exposed Drupal sites to identify potential entry points. While much of the activity is exploratory, the inherent risk of the vulnerability suggests that successful exploitation could swiftly escalate to data extraction or privilege escalation.

Recommendations for Federal Agencies

Federal Civilian Executive Branch (FCEB) agencies have been advised to implement the available patches by May 27, 2026, to ensure comprehensive protection against potential threats. This proactive measure is crucial in safeguarding against any further exploitation attempts that might capitalize on the uncovered flaw.

As the cybersecurity landscape continues to evolve, swift action and adherence to security advisories remain essential in mitigating risks associated with vulnerabilities in widely-used platforms like Drupal.
The Hacker News Tags:CISA, CVE-2026-9082, Cyberattack, Cybersecurity, database security, Drupal, Drupal core, Exploitation, Imperva, Patch, security flaw, SQL injection, Vulnerability, web security, website security

Post navigation

Previous Post: LiteSpeed Plugin Flaw Exploited for Root Access
Next Post: F5 BIG-IP Exploit Enables Network Intrusion via SSH

Related Posts

JPCERT Confirms Active Command Injection Attacks on Array AG Gateways JPCERT Confirms Active Command Injection Attacks on Array AG Gateways The Hacker News
VoidLink Linux Malware Framework Built with AI Assistance Reaches 88,000 Lines of Code VoidLink Linux Malware Framework Built with AI Assistance Reaches 88,000 Lines of Code The Hacker News
New FileFix Variant Delivers StealC Malware Through Multilingual Phishing Site New FileFix Variant Delivers StealC Malware Through Multilingual Phishing Site The Hacker News
New FileFix Method Emerges as a Threat Following 517% Rise in ClickFix Attacks New FileFix Method Emerges as a Threat Following 517% Rise in ClickFix Attacks The Hacker News
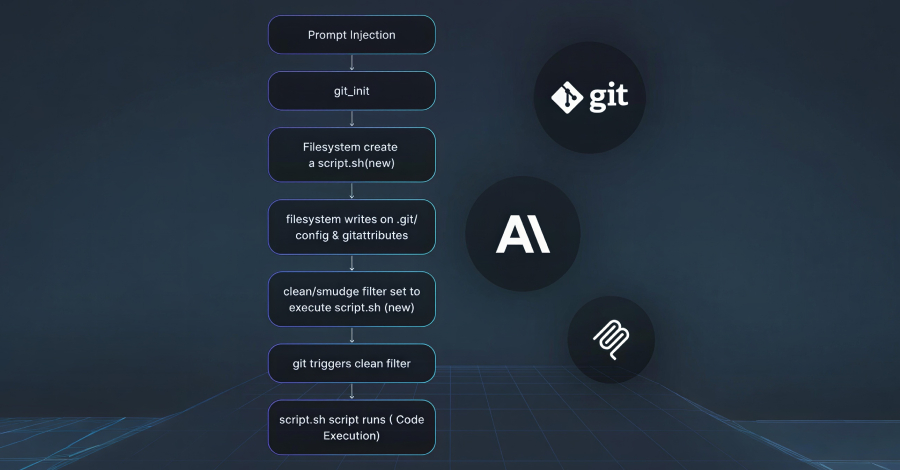
Three Flaws in Anthropic MCP Git Server Enable File Access and Code Execution Three Flaws in Anthropic MCP Git Server Enable File Access and Code Execution The Hacker News
Security Tools Alone Don’t Protect You — Control Effectiveness Does Security Tools Alone Don’t Protect You — Control Effectiveness Does The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Anthropic Expands Access to Claude for Cybersecurity Experts
  • Android October 2026 Security Update Fixes 25 Vulnerabilities
  • EY Cybersecurity Breach Impacts Goldman Sachs, Man Group
  • AppViewX Enhances AI Security with New Tools
  • Cyberattack Exposes Data of Over 1 Million in Arizona Courts

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Anthropic Expands Access to Claude for Cybersecurity Experts
  • Android October 2026 Security Update Fixes 25 Vulnerabilities
  • EY Cybersecurity Breach Impacts Goldman Sachs, Man Group
  • AppViewX Enhances AI Security with New Tools
  • Cyberattack Exposes Data of Over 1 Million in Arizona Courts

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark