Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
LastPass Warns of Fake Repositories Infecting macOS with Atomic Infostealer

LastPass Warns of Fake Repositories Infecting macOS with Atomic Infostealer

Posted on September 20, 2025September 20, 2025 By CWS

Sep 20, 2025Ravie LakshmananSoftware Safety / Malware
LastPass is warning of an ongoing, widespread info stealer marketing campaign concentrating on Apple macOS customers by means of faux GitHub repositories that distribute malware-laced packages masquerading as legit instruments.

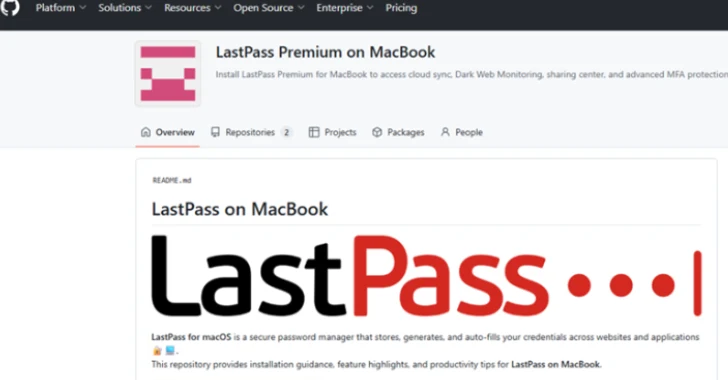
“Within the case of LastPass, the fraudulent repositories redirected potential victims to a repository that downloads the Atomic infostealer malware,” researchers Alex Cox, Mike Kosak, and Stephanie Schneider from the LastPass Risk Intelligence, Mitigation, and Escalation (TIME) staff stated.

Past LastPass, a few of the common instruments impersonated within the marketing campaign embody 1Password, Basecamp, Dropbox, Gemini, Hootsuite, Notion, Obsidian, Robinhood, Salesloft, SentinelOne, Shopify, Thunderbird, and TweetDeck, amongst others. All of the GiHub repositories are designed to focus on macOS techniques.

The assaults contain the usage of Search Engine Optimization (search engine marketing) poisoning to push hyperlinks to malicious GitHub websites on high of search outcomes on Bing and Google, that then instruct customers to the obtain this system by clicking the “Set up LastPass on MacBook” button, redirecting them a GitHub web page area.

“The GitHub pages seem like created by a number of GitHub usernames to get round takedowns,” LastPass stated.

The GitHub web page is designed to take the consumer to a different area that gives ClickFix-style directions to repeat and execute a command on the Terminal app, ensuing within the deployment of the Atomic Stealer malware.

It is price noting comparable campaigns have been beforehand leveraged malicious sponsored Google Adverts for Homebrew to distribute a multi-stage dropper by means of a bogus GitHub repository that may run detect digital machines or evaluation environments, and decode and execute system instructions to ascertain reference to a distant server, per safety researcher Dhiraj Mishra.

In latest weeks, risk actors have been noticed leveraging public GitHub repositories to host malicious payloads and distribute them through Amadey, in addition to make use of dangling commits similar to an official GitHub repository to redirect unwitting customers to malicious packages.

The Hacker News Tags:Atomic, Fake, Infecting, InfoStealer, LastPass, macOS, Repositories, Warns

Post navigation

Previous Post: Researchers Uncover GPT-4-Powered MalTerminal Malware Creating Ransomware, Reverse Shell
Next Post: Top Zero-Day Vulnerabilities Exploited in the Wild in 2025

Related Posts

Critical Flaw in LMS Exploited for Cyber Attacks Critical Flaw in LMS Exploited for Cyber Attacks The Hacker News
New Brazilian Malware Targets Financial Platforms New Brazilian Malware Targets Financial Platforms The Hacker News
RabbitMQ Vulnerabilities Expose OAuth Secrets, Threaten Security RabbitMQ Vulnerabilities Expose OAuth Secrets, Threaten Security The Hacker News
Chinese Hackers Target Chrome-Windows with Zero-Day Exploits Chinese Hackers Target Chrome-Windows with Zero-Day Exploits The Hacker News
Kali365 Exploits Microsoft Login to Threaten US Firms Kali365 Exploits Microsoft Login to Threaten US Firms The Hacker News
Assessing the Role of AI in Zero Trust Assessing the Role of AI in Zero Trust The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark