Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Microsoft Resolves Critical Azure AI Foundry Security Issue

Microsoft Resolves Critical Azure AI Foundry Security Issue

Posted on September 18, 2026 By CWS

Microsoft has announced the resolution of a critical security issue within its Azure AI Foundry platform, characterized as a high-severity vulnerability. The flaw, identified as CVE-2026-85889 and assigned a CVSS score of 10.0, allows unauthorized attackers to escalate privileges via network access. Microsoft has confirmed that no immediate action is required from users, as the issue has been fully addressed.

Details of the Azure AI Foundry Vulnerability

The Azure AI Foundry, also known as Microsoft Foundry, serves as an enterprise-level platform for the creation, deployment, and management of generative AI applications. A security advisory from Microsoft highlighted the absence of necessary authentication for a critical function within the platform, enabling potential privilege escalation by unauthorized entities.

Security researcher Rémy Marot, credited with discovering the flaw, reported the vulnerability, which has not been exploited in any known attacks. Microsoft’s swift response to this issue underscores its commitment to maintaining robust cloud security measures.

Additional Microsoft Vulnerability Patches

In addition to the Azure AI Foundry flaw, Microsoft has patched several other critical vulnerabilities across its software suite. These include CVE-2026-85885 and CVE-2026-85878, both with a CVSS score of 9.9, affecting Microsoft 365 Copilot and Azure Database for PostgreSQL, respectively. Another significant vulnerability, CVE-2026-87701, was identified in Azure Cosmos DB with a CVSS score of 9.6.

These vulnerabilities, typical of cloud-based security issues, have been mitigated without requiring user intervention. The consistent updates reflect Microsoft’s proactive approach to software security.

Recent Updates to Windows Vulnerabilities

Microsoft has also addressed two additional vulnerabilities impacting Windows systems. CVE-2026-62721 and CVE-2026-85921, affecting Windows User-Mode Power Service and Windows Secure Kernel Mode respectively, have been resolved. These issues, which allowed privilege escalation, were rectified through an out-of-band update for Windows 11, version 26H1.

The updates come shortly after Microsoft patched 974 vulnerabilities, two of which were actively exploited. The Advanced Local Procedure Call (ALPC) vulnerability was notably used in conjunction with Chrome flaws to create the BlueMoon exploit kit.

As Microsoft continues to enhance its security protocols, these updates reinforce the importance of timely software patching to protect against potential cyber threats.
The Hacker News Tags:AI security, Azure AI, cloud security, CVE-2026-85889, Cybersecurity, enterprise AI, IT security, Microsoft, Microsoft Foundry, Patch Tuesday, privilege escalation, security update, software update, technology news, vulnerability fix

Post navigation

Previous Post: AI Malware Evolves Hourly to Evade Detection
Next Post: Ransomware Developer Sentenced Amid Cybersecurity Alerts

Related Posts

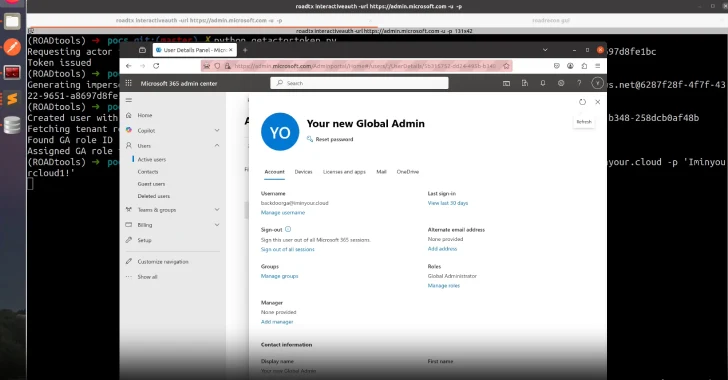
Microsoft Patches Critical Entra ID Flaw Enabling Global Admin Impersonation Across Tenants Microsoft Patches Critical Entra ID Flaw Enabling Global Admin Impersonation Across Tenants The Hacker News
DeepSeek Harness Flaw Allows AI Sandbox Bypass DeepSeek Harness Flaw Allows AI Sandbox Bypass The Hacker News
Tsundere Botnet Expands Using Game Lures and Ethereum-Based C2 on Windows Tsundere Botnet Expands Using Game Lures and Ethereum-Based C2 on Windows The Hacker News
Researchers Uncover NodeCordRAT Hidden in npm Bitcoin-Themed Packages Researchers Uncover NodeCordRAT Hidden in npm Bitcoin-Themed Packages The Hacker News
Cyber Espionage Campaign Targets Czech Republic and Taiwan Cyber Espionage Campaign Targets Czech Republic and Taiwan The Hacker News
7 Key Workflows for Maximum Impact 7 Key Workflows for Maximum Impact The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Top Container Registry Security Tools in 2026
  • Ransomware Developer Sentenced Amid Cybersecurity Alerts
  • Microsoft Resolves Critical Azure AI Foundry Security Issue
  • AI Malware Evolves Hourly to Evade Detection
  • Microsoft Updates Address AI and Cloud Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Top Container Registry Security Tools in 2026
  • Ransomware Developer Sentenced Amid Cybersecurity Alerts
  • Microsoft Resolves Critical Azure AI Foundry Security Issue
  • AI Malware Evolves Hourly to Evade Detection
  • Microsoft Updates Address AI and Cloud Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark