Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
SysAid Patches 4 Critical Flaws Enabling Pre-Auth RCE in On-Premise Version

SysAid Patches 4 Critical Flaws Enabling Pre-Auth RCE in On-Premise Version

Posted on May 7, 2025May 9, 2025 By CWS No Comments on SysAid Patches 4 Critical Flaws Enabling Pre-Auth RCE in On-Premise Version

Could 07, 2025Ravie LakshmananVulnerability / IT Service
Cybersecurity researchers have disclosed a number of safety flaw within the on-premise model of SysAid IT assist software program that may very well be exploited to attain pre-authenticated distant code execution with elevated privileges.
The vulnerabilities, tracked as CVE-2025-2775, CVE-2025-2776, and CVE-2025-2777, have all been described as XML Exterior Entity (XXE) injections, which happen when an attacker is ready to efficiently intrude with an software’s parsing of XML enter.
This, in flip, may allow attackers to inject unsafe XML entities into the online software, permitting them to hold out a Server-Aspect Request Forgery (SSRF) assault and in worst instances, distant code execution.

An outline of the three vulnerabilities, in accordance with watchTowr Labs researchers Sina Kheirkhah and Jake Knott, is as follows –

CVE-2025-2775 and CVE-2025-2776 – A pre-authenticated XXE inside the /mdm/checkin endpoint
CVE-2025-2777 – A pre-authenticated XXE inside the /lshw endpoint

watchTowr Labs described the vulnerabilities as trivial to use via a specifically crafted HTTP POST request to the endpoints in query.

Profitable exploitation of the issues may allow an attacker to retrieve native recordsdata containing delicate info, together with SysAid’s personal “InitAccount.cmd” file, which incorporates details about the administrator account username and plaintext password created throughout set up.
Armed with this info, the attacker may then acquire full administrative entry to SysAid as an administrator-privileged consumer.
To make issues worse, the XXE flaws may very well be chained with one other working system command injection vulnerability – found by a third-party – to attain distant code execution. The command injection problem has been assigned the CVE identifier CVE-2025-2778.

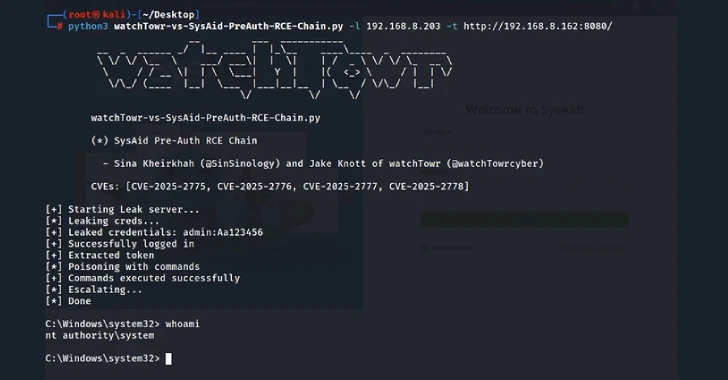
All 4 vulnerabilities have been rectified by SysAid with the discharge of on-premise model 24.4.60 b16 in early March 2025. A proof-of-concept (PoC) exploit combining the 4 vulnerabilities has been made accessible.
With safety flaws in SysAid (CVE-2023-47246) beforehand exploited by ransomware actors like Cl0p in zero-day assaults, it is crucial that customers replace their cases to the newest model.

Discovered this text fascinating? Comply with us on Twitter  and LinkedIn to learn extra unique content material we put up.
The Hacker News Tags:Critical, Enabling, Flaws, OnPremise, Patches, PreAuth, RCE, SysAid, Version

Post navigation

Previous Post: Spyware Maker NSO Ordered to Pay $167 Million Over WhatsApp Hack
Next Post: US Sanctions Myanmar Militia Involved in Cyber Scams 

Related Posts

FCC Bans Foreign-Made Drones and Key Parts Over U.S. National Security Risks FCC Bans Foreign-Made Drones and Key Parts Over U.S. National Security Risks The Hacker News
Cline CLI Supply Chain Breach Installs OpenClaw Cline CLI Supply Chain Breach Installs OpenClaw The Hacker News
Why DNS Security Is Your First Defense Against Cyber Attacks? Why DNS Security Is Your First Defense Against Cyber Attacks? The Hacker News
CRESCENTHARVEST Campaign Targets Iranian Protest Allies CRESCENTHARVEST Campaign Targets Iranian Protest Allies The Hacker News
HPE Issues Security Patch for StoreOnce Bug Allowing Remote Authentication Bypass HPE Issues Security Patch for StoreOnce Bug Allowing Remote Authentication Bypass The Hacker News
Google Gemini AI Inadvertently Breaches Real Company Systems Google Gemini AI Inadvertently Breaches Real Company Systems The Hacker News

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Ivanti Releases Critical Security Updates for Key Products
  • Microsoft’s November Patch Tuesday Fixes 1,094 Vulnerabilities
  • Git Addresses Critical Vulnerability in Recursive Clone Operations
  • Notion AI Chat Transcripts Exposed in Security Breach
  • Adobe Addresses Critical Vulnerabilities in Patch Update

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Ivanti Releases Critical Security Updates for Key Products
  • Microsoft’s November Patch Tuesday Fixes 1,094 Vulnerabilities
  • Git Addresses Critical Vulnerability in Recursive Clone Operations
  • Notion AI Chat Transcripts Exposed in Security Breach
  • Adobe Addresses Critical Vulnerabilities in Patch Update

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark