Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hackers Compromise Active Directory to Steal NTDS.dit that Leads to Full Domain Compromise

Hackers Compromise Active Directory to Steal NTDS.dit that Leads to Full Domain Compromise

Posted on September 26, 2025September 26, 2025 By CWS

Energetic Listing (AD) stays the muse of authentication and authorization in Home windows environments. Menace actors concentrating on the NTDS.dit database can harvest each area credential, unlock lateral motion, and obtain full area compromise. 

Attackers leveraged native Home windows utilities to dump and exfiltrate NTDS.dit, bypassing customary defenses. 

The adversary on this case obtained DOMAIN ADMIN privileges by way of a profitable phishing marketing campaign and subsequent privilege escalation. As soon as elevated, they executed:

To create a Quantity Shadow Copy and extract NTDS.dit, silently bypassing file locks. With the SYSTEM hive obtained, attackers decrypted the database offline utilizing secretsdump.py from Impacket:

This chain enabled harvesting of NTLM and AES hashes for all area accounts with out triggering conventional endpoint alarms.

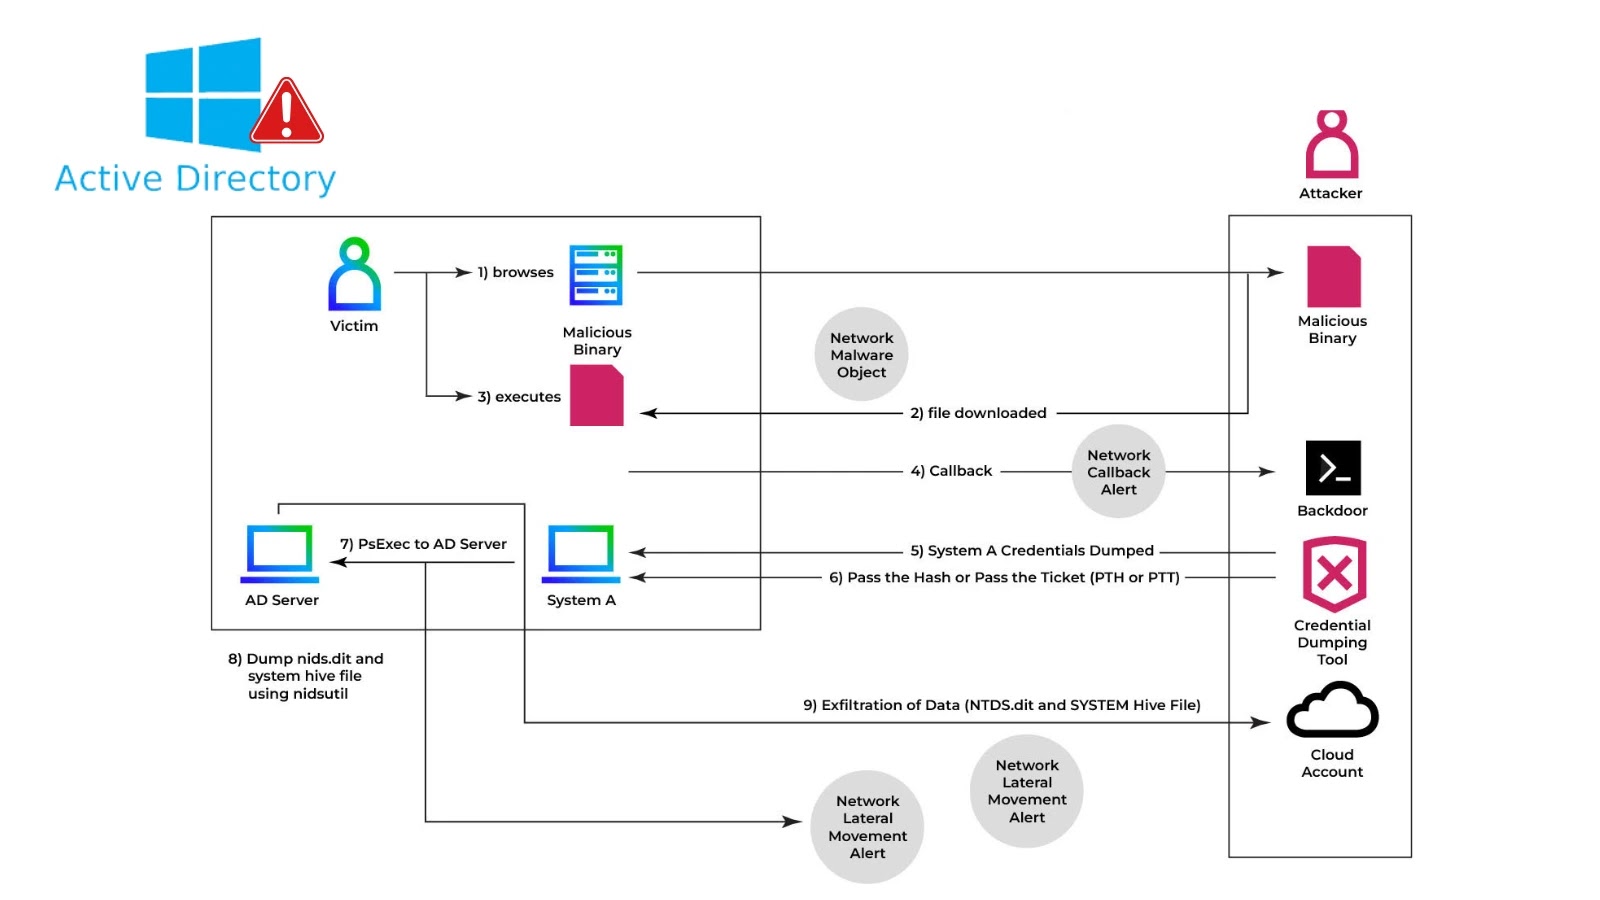
Full Kill Chain

After archiving and compressing the dump with tar -czf ntds.tar.gz c:tempntds.dit c:tempSYSTEM, the attackers exfiltrated information over SMB to a compromised file share.

NTDS.dit file dump

Trellix detected this exercise by way of two high-fidelity signatures: anomalous SMB write patterns exceeding baseline quantity and a customized exfiltration signature for big NTDS file transfers. 

Behavioral detection flagged sudden esentutl processes working outdoors upkeep home windows, and protocol anomaly alerts triggered on shadow copy reads to C:$VolumeShadowCopy.

Via Trellix Sensible, AI-driven alert correlation highlighted the development from VSS creation to SMB add, lowering analyst workload by 60% and reducing imply time to detect (MTTD) by 45%. 

The theft of NTDS.dit poses an existential risk to Home windows domains, offering attackers full management over all credentials.  

 NTDS.dit archived for exfiltration

Conventional defenses usually miss the low-and-slow strategies employed throughout shadow copy creation and offline decryption.

Comply with us on Google Information, LinkedIn, and X for every day cybersecurity updates. Contact us to characteristic your tales.
Cyber Security News Tags:Active, Compromise, Directory, Domain, Full, Hackers, Leads, NTDS.dit, Steal

Post navigation

Previous Post: Fortra GoAnywhere CVSS 10 Flaw Exploited as 0-Day a Week Before Public Disclosure
Next Post: New XCSSET macOS Malware Variant Hijacks Cryptocurrency Transactions

Related Posts

Citrix Windows Virtual Delivery Agent Vulnerability Let Attackers Gain SYSTEM Privileges Citrix Windows Virtual Delivery Agent Vulnerability Let Attackers Gain SYSTEM Privileges Cyber Security News
Windows 11 24H2 Update Hides the Password Icon in the Sign-in Options on the Lock Screen Windows 11 24H2 Update Hides the Password Icon in the Sign-in Options on the Lock Screen Cyber Security News
Malicious Chrome Extensions as VPN Intercept User Traffic to Steal Credentials Malicious Chrome Extensions as VPN Intercept User Traffic to Steal Credentials Cyber Security News
PowerShell Exploited in New TASK#STOMP Cyber Intrusion PowerShell Exploited in New TASK#STOMP Cyber Intrusion Cyber Security News
Android Remote Data-Wipe Malware Attacking Users Leveraging Google’s Find Hub Android Remote Data-Wipe Malware Attacking Users Leveraging Google’s Find Hub Cyber Security News
Lyrie.ai Enhances AI Security with New Protocol Lyrie.ai Enhances AI Security with New Protocol Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles
  • Critical Vulnerability in Oracle PeopleSoft Exploited Globally
  • Kiteworks Recommends Nine-Hour System Shutdown Amid Cyber Threat
  • New Botnet x47.c Leverages AI for Advanced Cyber Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles
  • Critical Vulnerability in Oracle PeopleSoft Exploited Globally
  • Kiteworks Recommends Nine-Hour System Shutdown Amid Cyber Threat
  • New Botnet x47.c Leverages AI for Advanced Cyber Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark