A classy cyber marketing campaign is exploiting the belief customers place in in style collaboration software program, tricking them into downloading a weaponized model of Microsoft Groups to realize distant entry to their techniques.
Risk actors are utilizing search engine marketing (search engine optimization) poisoning and malicious commercials to lure unsuspecting victims to fraudulent obtain pages, a tactic that intently mirrors earlier campaigns involving different trusted software program.
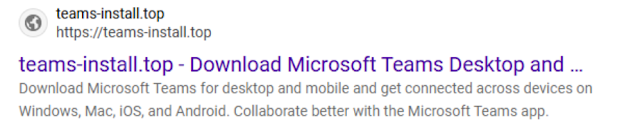
Blackpoint has recognized a brand new wave of assaults the place customers looking for “Microsoft Groups obtain” are offered with malicious adverts that redirect them to spoofed web sites.
One such area, teams-install[.]high, has been noticed impersonating the official Microsoft obtain portal, providing a malicious file named MSTeamsSetup.exe.
To look respectable, these pretend installers are sometimes signed with untrustworthy digital certificates from issuers like “4th State Oy” and “NRM NETWORK RISK MANAGEMENT INC.”. This system helps bypass fundamental safety checks that flag unsigned software program.
Malicious area
Weaponized Microsoft Groups Delivers Oyster Backdoor
Executing the fraudulent installer triggers a multi-stage assault that deploys a persistent backdoor generally known as Oyster, or Broomstick.
The malware drops a malicious DLL file named CaptureService.dll into the %APPDATA%Roaming folder and establishes persistence by making a scheduled activity referred to as CaptureService.
This activity is configured to run the DLL periodically, guaranteeing the backdoor stays energetic even after a system reboot and permitting it to mix in with regular Home windows exercise.
The Oyster backdoor supplies attackers with a robust foothold within the compromised community.
It permits for distant entry, collects system data, and establishes communication with command-and-control (C2) servers to exfiltrate information and obtain additional directions or payloads.
On this marketing campaign, Oyster has been noticed speaking with C2 domains akin to nickbush24[.]com and techwisenetwork[.]com, Blackpoint evaluation revealed.
Assault Chain
This marketing campaign shouldn’t be an remoted incident however a part of a broader development the place cybercriminals weaponize well-known software program manufacturers to attain preliminary entry. The ways are just like earlier campaigns that distributed pretend installers for PuTTY, WinSCP, and Google Chrome.
By leveraging malvertising and search engine optimization poisoning, attackers can successfully goal a large viewers, exploiting person belief in each serps and in style enterprise instruments.
The usage of the Oyster backdoor is especially regarding, because it has been linked to ransomware operations like Rhysida, which have used it to infiltrate company networks.
This technique highlights a shift the place menace actors aren’t simply counting on phishing emails however are actively poisoning the software program provide chain on the user-download degree.
The marketing campaign is designed to bypass some conventional antivirus and endpoint detection and response (EDR) options, making it a stealthy and harmful menace.
To mitigate this danger, organizations and people are strongly suggested to obtain software program solely from official vendor web sites.
Utilizing saved bookmarks for incessantly accessed obtain pages is really helpful over counting on search engine outcomes, particularly sponsored commercials. Vigilance and person schooling stay crucial strains of protection towards these evolving social engineering ways.
Comply with us on Google Information, LinkedIn, and X for each day cybersecurity updates. Contact us to characteristic your tales.