Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Organizations Warned of Exploited Meteobridge Vulnerability

Organizations Warned of Exploited Meteobridge Vulnerability

Posted on October 3, 2025October 3, 2025 By CWS

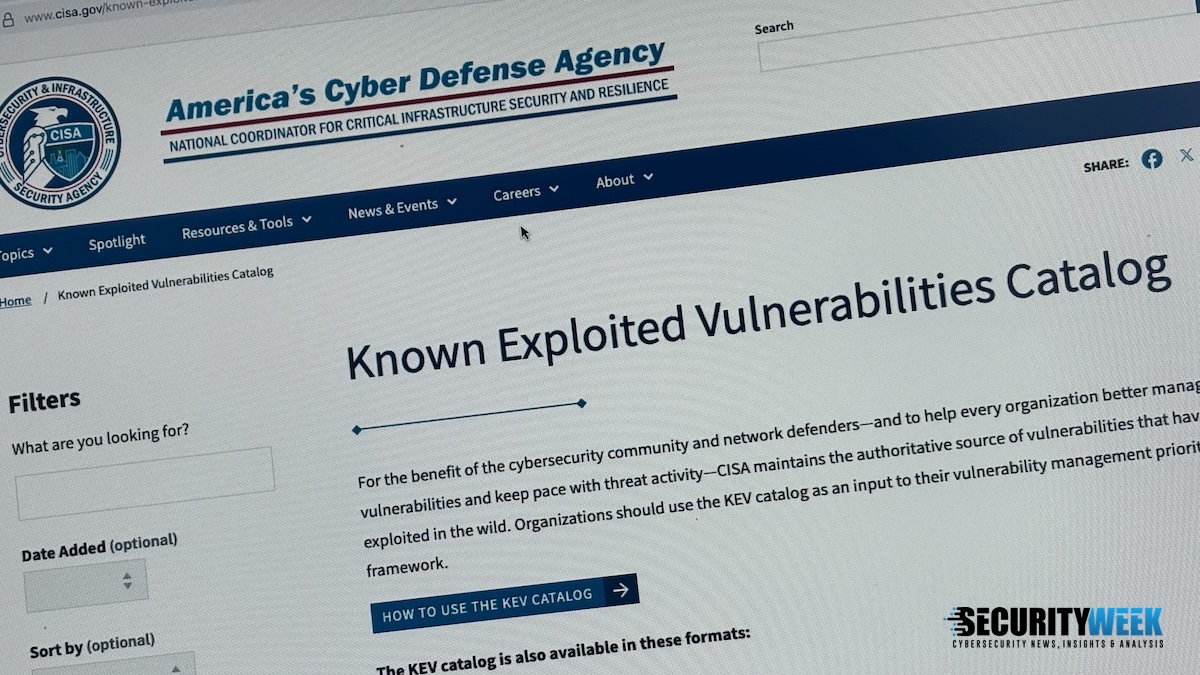
The US cybersecurity company CISA on Thursday warned {that a} Meteobridge vulnerability patched in Might has been exploited in assaults and added the flaw to its Recognized Exploited Vulnerabilities (KEV) catalog.

Meteobridge is a tool that permits directors to attach their climate stations to public climate networks. Station information assortment and system administration performance is offered by way of the Meteobridge internet interface.

Whereas Meteobridge shouldn’t be uncovered to the web, there are roughly 100 units which might be accessible from the general public internet, Shodan historic information reveals. This misconfiguration exposes susceptible units to potential assaults.

Tracked as CVE-2025-4008 (CVSS rating of 8.7), the Meteobridge bug now flagged as exploited was recognized in an internet interface endpoint (a CGI shell script) that’s liable to command injection.

The difficulty exists as a result of user-controlled enter is parsed and utilized in an eval name with out sanitization. Moreover, as a result of the susceptible CGI script is out there within the public folder, it’s not protected by authentication, permitting unauthenticated attackers to take advantage of the bug by way of a curl command.

“Distant exploitation by way of malicious webpage can be doable because it’s a GET request with none type of customized header or token parameter,” Onekey explains.

On Might 13, Smartbedded introduced that MeteoBridge model 6.2 was launched with fixes for “an utility safety threat”, with out mentioning the CVE or the vulnerability’s exploitation.

Now, CISA warns that risk actors have exploited the flaw in assaults, urging federal companies to deal with it inside the subsequent three weeks, as mandated by the Binding Operational Directive (BOD) 22-01.Commercial. Scroll to proceed studying.

Whereas Onekey revealed technical particulars on CVE-2025-4008 and a proof-of-concept (PoC) exploit in Might, there have been no experiences of the bug’s in-the-wild exploitation previous to CISA including it to KEV.

On Thursday, CISA additionally expanded the KEV record with a latest Samsung zero-day (CVE-2025-21043) and with three outdated safety defects in Jenkins (CVE-2017-1000353), Juniper ScreenOS (CVE-2015-7755), and GNU Bash OS (CVE-2014-6278, aka Shellshock), which have been flagged as exploited earlier than.

All organizations are suggested to deal with these 5 vulnerabilities, and all the issues described by CISA’s KEV record.

Associated: Oracle Says Recognized Vulnerabilities Probably Exploited in Latest Extortion Assaults

Associated: Organizations Warned of Exploited Sudo Vulnerability

Associated: WireTap Assault Breaks Intel SGX Safety

Associated: Chrome 141 and Firefox 143 Patches Repair Excessive-Severity Vulnerabilities
Security Week News Tags:Exploited, Meteobridge, Organizations, Vulnerability, Warned

Post navigation

Previous Post: MokN Raises $3 Million for Phish-Back Solution
Next Post: How Passwork 7 Addresses Complexity of Enterprise Security

Related Posts

Salesforce AI Hack Enabled CRM Data Theft Salesforce AI Hack Enabled CRM Data Theft Security Week News
Data Breach by Over 300 Chrome Extensions Uncovered Data Breach by Over 300 Chrome Extensions Uncovered Security Week News
New Wave of Attacks Targeting FortiGate Firewalls New Wave of Attacks Targeting FortiGate Firewalls Security Week News
Verisoul Raises .8 Million for Fraud Prevention Verisoul Raises $8.8 Million for Fraud Prevention Security Week News
DHS Database Breach and Adobe’s Security Enhancements DHS Database Breach and Adobe’s Security Enhancements Security Week News
Manpower Says Data Breach Stemming From Ransomware Attack Impacts 140,000 Manpower Says Data Breach Stemming From Ransomware Attack Impacts 140,000 Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark