Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Google Chrome Can Now Auto-Change Compromised Passwords Using Its Built-In Manager

Google Chrome Can Now Auto-Change Compromised Passwords Using Its Built-In Manager

Posted on May 21, 2025May 21, 2025 By CWS

Might 21, 2025Ravie LakshmananData Breach / Account Safety
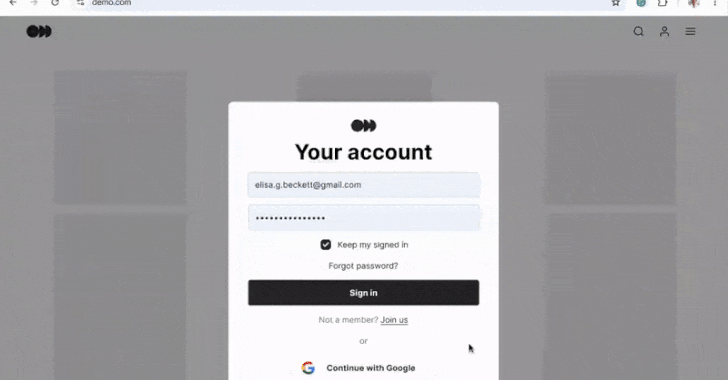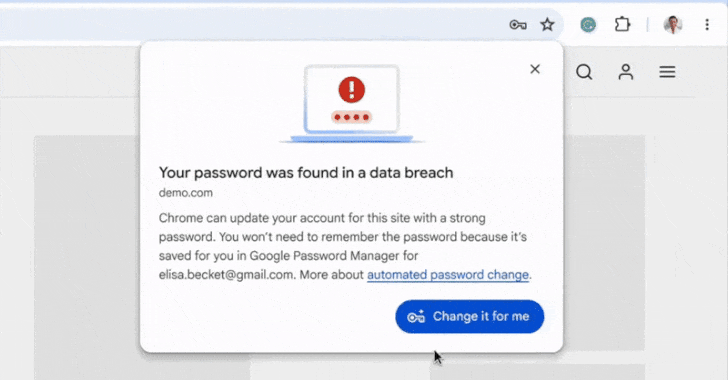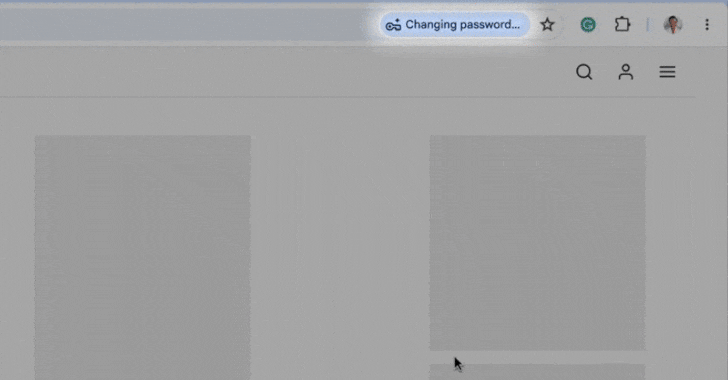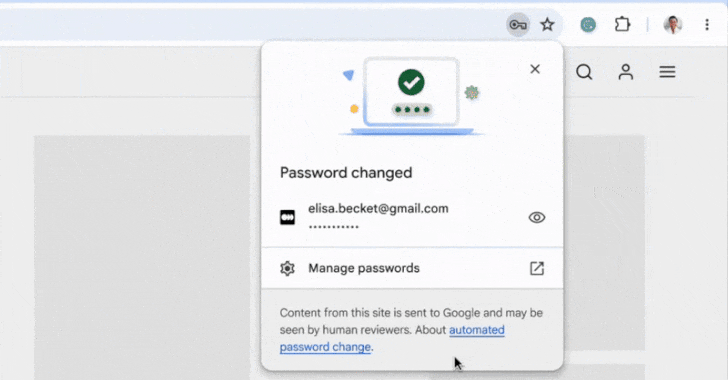
Google has introduced a brand new characteristic in its Chrome browser that lets its built-in Password Supervisor routinely change a consumer’s password when it detects the credentials to be compromised.
“When Chrome detects a compromised password throughout sign up, Google Password Supervisor prompts the consumer with an choice to repair it routinely,” Google’s Ashima Arora, Chirag Desai, and Eiji Kitamura mentioned. “On supported web sites, Chrome can generate a powerful alternative and replace the password for the consumer routinely.”
The characteristic builds upon Password Supervisor’s present capabilities to generate sturdy passwords throughout sign-up and flag credentials which were detected in a knowledge breach.
With the automated password change, Google mentioned the thought is to cut back friction and assist customers maintain their accounts safe with out having to seek for related account settings or abandon the method halfway.
Web site house owners can assist this characteristic by adopting the next strategies –

Use autocomplete=”current-password” and autocomplete=”new-password” to set off autofill and storage
Arrange a redirect from <your-website-domain>/.well-known/change-password to the password change type on their web site

“It might be a lot simpler if password managers might navigate the consumer on to the change-password URL,” Kitamura mentioned. “That is the place a well known URL for altering passwords turns into helpful.”

“By reserving a well known URL path that redirects the consumer to the change password web page, the web site can simply redirect customers to the suitable place to alter their passwords.”
The event comes as corporations are more and more shifting to passkeys as a stronger different to guard accounts from potential takeover assaults. Earlier this month, Microsoft mentioned it is making passkeys the default technique when signing up for brand spanking new buyer accounts.

Discovered this text attention-grabbing? Comply with us on Twitter  and LinkedIn to learn extra unique content material we put up.
The Hacker News Tags:AutoChange, BuiltIn, Chrome, Compromised, Google, Manager, Passwords

Post navigation

Previous Post: How to Secure Company Emails Against Phishing
Next Post: Critical OpenPGP.js Vulnerability Allows Spoofing

Related Posts

Open Source Web Application Firewall with Zero-Day Detection and Bot Protection Open Source Web Application Firewall with Zero-Day Detection and Bot Protection The Hacker News
UAC-0099 Uses GuardBreaker to Disrupt AI Systems UAC-0099 Uses GuardBreaker to Disrupt AI Systems The Hacker News
IBM Warns of Critical API Connect Bug Allowing Remote Authentication Bypass IBM Warns of Critical API Connect Bug Allowing Remote Authentication Bypass The Hacker News
Microsoft Alerts on IRS Phishing Amid Tax Season Microsoft Alerts on IRS Phishing Amid Tax Season The Hacker News
INTERPOL Dismantles Sniper Dz Phishing Platform INTERPOL Dismantles Sniper Dz Phishing Platform The Hacker News
Ransomware Groups Exploit Citrix Vulnerability Ransomware Groups Exploit Citrix Vulnerability The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Session Cookie Flaw Risks Entra ID MFA Security
  • Sony Enhances PS5 Security Amid Relapse Jailbreak Concerns
  • Critical Dell CSM Vulnerabilities Allow Admin Access
  • WordPress Backups Expose Valuable AWS and Email Credentials
  • Antino Backdoor Utilizes Microsoft 365 in Espionage

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Session Cookie Flaw Risks Entra ID MFA Security
  • Sony Enhances PS5 Security Amid Relapse Jailbreak Concerns
  • Critical Dell CSM Vulnerabilities Allow Admin Access
  • WordPress Backups Expose Valuable AWS and Email Credentials
  • Antino Backdoor Utilizes Microsoft 365 in Espionage

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark