Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
New Analysis Uncovers LockBit 5.0 Key Capabilities and Two-Stage Execution Model

New Analysis Uncovers LockBit 5.0 Key Capabilities and Two-Stage Execution Model

Posted on November 7, 2025November 7, 2025 By CWS

LockBit 5.0 made its debut in late September 2025, marking a big improve for one of the infamous ransomware-as-a-service (RaaS) teams.

With roots tracing again to the ABCD ransomware in 2019, LockBit quickly grew in sophistication, constantly updating its techniques regardless of going through aggressive regulation enforcement efforts and affiliate panel leaks.

The most recent model is constructed on the prevailing v4.0 codebase, but it introduces new strategies designed to maximise evasion and harmful impression throughout numerous organizational networks.

FlashPoint safety analysts recognized LockBit 5.0’s uniquely modular structure as a notable innovation within the ransomware’s ongoing evolution.

Their detailed technical evaluation highlights how this malware continues to threaten important infrastructure by leveraging superior execution and obfuscation methods.

Massive-scale assaults have been noticed concentrating on industries no matter their geographic and operational boundaries, making certain LockBit’s continued repute for stealth and resilience.

One standout development in LockBit 5.0 is its two-stage execution mannequin, which expertly divides the an infection course of into loader and payload phases.

The preliminary stage entails a stealthy loader constructed for persistence and anti-analysis, using management stream obfuscation to dynamically calculate execution paths and complicate reverse engineering.

The loader dynamically resolves API calls utilizing a hashing algorithm, then reloads recent copies of core libraries—resembling NTDLL and Kernel32—successfully bypassing hooks positioned by safety instruments.

Ransom notice decryption utilizing RC4 (Supply – FlashPoint)

After making a suspended occasion of defrag.exe, it injects the decrypted payload by course of hollowing, updating the instruction pointer with ZwWriteProcessMemory and resuming execution in reminiscence, all whereas evading normal detection mechanisms.

// Course of hollowing code snippet excerpt
HANDLE hProcess = CreateProcess(“defrag.exe”, …);
ZwWriteProcessMemory(hProcess, …); // Inject LockBit payload
ResumeThread(hProcess);

This technical breakdown demonstrates LockBit’s dedication to maximizing operational stealth and survivability.

Comply with us on Google Information, LinkedIn, and X to Get Extra On the spot Updates, Set CSN as a Most popular Supply in Google.
Cyber Security News Tags:Analysis, Capabilities, Execution, Key, LockBit, Model, TwoStage, Uncovers

Post navigation

Previous Post: New Android Malware ‘Fantasy Hub’ Intercepts SMS Messages, Contacts and Call Logs
Next Post: Radical Empowerment From Your Leadership: Understood by Few, Essential for All

Related Posts

Google Warns of Threat Actors Using Fake Job Posting to Deliver Malware and Steal Credentials Google Warns of Threat Actors Using Fake Job Posting to Deliver Malware and Steal Credentials Cyber Security News
Italian Adviser Becomes Latest Target in Expanding Paragon Graphite Spyware Surveillance Case Italian Adviser Becomes Latest Target in Expanding Paragon Graphite Spyware Surveillance Case Cyber Security News
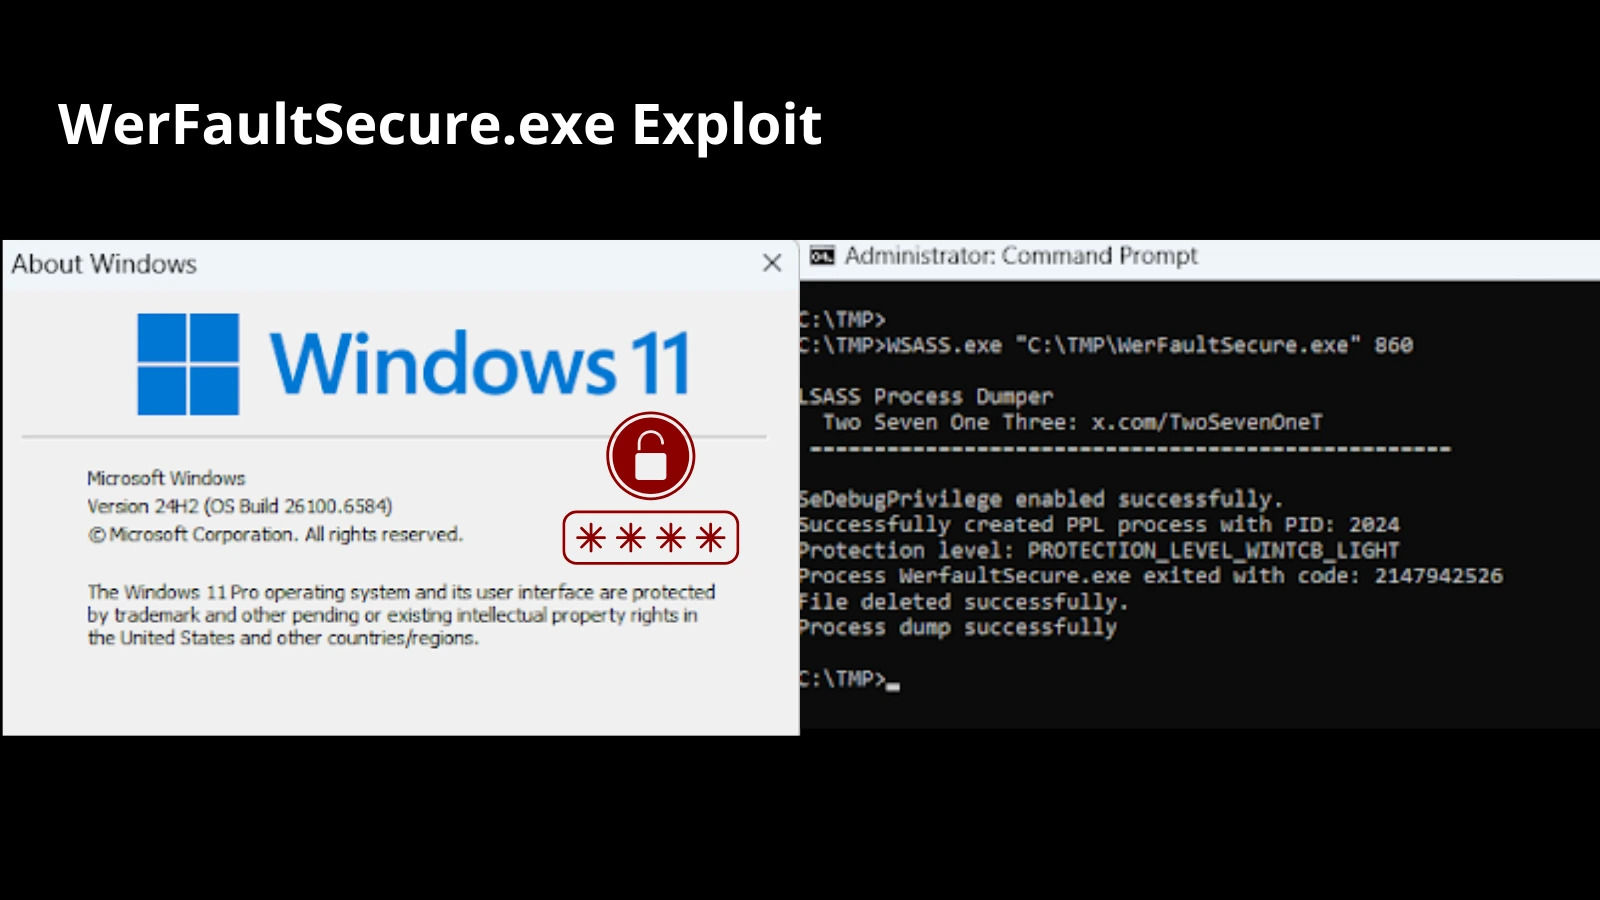
Attackers Can Exploit WerFaultSecure.exe Tool to Steal Cached Passwords From Windows 11 24H2 Attackers Can Exploit WerFaultSecure.exe Tool to Steal Cached Passwords From Windows 11 24H2 Cyber Security News
Top Dark Web Monitoring Tools for 2026 Top Dark Web Monitoring Tools for 2026 Cyber Security News
Hackers Weaponize PDF Along With a Malicious LNK File to Compromise Windows Systems Hackers Weaponize PDF Along With a Malicious LNK File to Compromise Windows Systems Cyber Security News
Chinese PlushDaemon Hackers use EdgeStepper Tool to Hijack Legitimate Updates and Redirect to Malicious Servers Chinese PlushDaemon Hackers use EdgeStepper Tool to Hijack Legitimate Updates and Redirect to Malicious Servers Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark