Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Spotting Phishing-to-RMM Threats Early

Spotting Phishing-to-RMM Threats Early

Posted on May 7, 2026 By CWS

Cybersecurity researchers at ANY.RUN have identified a sophisticated phishing-to-RMM attack campaign. Cybercriminals are mimicking legitimate sites like Microsoft and Adobe to distribute remote management tools such as ScreenConnect and LogMeIn Rescue under false pretenses.

This type of attack is particularly challenging to detect due to the authentic nature of the payloads and infrastructure used. Security analysts must piece together the entire sequence, from the initial phishing lure to the execution of RMM software, to thwart potential threats.

Geographical and Sector-Specific Impact

ANY.RUN’s findings indicate that these phishing-to-RMM activities are most prevalent in the United States, followed by regions such as Canada, Europe, and Australia. Industries heavily impacted include Education, Technology, Banking, Government, Manufacturing, and Finance. These sectors routinely use remote administration, making it harder to discern malicious RMM activity at first glance.

For security professionals, simply identifying the presence of tools like ScreenConnect or LogMeIn Rescue is insufficient. The context of the download, the source page, and the user’s expectations are crucial for accurate threat identification.

Mechanisms of Phishing-to-RMM Attacks

Within the ANY.RUN sandbox, researchers have traced various phishing-to-RMM pathways. These attacks often exploit well-known brands and legitimate remote access tools to infiltrate systems.

For instance, a phishing page posing as the Microsoft Store may prompt users to download a file named Adobesetup.exe. This file, however, is a ScreenConnect installer, granting attackers remote access once executed.

Detailed Attack Scenarios

In another scenario, a fake OneDrive download page deceives users into clicking a “Verify to Download” prompt, which results in the download of ScreenConnect.ClientSetup.exe. This attack is particularly insidious because the phishing page is hosted on a legitimate platform, complicating detection efforts.

Additionally, researchers observed the deployment of a VBS script masquerading as an Adobe document. Upon execution, this script disables security features and installs LogMeIn Rescue, enabling remote access without user consent.

Detection of these threats requires a comprehensive overview of the attack chain, from the phishing page to the execution and subsequent connections. Behavioral analysis in a sandbox environment is essential to unveil these complex attack sequences.

Enhancing Detection and Response

Traditional detection methods often fall short because the final payloads appear legitimate. Security analysts must focus on the entire sequence of events, including the phishing lure, download behavior, and resulting network connections, to accurately assess threats.

Utilizing tools like ANY.RUN can significantly improve threat response times, reducing the Tier 1 workload by up to 20% and cutting down on unnecessary escalations. This enables teams to act swiftly and prevent potential business impacts.

By adopting cloud-based analysis, organizations can enhance threat visibility, streamline threat response, and ultimately protect their assets from sophisticated phishing-to-RMM attacks.
Cyber Security News Tags:ANY.RUN, attack chains, cloud security, Cybersecurity, endpoint protection, IT support, LogMeIn Rescue, Malware, network security, Phishing, remote access, RMM tools, ScreenConnect, SOC workflows, threat detection

Post navigation

Previous Post: Critical MajorDoMo Vulnerability Enables Remote Code Execution
Next Post: Phishing Campaign Targets Users with Fake Event Invites

Related Posts

Critical RCE Flaw in Claude Code Patched by Anthropic Critical RCE Flaw in Claude Code Patched by Anthropic Cyber Security News
Threat Actors Allegedly Selling Monolock Ransomware on Dark Web Forums Threat Actors Allegedly Selling Monolock Ransomware on Dark Web Forums Cyber Security News
New HybridPetya Weaponizing UEFI Vulnerability to Bypass Secure Boot on Outdated Systems New HybridPetya Weaponizing UEFI Vulnerability to Bypass Secure Boot on Outdated Systems Cyber Security News
Chrome 151 Update Fixes Five Critical Security Flaws Chrome 151 Update Fixes Five Critical Security Flaws Cyber Security News
Hackers Target Android Users with Fake App Testing Invites Hackers Target Android Users with Fake App Testing Invites Cyber Security News
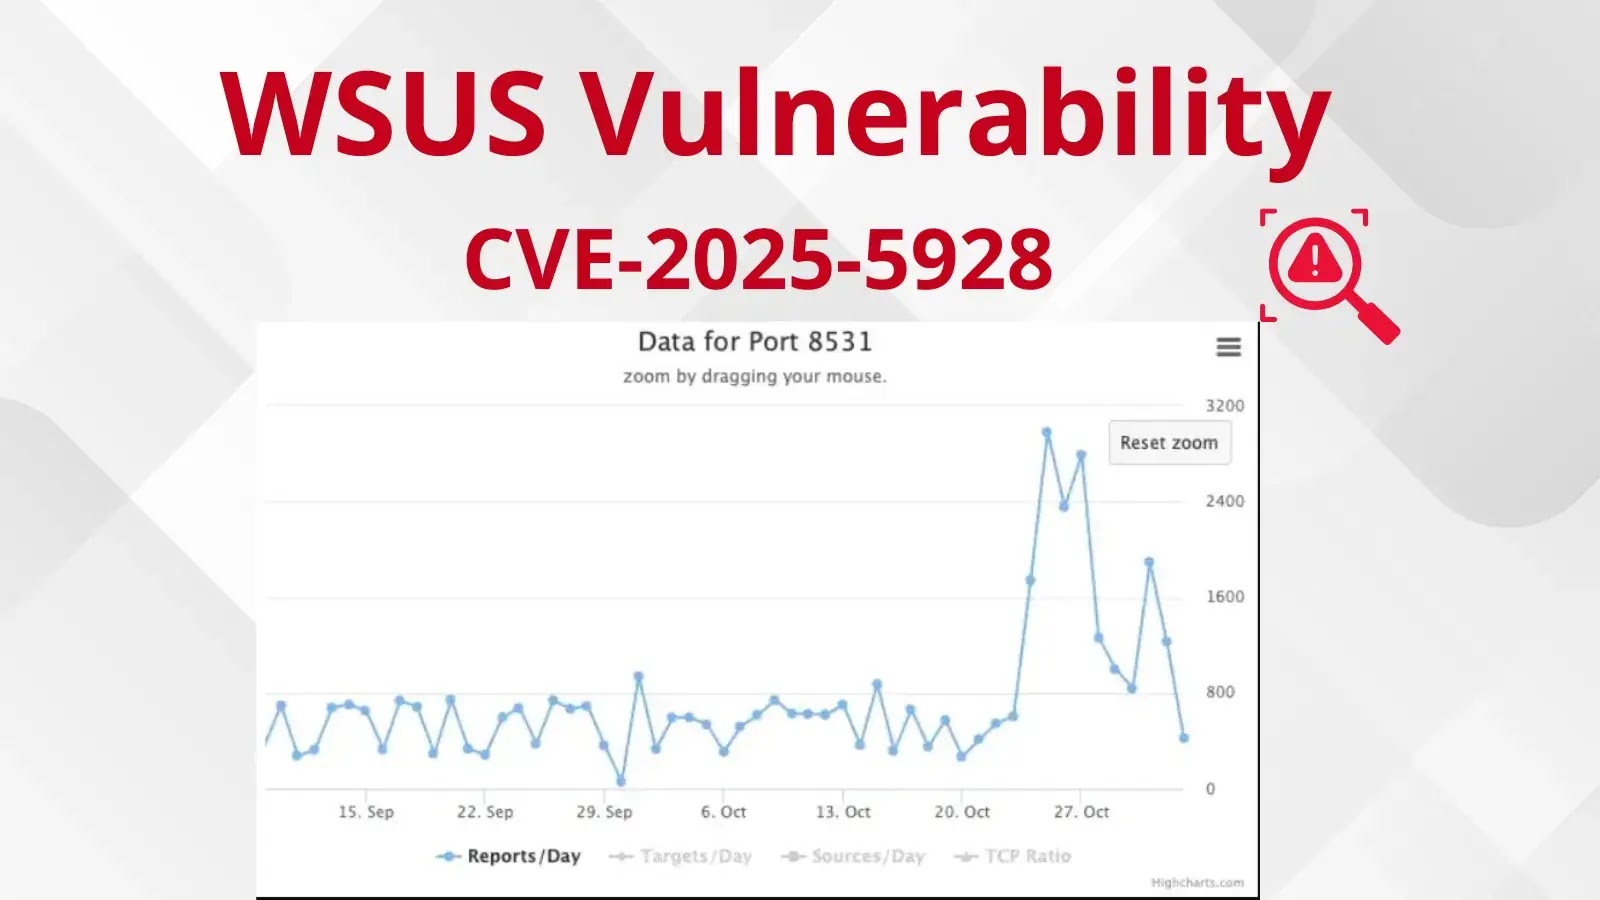
Hackers Actively Scanning for TCP Port 8530/8531 Linked to WSUS Vulnerability CVE-2025-59287 Hackers Actively Scanning for TCP Port 8530/8531 Linked to WSUS Vulnerability CVE-2025-59287 Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Hackers Exploit Fake Game Cheats to Steal Data
  • Ryan Davis: Transition from Hacker to CISO at New Charter
  • Top Cyber Threats for US Businesses in October 2026
  • Critical Citrix XenServer Flaw Exposes Hosts to Attack
  • Russian Hackers Exploit iOS, Android via Watering Hole Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Hackers Exploit Fake Game Cheats to Steal Data
  • Ryan Davis: Transition from Hacker to CISO at New Charter
  • Top Cyber Threats for US Businesses in October 2026
  • Critical Citrix XenServer Flaw Exposes Hosts to Attack
  • Russian Hackers Exploit iOS, Android via Watering Hole Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark