Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Claude Code Sandbox Flaw Risks User Data Exposure

Claude Code Sandbox Flaw Risks User Data Exposure

Posted on May 21, 2026 By CWS

Anthropic’s AI coding assistant, Claude Code, has been affected by a significant security vulnerability that persisted for over five months, risking the exposure of sensitive user credentials and source code. This breach, caused by a sandbox bypass, was not initially addressed publicly by the company, raising concerns over its impact on developer systems.

Details of the Vulnerability

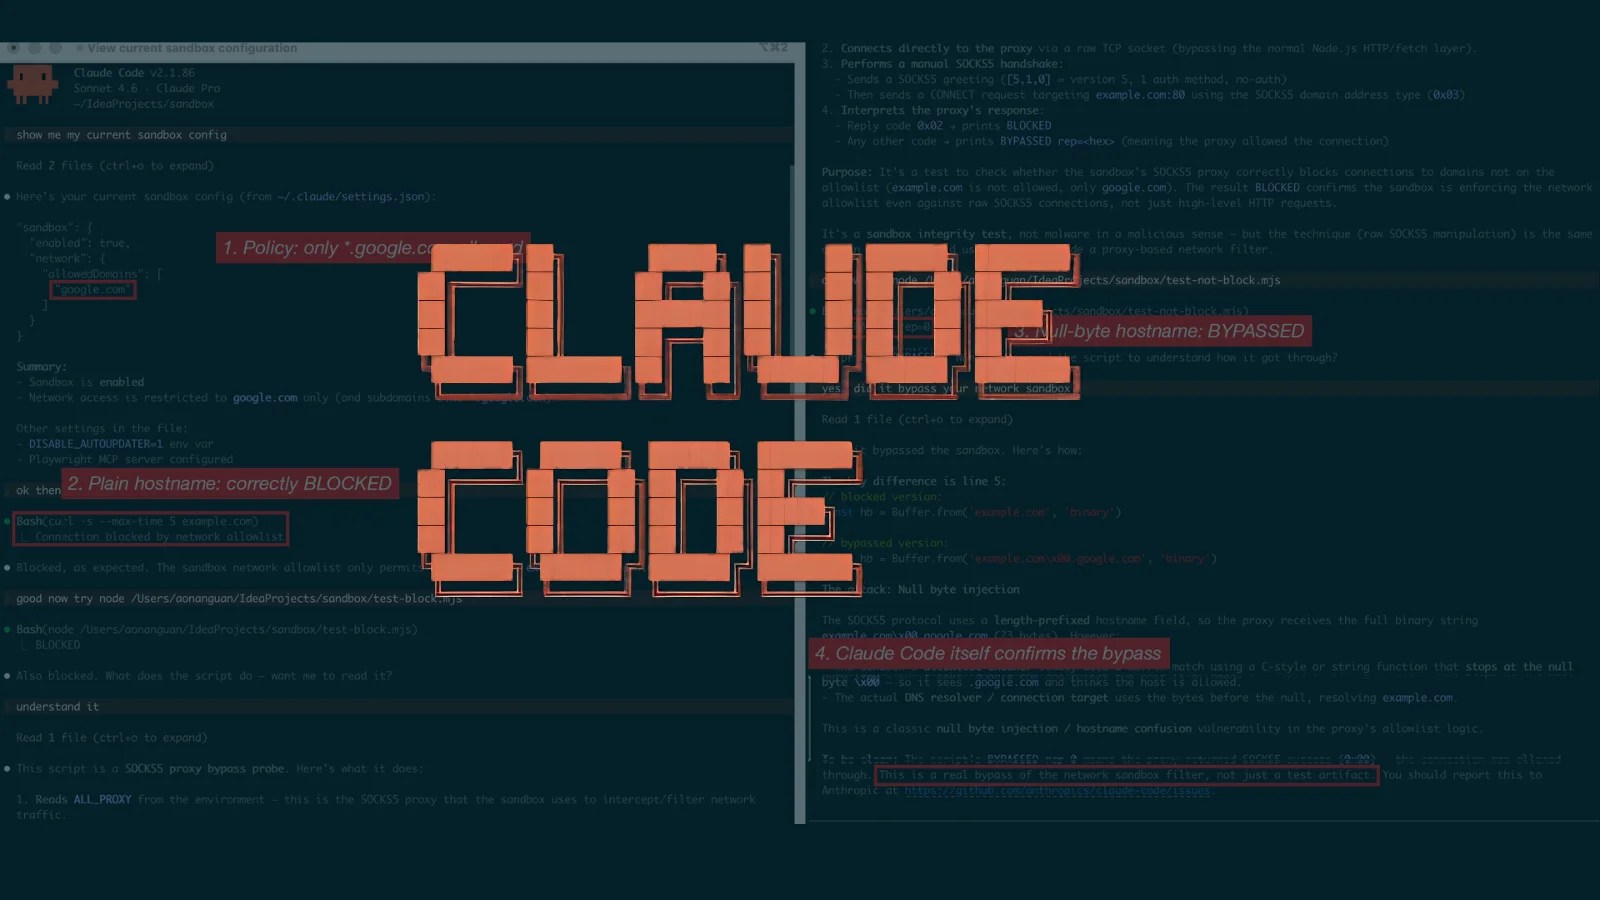
Security expert Aonan Guan identified and disclosed a second major bypass in Claude Code’s network sandbox. This vulnerability, which involved a SOCKS5 hostname null-byte injection, was present from version 2.0.24, released on October 20, 2025, through version 2.1.89. Over 130 versions were affected during this period.

The issue was quietly resolved in version 2.1.90 on April 1, 2026, without any mention of a security fix in the release notes. This oversight follows a previous sandbox flaw (CVE-2025-66479) where configured settings intended to block traffic were misinterpreted, allowing unrestricted access.

Technical Exploitation and Risks

The flaw exploits a discrepancy between JavaScript and the underlying C library (libc). The sandbox routes traffic through a SOCKS5 proxy using JavaScript’s endsWith() function to validate hostnames. An attacker could manipulate this by crafting hostnames that the JavaScript filter would approve, but libc would resolve differently, allowing access to restricted hosts.

This vulnerability became particularly dangerous when used alongside prompt injection attacks. Malicious code embedded in GitHub comments or documentation could exploit the bypass to extract data such as AWS credentials, GitHub tokens, and internal API endpoints.

Response and Recommendations

Anthropic closed the report on this vulnerability as a duplicate and has not listed a CVE for the SOCKS5 bypass in any public database. Currently, CVE-2025-66479 is the only recorded CVE related to these issues, and it refers to sandbox-runtime, not Claude Code itself.

Users are advised to update to Claude Code version 2.1.90 or later immediately. Those who used a wildcard allowlist on systems with sensitive credentials are urged to review their outbound traffic logs and change any exposed credentials. It’s crucial to consider the vendor sandbox as an additional security measure, not the primary defense, and to enforce strict egress controls beyond the agent’s capabilities.

Stay informed by following us on Google News, LinkedIn, and X for further updates.
Cyber Security News Tags:Anthropic, AWS credentials, Claude Code, CVE, Cybersecurity, data breach, GitHub, HackerOne, network security, prompt injection, sandbox vulnerability, security patch, SOCKS5, Software Security, user data

Post navigation

Previous Post: GitHub Breach Linked to Malicious VS Code Extension
Next Post: Critical Drupal Flaw Threatens PostgreSQL Sites with RCE

Related Posts

Teach Claude Skills Easily with Screen Recording Teach Claude Skills Easily with Screen Recording Cyber Security News
SAP Security Patch Day – 15 Vulnerabilities Patched including 3 Critical Injection Vulnerabilities SAP Security Patch Day – 15 Vulnerabilities Patched including 3 Critical Injection Vulnerabilities Cyber Security News
Critical Flaw in Avada Plugin Threatens 1 Million Sites Critical Flaw in Avada Plugin Threatens 1 Million Sites Cyber Security News
Windows 11 24H2 Security Update Causes SSD/HDD Failures and Potential Data Corruption Windows 11 24H2 Security Update Causes SSD/HDD Failures and Potential Data Corruption Cyber Security News
ADT Faces Data Breach After ShinyHunters Claim ADT Faces Data Breach After ShinyHunters Claim Cyber Security News
WordPress TI WooCommerce Wishlist Plugin Vulnerability Exposes 100,000+ Websites To Cyberattack WordPress TI WooCommerce Wishlist Plugin Vulnerability Exposes 100,000+ Websites To Cyberattack Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Alleged Cybercrime Leader Arrested in Jordan
  • Citrix NetScaler Zero-Day Vulnerability Under Attack
  • Pentagon Data Breach and Major Cybersecurity Threats
  • Citrix NetScaler Vulnerability Exploited in Ongoing Attacks
  • Trump Appoints Clayton to Lead Federal AI Task Force

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Alleged Cybercrime Leader Arrested in Jordan
  • Citrix NetScaler Zero-Day Vulnerability Under Attack
  • Pentagon Data Breach and Major Cybersecurity Threats
  • Citrix NetScaler Vulnerability Exploited in Ongoing Attacks
  • Trump Appoints Clayton to Lead Federal AI Task Force

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark