Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Microsoft Defender Enhances Security with Auto Device Isolation

Microsoft Defender Enhances Security with Auto Device Isolation

Posted on May 26, 2026 By CWS

Microsoft Defender for Endpoint has introduced a significant advancement in cybersecurity with its new automatic device isolation feature. Designed to curtail the spread of ransomware, this capability disconnects compromised devices from the network as soon as a high-confidence threat is identified, eliminating the need for human intervention.

Automatic Isolation in Action

The automatic isolation function is part of Microsoft’s broader Automatic Attack Disruption framework. When the system detects an active ransomware attack or a complex intrusion, it promptly severs the affected device’s connection to the wider network. This action prevents attackers from accessing further systems while maintaining a communication link with the Defender for Endpoint service.

This feature ensures that security analysts maintain visibility into the compromised device, even as it remains isolated. Currently, this capability is targeted at end-user workstations managed by Microsoft Defender for Endpoint, excluding servers and unmanaged devices.

How the Automatic Attack Disruption Works

Microsoft Defender XDR leverages a vast array of signals from endpoints, identities, emails, and SaaS applications to create a comprehensive incident overview. Upon confirmation of an attack, such as ransomware spread or Business Email Compromise (BEC), the system initiates containment actions at the incident level.

Specifically, for device isolation, the compromised asset is disconnected from the network, preventing it from being used for lateral movement, data exfiltration, or further ransomware deployment. This isolation is tactically applied only to the devices directly involved, minimizing disruption to business operations.

Ensuring Effective and Safe Isolation

Microsoft has implemented several safeguards to ensure that automatic isolation does not hinder business activities. These include time-limited containment, allowing automatic reversal of isolation after a set period, and operator override, enabling security teams to release isolation after thorough investigation and remediation.

Additionally, scoped targeting ensures that only implicated devices are isolated, and not the entire network. Organizations can also set exclusion rules for critical business assets, allowing selective isolation rather than full network disconnection.

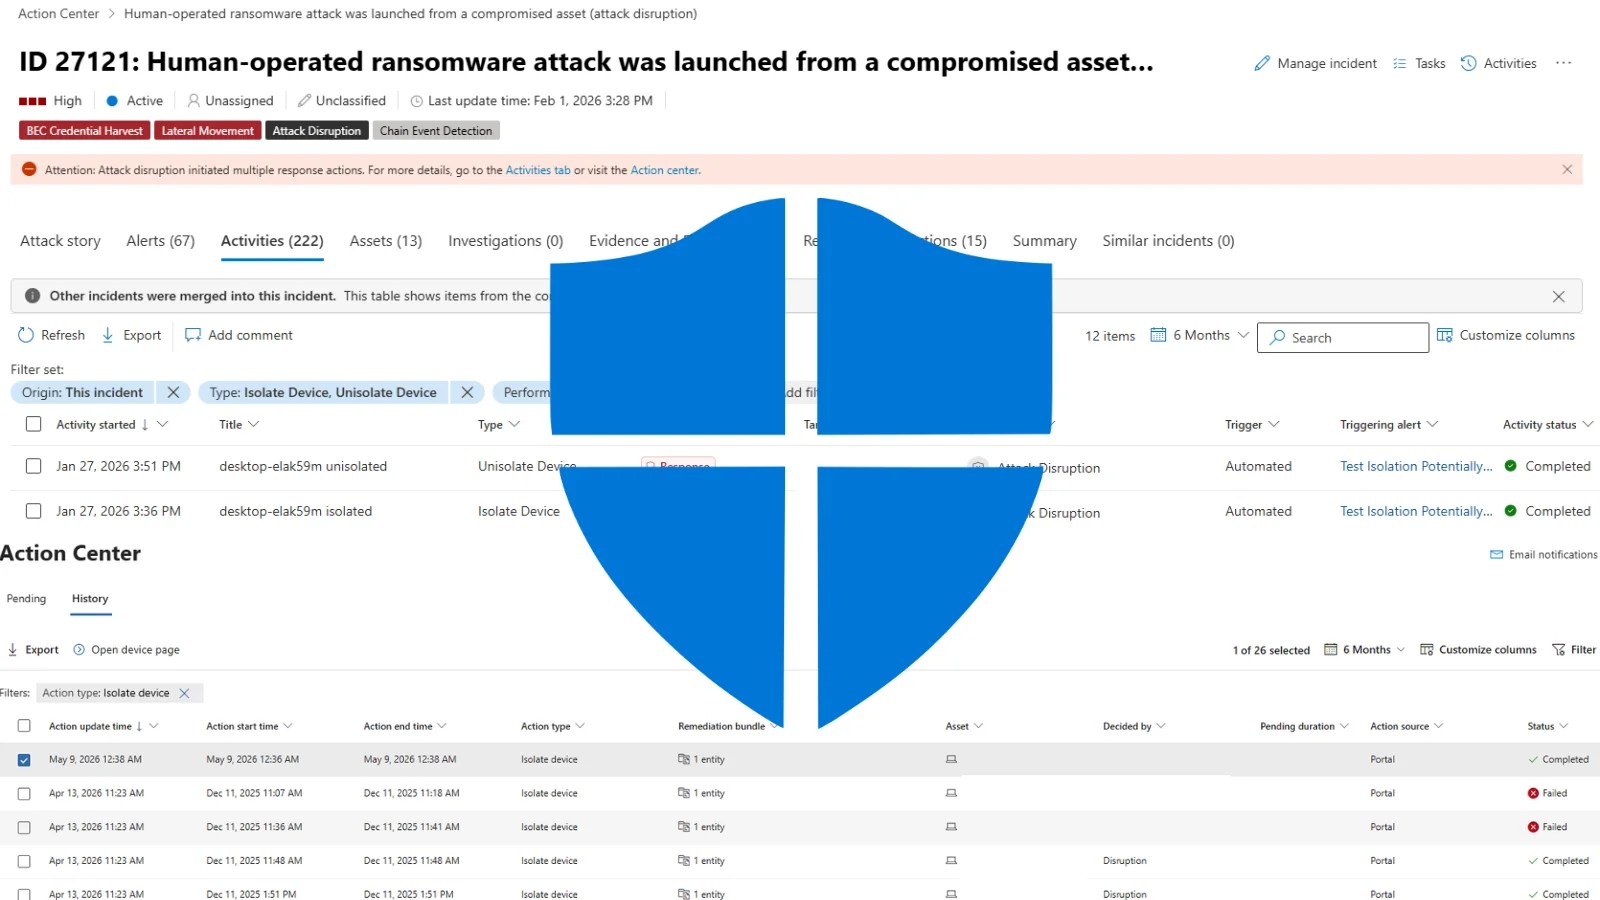
Once isolation is enacted, security operators can audit the entire activity in the Microsoft Defender portal, accessing detailed logs of each isolation event, including timestamps and triggering alerts. The Action Center provides a comprehensive historical log of all isolation actions, offering insight into their status and origins.

By automating the containment process upon detection of a high-confidence threat, Microsoft Defender for Endpoint significantly reduces the time between threat detection and response. This approach limits the attack’s potential damage, preserving both financial resources and operational productivity.
Cyber Security News Tags:Automatic Attack Disruption, cyber threats, Cybersecurity, Device Isolation, endpoint security, IT security, Microsoft Defender, network security, Ransomware, security operations

Post navigation

Previous Post: Anthropic Enhances Claude’s Security with New Integrations
Next Post: Marlin AI: Revolutionizing SaaS Security with Autonomous Analysis

Related Posts

Employee Devices at Risk from Bandwidth-Sharing Apps Employee Devices at Risk from Bandwidth-Sharing Apps Cyber Security News
New Microsoft 365 Admin Feature Let Admins Control Link Creation Policies New Microsoft 365 Admin Feature Let Admins Control Link Creation Policies Cyber Security News
15,200 OpenClaw Systems at Risk Due to Internet Exposure 15,200 OpenClaw Systems at Risk Due to Internet Exposure Cyber Security News
RedNovember Hackers Attacking Government and Technology Organizations to Deploy Backdoor RedNovember Hackers Attacking Government and Technology Organizations to Deploy Backdoor Cyber Security News
Hackers Actively Attacking Cisco and Palo Alto Networks VPN Gateways to Gain Login Access Hackers Actively Attacking Cisco and Palo Alto Networks VPN Gateways to Gain Login Access Cyber Security News
SecSuite: Comprehensive AI-Driven Security Platform Unveiled SecSuite: Comprehensive AI-Driven Security Platform Unveiled Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • TP-Link Faces New Lawsuits Over Security and China Links
  • Hackers Exploit Terraform Workflows to Spread Malware
  • Anthropic Accelerates AI Bug Reports for Open Source Security
  • Citrix Addresses Critical NetScaler Vulnerability
  • Top Container Image Scanning Tools of 2026

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • TP-Link Faces New Lawsuits Over Security and China Links
  • Hackers Exploit Terraform Workflows to Spread Malware
  • Anthropic Accelerates AI Bug Reports for Open Source Security
  • Citrix Addresses Critical NetScaler Vulnerability
  • Top Container Image Scanning Tools of 2026

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark