Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Linux SCTP Vulnerability Risks Full Root Access

Critical Linux SCTP Vulnerability Risks Full Root Access

Posted on August 7, 2026 By CWS

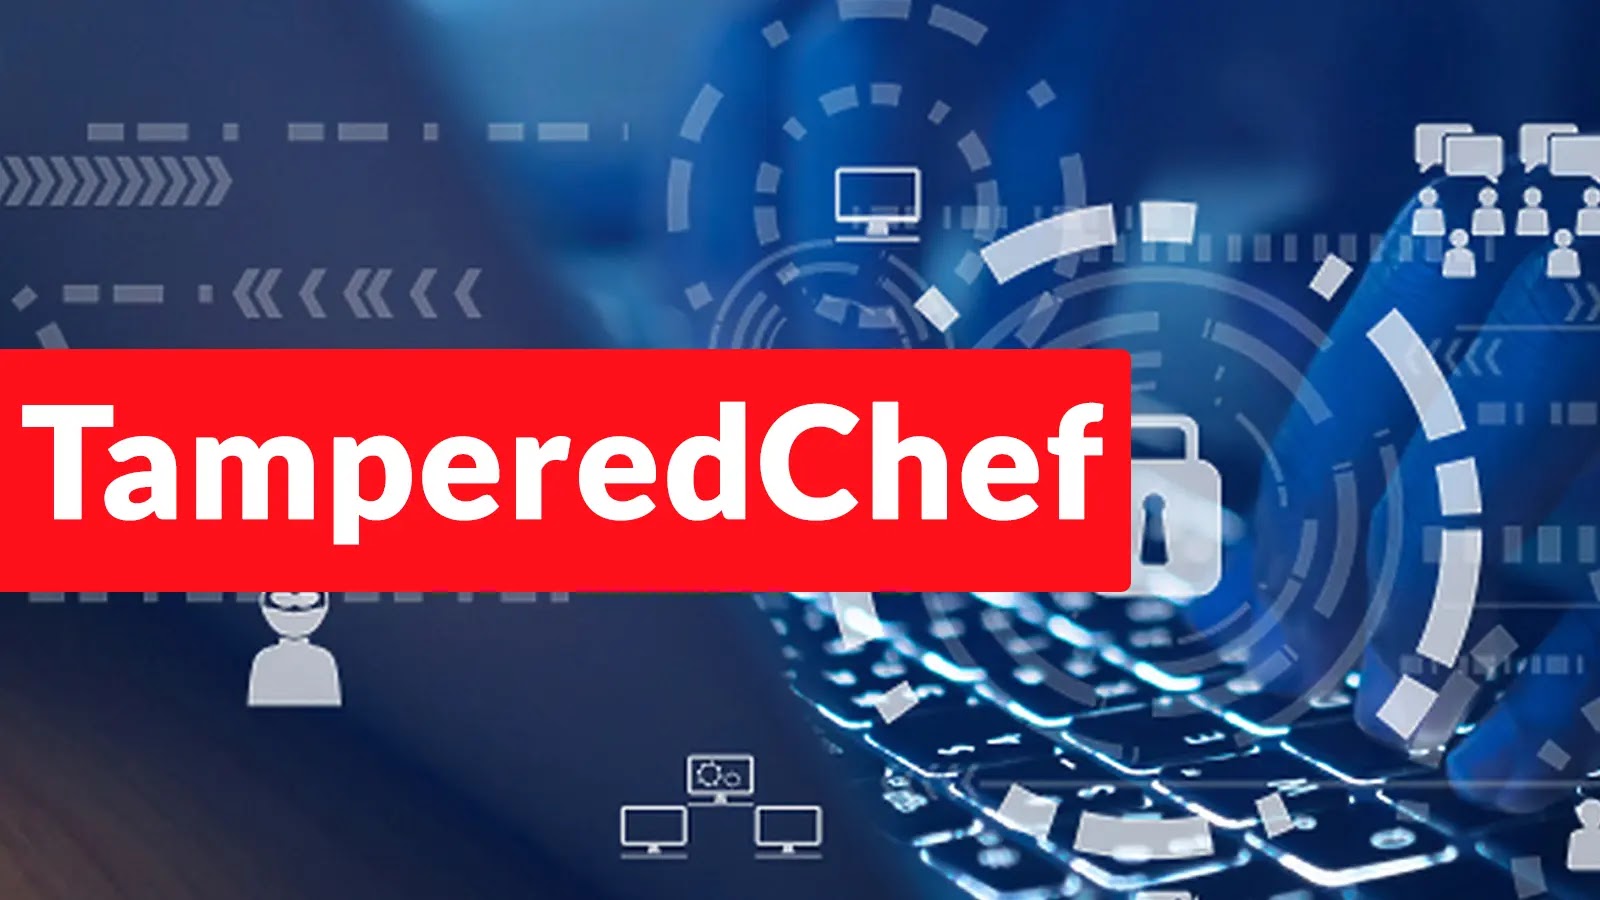
A newly revealed vulnerability in the Linux kernel, identified as CVE-2026-64564 and nicknamed SCTPhantom, poses significant security risks by enabling attackers to escalate privileges from non-root local user to full root access. This flaw, which can also facilitate container escapes to compromise the host system, has been present since Linux version 2.6.25, dating back to December 2007.

Understanding the Vulnerability

This security issue originates from a use-after-free bug in the SCTP Dynamic Address Reconfiguration feature of the Linux kernel. Notably, it affects the handling of ASCONF chunks, a component that allows for dynamic network path adjustments in SCTP associations as specified in RFC 5061.

The core of the issue is an identity mismatch during the DEL-IP delete operation. While the kernel validates this operation using the packet’s source address, it relies on a separate cached pointer for the actual network path selection. This inconsistency can be exploited by orchestrating a sequence of ASCONF commands, leading to a use-after-free condition when the kernel dereferences memory linked to a stale network path.

Exploitation and Impact

Researchers from the TencentOS Security Team, utilizing their Corvus AI system, crafted a privilege-escalation chain from this vulnerability. Their method involves reclaiming freed transport memory using a packet socket ring buffer, thereby leaking a kernel memory address. This leak allows bypassing KASLR by examining the interrupt descriptor table.

Subsequent exploitation leverages a second use-after-free scenario, where attacker-controlled SCTP authentication key data constructs a fake kernel object graph. This ultimately triggers the commit_creds function, granting global root access without the need for shellcode or ROP chains. Furthermore, the exploit enables container-to-host escapes under certain conditions, highlighting the severity of this flaw.

Mitigation and Recommendations

The Linux community has responded with an upstream patch, identified as commit 9b2854f86f0b, which addresses the vulnerability by rejecting DEL-IP requests affecting active transports. This patch has been backported to several stable kernel branches, including 6.6.148, 6.12.101, 6.18.42, and 7.1.6.

Given the vulnerability’s CVSS v4.0 score of 8.5, indicating high severity due to its low attack complexity and significant impact, system administrators, particularly those managing SCTP-enabled kernels in containerized environments, are urged to apply the patch immediately. This proactive step is crucial to mitigate the potential for exploitation and ensure system integrity.

In conclusion, the SCTPhantom vulnerability serves as a critical reminder of the importance of timely patch management and the ongoing need for vigilant security practices in software development and deployment environments.
Cyber Security News Tags:container escape, Corvus AI, CVE, CVE-2026-64564, Exploit, Kernel, Linux, Patch, privilege escalation, root access, SCTP, Security, system administrators, use-after-free, Vulnerability

Post navigation

Previous Post: Critical WordPress Vulnerability Allows Remote Code Execution
Next Post: 800 Malicious npm Packages Spread Cross-Platform Malware

Related Posts

TamperedChef Hacking Campaign Leverages Common Apps to Deliver Payloads and Gain Remote Access TamperedChef Hacking Campaign Leverages Common Apps to Deliver Payloads and Gain Remote Access Cyber Security News
Ollama Vulnerability Exposes Servers to Data Leaks Ollama Vulnerability Exposes Servers to Data Leaks Cyber Security News
Qilin Ransomware Exploits RDP History for Network Infiltration Qilin Ransomware Exploits RDP History for Network Infiltration Cyber Security News
Google Introduces MTCs to Secure HTTPS from Quantum Risks Google Introduces MTCs to Secure HTTPS from Quantum Risks Cyber Security News
AI Agents Exploit PaperCut Vulnerabilities Globally AI Agents Exploit PaperCut Vulnerabilities Globally Cyber Security News
Cisco ASA/FTD 0-Day Vulnerability Exploited for Authentication Bypass Cisco ASA/FTD 0-Day Vulnerability Exploited for Authentication Bypass Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Dark Project Ransomware Offers 80% Cut to Hackers
  • White House Network Found Hosting Residential Proxies
  • OpenSSH SSHole Vulnerability Exploited by Hackers
  • Massive WordPress Vulnerability Exploit Attempts Uncovered
  • Ahold Delhaize Faces Major Financial Hit from Cyberattack

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Dark Project Ransomware Offers 80% Cut to Hackers
  • White House Network Found Hosting Residential Proxies
  • OpenSSH SSHole Vulnerability Exploited by Hackers
  • Massive WordPress Vulnerability Exploit Attempts Uncovered
  • Ahold Delhaize Faces Major Financial Hit from Cyberattack

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark