Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
FamousSparrow’s New Backdoor Targets Exchange Servers

FamousSparrow’s New Backdoor Targets Exchange Servers

Posted on September 17, 2026 By CWS

FamousSparrow, a known cyber espionage group, has unveiled a new backdoor named SparroWocky, targeting public-facing Microsoft Exchange servers. This development demonstrates how exposed email systems can serve as long-term infiltration points in government networks.

Focus on Latin American Targets

The campaign, which began in mid-2025, has primarily affected governments in Latin America, including Argentina, Ecuador, and Venezuela. Researchers from Welivesecurity noted that 90 percent of the group’s activities from mid-2025 into 2026 were centered in this region. This marks a significant shift from the group’s previous global operations.

FamousSparrow, active since 2019, has been linked to attacks leveraging ProxyLogon vulnerabilities. The recent focus on Exchange servers continues this trend, as detailed in a report shared with Cyber Security News (CSN).

SparroWocky’s Advanced Features

SparroWocky, identified as FamousSparrow’s main implant since August 2025, is a modular backdoor designed in C language. It combines data exfiltration and remote access with sophisticated techniques to avoid detection, making it a potent tool for stealthy operations.

The backdoor employs a three-part loader, leveraging a legitimate executable, a malicious DLL, and an encrypted payload. This approach ensures the malicious code blends seamlessly with trusted programs, complicating detection efforts.

Defense Strategies Against SparroWocky

To mitigate the threat posed by SparroWocky, organizations must prioritize patching of internet-facing Exchange servers and limit unnecessary public access. The backdoor’s use of TLS and RC4 encryption for communications underscores the need for robust security monitoring.

Security teams should actively look for signs of DLL side-loading, abnormal services, and suspicious network activity. Regularly reviewing logs and isolating compromised systems can help contain the impact of any breaches.

Ultimately, this campaign highlights the importance of maintaining a proactive defense posture, with continuous monitoring and rapid response capabilities to address evolving cyber threats.
Cyber Security News Tags:Backdoor, cyber attack, Cybersecurity, Espionage, Exchange servers, FamousSparrow, Latin America, Malware, network security, SparroWocky

Post navigation

Previous Post: ISC Updates BIND 9 to Fix 14 Critical Flaws
Next Post: BIND 9 Update Resolves 14 Vulnerabilities in DNS Server

Related Posts

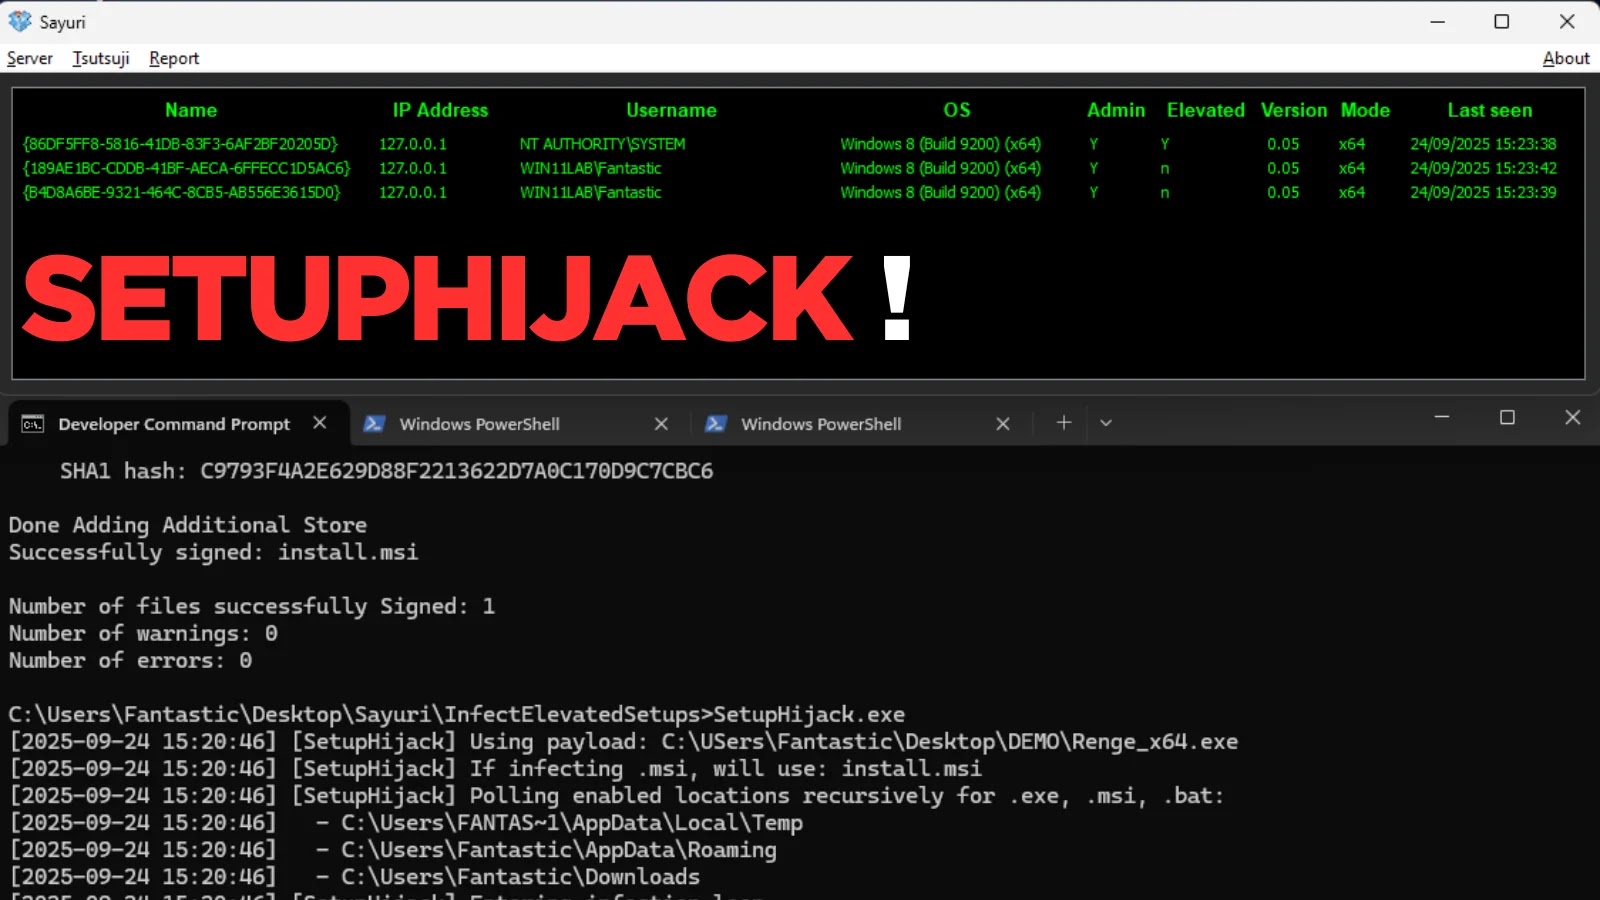
SetupHijack Tool Exploits Race Conditions and Insecure File Handling in Windows Installer Processes SetupHijack Tool Exploits Race Conditions and Insecure File Handling in Windows Installer Processes Cyber Security News
Microsoft Introduces Efficiency Mode in Teams for Low-End Devices Microsoft Introduces Efficiency Mode in Teams for Low-End Devices Cyber Security News
VMware Tools and Aria 0-Day Vulnerability Exploited for Privilege Escalation and Code Execution VMware Tools and Aria 0-Day Vulnerability Exploited for Privilege Escalation and Code Execution Cyber Security News
Critical Apache Tika Core Vulnerability Exploited by Uploading Malicious PDF Critical Apache Tika Core Vulnerability Exploited by Uploading Malicious PDF Cyber Security News
Red Hat Breach Exposes 5000+ High Profile Enterprise Customers at Risk Red Hat Breach Exposes 5000+ High Profile Enterprise Customers at Risk Cyber Security News
Cyber Attackers Use Zoom and PDF Setups to Infiltrate PCs Cyber Attackers Use Zoom and PDF Setups to Infiltrate PCs Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CyberStrikeAI Automates Windows Domain Control for Hackers
  • Synology NAS Under Siege: C3RB3R Ransomware Attacks Exploit Flaws
  • Mercado Bitcoin Halts Operations After Cyber Breach
  • Exploit Released for Windows WinSock Security Flaw
  • Critical Cybersecurity Events: CVEs, Botnets, and Phishing

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CyberStrikeAI Automates Windows Domain Control for Hackers
  • Synology NAS Under Siege: C3RB3R Ransomware Attacks Exploit Flaws
  • Mercado Bitcoin Halts Operations After Cyber Breach
  • Exploit Released for Windows WinSock Security Flaw
  • Critical Cybersecurity Events: CVEs, Botnets, and Phishing

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark