Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
OpenCode Vulnerability Risks Unauthorized Code Execution

OpenCode Vulnerability Risks Unauthorized Code Execution

Posted on September 28, 2026 By CWS

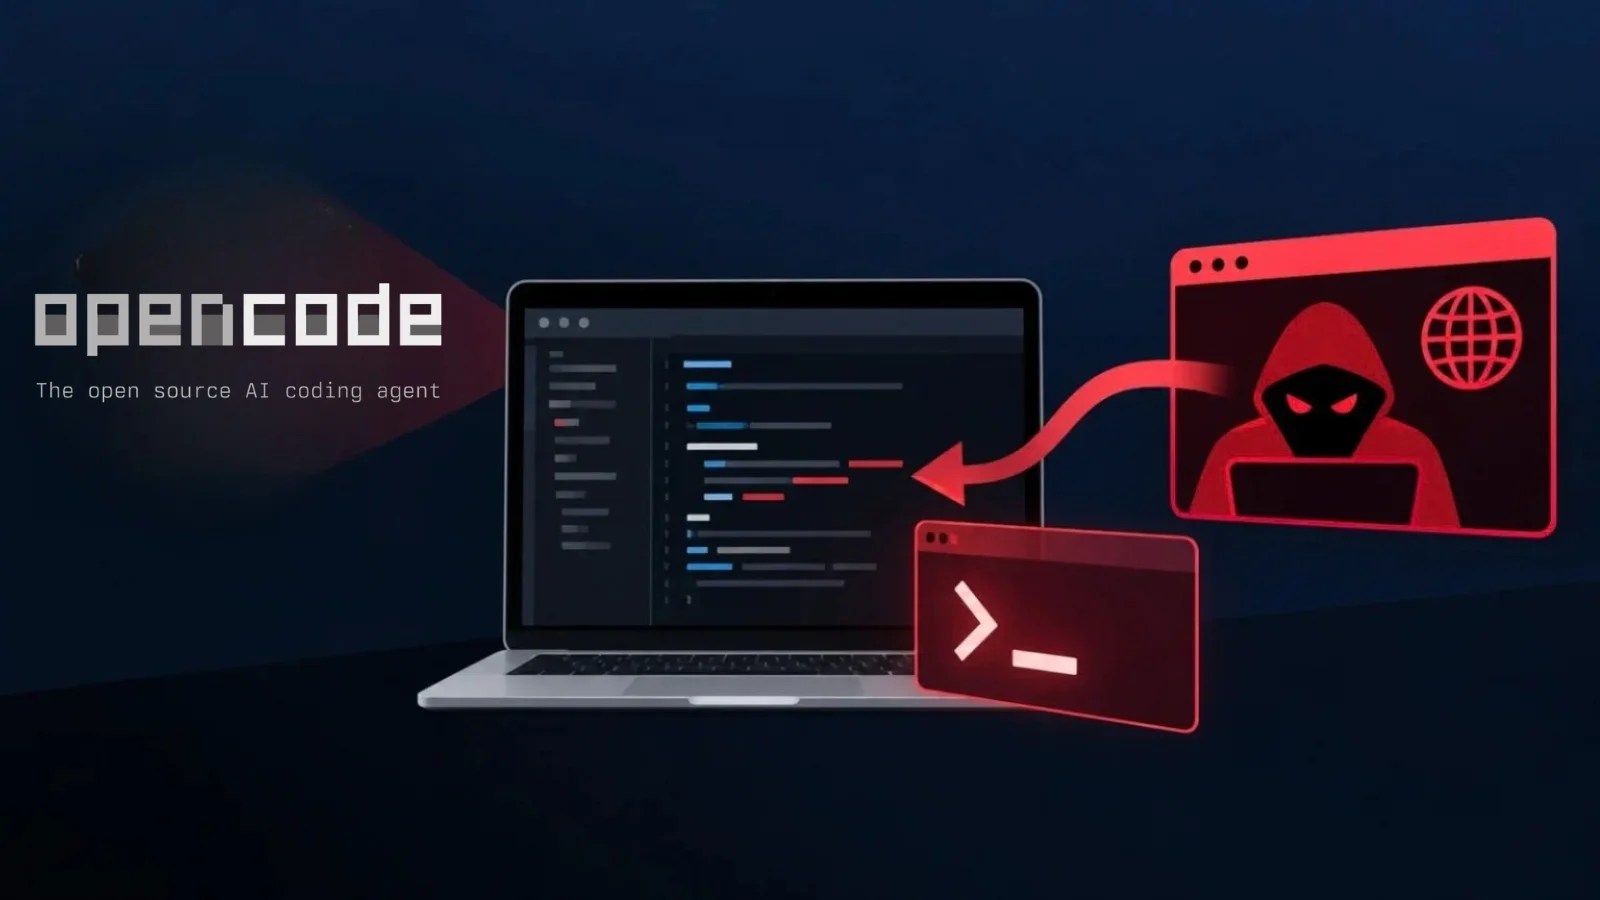
A significant security flaw has been identified in OpenCode, an open-source AI coding agent, that could permit harmful websites to execute unauthorized commands on a developer’s system.

Known as GHSA-632h-h47v-g4x4, this remote code execution vulnerability involves a content-type confusion in OpenCode’s /global/upgrade API. This flaw, combined with insecure handling of a potentially malicious upgrade target, was addressed by Anomaly in the update to OpenCode version 1.18.22.

OpenCode’s Integration and Security Concerns

Launched in June 2025, OpenCode has become a key tool in integrating language models into developer environments. Its popularity, with over 208,000 stars on GitHub and 16 million active monthly developers, underscores the critical nature of this security vulnerability.

The vulnerability primarily affects OpenCode’s browser interface, which operates through ‘opencode serve’ or ‘opencode web’. This interface listens on 127.0.0.1:4096 without default authentication, making it susceptible to unauthorized access.

Technical Details of the Vulnerability

According to Datadog Security Labs, the flaw affects versions 1.14.30 through 1.18.21 when installed using npm, pnpm, or Bun. The /global/upgrade endpoint can be manipulated to install a malicious package if an attacker supplies a URL to a remote tarball instead of a proper version target.

Attackers can exploit this by creating an archive with a harmful package.json preinstall script, running commands with the privileges of the OpenCode process. Although the server binds to localhost, a crafted webpage could trick a user’s browser into interacting with the local API using a method not blocked by CORS.

Preventive Measures and Security Recommendations

To mitigate this risk, developers using the affected versions should upgrade promptly to OpenCode 1.18.22 or later. This version enhances security by validating upgrade targets and rejecting inappropriate submissions, like text/plain content types.

Developers are also advised to configure OPENCODE_SERVER_PASSWORD for added security when using the web interface and to monitor for unusual package-manager activity as potential signs of compromise.

While password protection can reduce exposure, it is not a substitute for the critical patching provided in the latest update. Cached credentials in the browser may still be leveraged for malicious requests, emphasizing the importance of comprehensive security practices.

Cyber Security News Tags:AI coding agent, Anomaly, CORS protection, Cybersecurity, Datadog, developer security, GitHub, NPM, OpenCode, remote code execution, Security, Software Security, software update, Vulnerability, web security

Post navigation

Previous Post: Apple Fixes CoreGraphics Vulnerability in Older OS
Next Post: NeedyMantis Malware Ensures Long-Term Network Access

Related Posts

Join Free Webinar on AI-Powered Web App Security Join Free Webinar on AI-Powered Web App Security Cyber Security News
Bing Search Leads to Akira Ransomware Attack via SEO Poisoning Bing Search Leads to Akira Ransomware Attack via SEO Poisoning Cyber Security News
Microsoft Teams RCE Vulnerability Let Attackers Read, Write and Delete Messages Microsoft Teams RCE Vulnerability Let Attackers Read, Write and Delete Messages Cyber Security News
Microsoft 365 Under Threat: Phishing Panel Exploits OAuth Flow Microsoft 365 Under Threat: Phishing Panel Exploits OAuth Flow Cyber Security News
Threat Actors Advertising AI-Enhanced Metamorphic Crypter with Claims of Windows Defender Bypass Threat Actors Advertising AI-Enhanced Metamorphic Crypter with Claims of Windows Defender Bypass Cyber Security News
FBI and Thai Authorities Combat Southeast Asia Cyber Scams FBI and Thai Authorities Combat Southeast Asia Cyber Scams Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Oracle PeopleSoft Vulnerability Exploited by ShinyHunters
  • NeedyMantis Malware Ensures Long-Term Network Access
  • OpenCode Vulnerability Risks Unauthorized Code Execution
  • Apple Fixes CoreGraphics Vulnerability in Older OS
  • Hackers Expose AI-Driven Attack System

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Oracle PeopleSoft Vulnerability Exploited by ShinyHunters
  • NeedyMantis Malware Ensures Long-Term Network Access
  • OpenCode Vulnerability Risks Unauthorized Code Execution
  • Apple Fixes CoreGraphics Vulnerability in Older OS
  • Hackers Expose AI-Driven Attack System

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark