Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Apache Struts Flaws Risk Remote Code Execution

Apache Struts Flaws Risk Remote Code Execution

Posted on October 6, 2026 By CWS

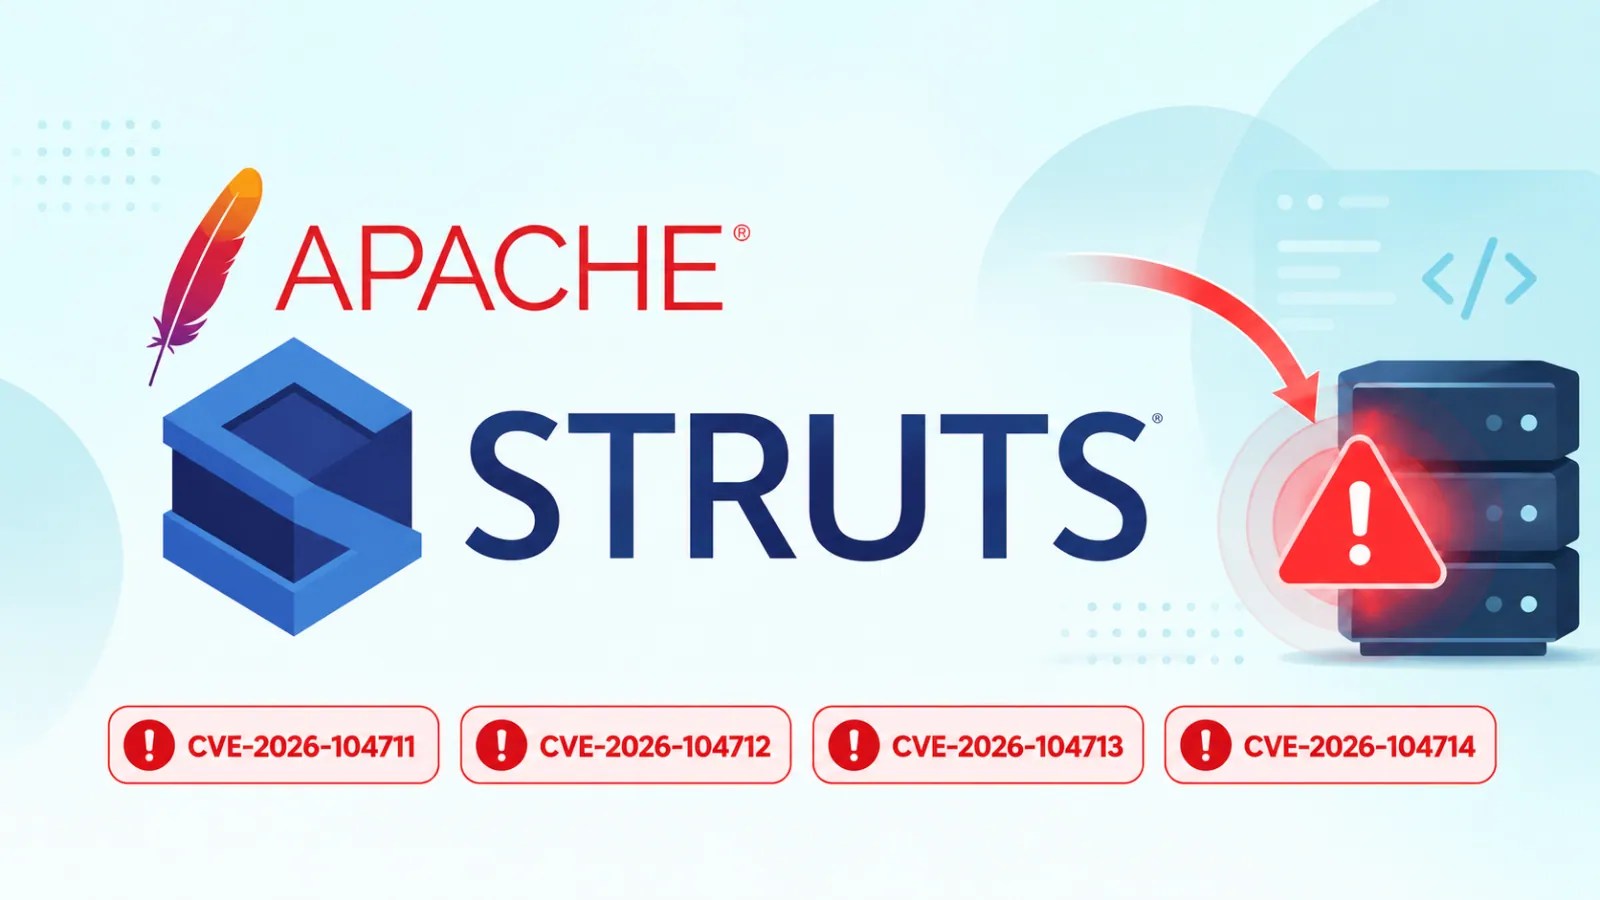
Several vulnerabilities have been identified in Apache Struts that could lead to severe security risks such as remote code execution, denial-of-service, and unintended data exposure. Organizations using affected versions should consider upgrading to Struts 7.4.0 or later, or Struts 6.12.0 or later for the 6.x line, to mitigate these issues.

Understanding the Vulnerabilities

The discovered issues are present in different components of the Apache Struts framework, and the level of exposure varies based on individual application configurations. Of the identified vulnerabilities, three are rated as Moderate, while a vulnerability in the REST plugin has been deemed Important. There is no evidence of these vulnerabilities being actively exploited at this time.

One significant vulnerability, identified as CVE-2026-104711, involves OGNL injection in the legacy RESTful action mapper. This flaw could allow a crafted request to execute remote code if an application uses this mapper. This vulnerability affects Struts versions 2.0.0 through 2.3.37, 2.5.0 through 2.5.33, and 6.0.0 through 6.11.0. It is also present in versions 7.0.0 through 7.3.0 if the OGNL allowlist feature is disabled. Applications using the default mapper or the REST plugin are not affected.

Potential Impacts and Mitigation Strategies

Another vulnerability, CVE-2026-104712, permits small requests to generate unexpectedly large responses, posing a risk of resource exhaustion. This issue arises when request parameters are used with java.math.BigDecimal properties and rendered via the Struts tag library. Affected versions include Struts 2.5.14 through 2.5.33, 6.0.0 through 6.11.0, and 7.0.0 through 7.3.0. Organizations can temporarily mitigate this by implementing a custom BigDecimal converter.

The CVE-2026-104713 vulnerability affects applications that utilize the optional REST plugin, allowing unbounded memory use from oversized requests. This flaw impacts Struts versions from 2.1.8 to 2.3.37, 2.5.0 to 2.5.33, and 6.0.0 to 6.11.0, including 7.0.0 to 7.3.0. Updates have introduced a default character limit for request bodies, but organizations that cannot update should set their own limits at the server level.

Recommendations and Future Outlook

Another concern, CVE-2026-104714, involves shared localized message formatters for date or time arguments, which may cause data leakage between user requests. This vulnerability affects all versions up to 6.11.0 and 7.3.0. A temporary solution involves formatting dates before message interpolation.

To protect systems, administrators are encouraged to update affected deployments, review configurations, and enforce better security practices. Addressing these vulnerabilities is crucial in safeguarding applications against potential threats and ensuring data protection.
Cyber Security News Tags:Apache Struts, BigDecimal, CVE, Cybersecurity, data protection, IT security, memory exploitation, OGNL injection, remote code execution, REST plugin, security update, software update, Vulnerabilities

Post navigation

Previous Post: Hackers Target US Water Infrastructure via Industrial Controllers
Next Post: Ex-Engineer Jailed for Sabotage and Ransom Scheme

Related Posts

New SmartAttack Steals Sensitive Data From Air-Gapped Systems via Smartwatches New SmartAttack Steals Sensitive Data From Air-Gapped Systems via Smartwatches Cyber Security News
FIN7 Hackers Using Windows SSH Backdoor to Establish Stealthy Remote Access and Persistence FIN7 Hackers Using Windows SSH Backdoor to Establish Stealthy Remote Access and Persistence Cyber Security News
Critical Flaw in Synology DSM Risks Remote Exploitation Critical Flaw in Synology DSM Risks Remote Exploitation Cyber Security News
AI and Security: Key Insights from This Week’s Cyber Threats AI and Security: Key Insights from This Week’s Cyber Threats Cyber Security News
An Open-Source Tool to See Through Encrypted Traffic in Linux systems An Open-Source Tool to See Through Encrypted Traffic in Linux systems Cyber Security News
StealC Malware Targets Windows via Fake CAPTCHA StealC Malware Targets Windows via Fake CAPTCHA Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Ex-Engineer Jailed for Sabotage and Ransom Scheme
  • Apache Struts Flaws Risk Remote Code Execution
  • Hackers Target US Water Infrastructure via Industrial Controllers
  • AI Activity Causes Concerns for Wikipedia’s Security
  • AI Coding Assistant Exploited in Ransomware Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Ex-Engineer Jailed for Sabotage and Ransom Scheme
  • Apache Struts Flaws Risk Remote Code Execution
  • Hackers Target US Water Infrastructure via Industrial Controllers
  • AI Activity Causes Concerns for Wikipedia’s Security
  • AI Coding Assistant Exploited in Ransomware Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark