Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Severe ArangoDB Vulnerabilities Enable Critical Exploits

Severe ArangoDB Vulnerabilities Enable Critical Exploits

Posted on September 9, 2026 By CWS

ArangoDB, a popular database management system, is currently under scrutiny due to two significant vulnerabilities that could lead to unauthorized access and root-level code execution on compromised systems. These flaws, impacting versions up to 3.12.10.1, pose a serious threat to internet-facing databases and containerized environments.

Exploiting Authentication Bypass

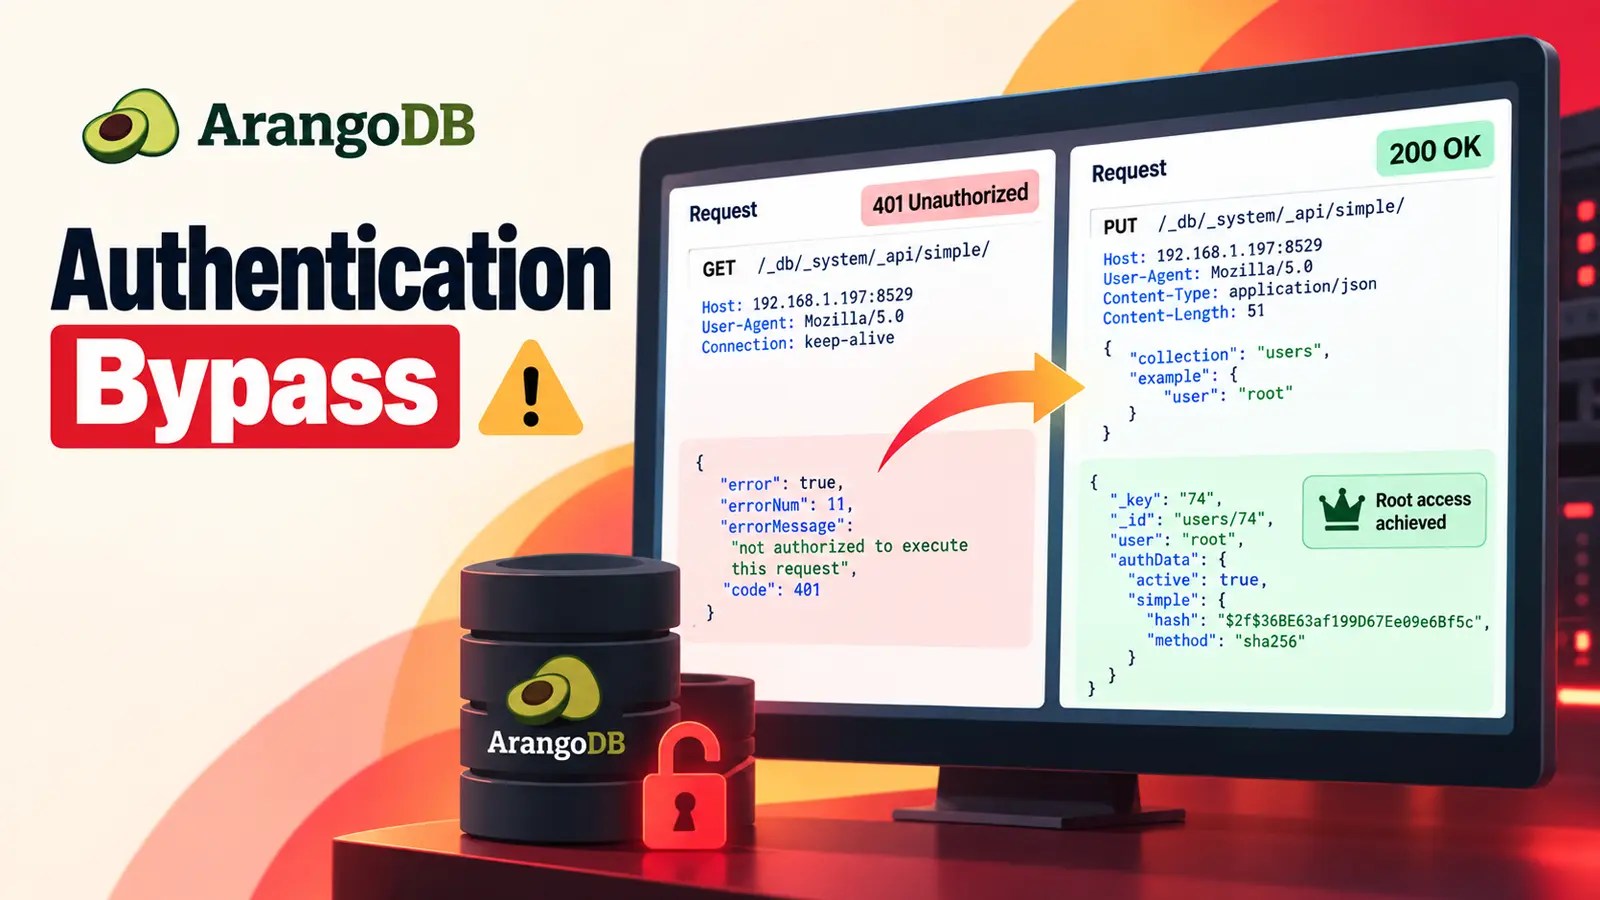
The first vulnerability, designated as GHSA-rrgq-978q-36mq, carries a CVSS 3.1 score of 9.8, highlighting its severity. The flaw allows attackers to bypass authentication by exploiting discrepancies in URL parsing. While ArangoDB’s default configuration requires authentication for paths starting with /_, the routing mechanism misinterprets URL-encoded versions of these paths as public, enabling unauthorized access.

This flaw allows attackers to access protected API endpoints without valid credentials, potentially retrieving sensitive data such as the root account password hash. The vulnerability was uncovered by Remedio analysts during a review of ArangoDB’s HTTP attack surface, emphasizing the risk of inconsistent request handling in critical systems.

Root-Level Code Execution Threat

The second vulnerability, identified as GHSA-rvhw-4hpw-9vrx and assigned a CVSS score of 9.9, involves ArangoDB’s handling of scheduled JavaScript tasks. By manipulating the isSystem parameter, attackers can execute tasks within the server’s highly privileged context, a domain typically reserved for internal operations.

This flaw arises from inadequate checks on the HTTP handler, allowing client-supplied values to determine execution privileges. Once a task is elevated to this context, it can perform actions like reading sensitive files, making outbound requests, and potentially leading to remote code execution. On official container images, where the ArangoDB process runs as root, this vulnerability becomes particularly dangerous.

Patch and Prevention Measures

ArangoDB was informed of these vulnerabilities on August 23, 2026, and quickly released patches in version 3.12.11 on August 31. Organizations using affected versions should upgrade immediately, limit database exposure to trusted networks, and rotate any potentially compromised credentials.

These incidents underscore the importance of consistent request handling and the dangers of allowing client inputs to affect system-level privileges. Developers are urged to standardize and verify requests uniformly across all handlers to prevent similar vulnerabilities.

The rapid response to patch these critical vulnerabilities highlights the need for prompt updates and access restrictions to safeguard against potential exploits. Keeping systems updated and monitoring for unusual activities are essential strategies in maintaining robust cybersecurity defenses.
Cyber Security News Tags:API security, ArangoDB, authentication bypass, container security, CVSS score, Cybersecurity, database security, JavaScript tasks, network security, remote code execution, root access, security flaw, software patch, system security, Vulnerability

Post navigation

Previous Post: New N0va Phishkit: Emerging Threat to North America and EU
Next Post: September 2026 Android Security Update Released

Related Posts

Cybercriminal Cryptocurrency Transactions Peaked in 2025 Following Nation‑State Sanctions Evasion Moves Cybercriminal Cryptocurrency Transactions Peaked in 2025 Following Nation‑State Sanctions Evasion Moves Cyber Security News
Malicious npm Package with 206k Downloads Attacking GitHub-Owned Repositories to Exfiltrate Tokens Malicious npm Package with 206k Downloads Attacking GitHub-Owned Repositories to Exfiltrate Tokens Cyber Security News
OpenAI Introduces AI Safety Bug Bounty Program OpenAI Introduces AI Safety Bug Bounty Program Cyber Security News
Sweet Security Enhances AI Safety with New Blocking Features Sweet Security Enhances AI Safety with New Blocking Features Cyber Security News
AI Enhances Security with Realistic Attack Simulations AI Enhances Security with Realistic Attack Simulations Cyber Security News
Revolut Data Breach: Sensitive Customer Info Exposed Revolut Data Breach: Sensitive Customer Info Exposed Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Google Chrome Update Patches 247 Security Vulnerabilities
  • Critical Atlassian Vulnerability Fixed Across Key Products
  • 32 Zero-Day Vulnerabilities Exploited at Pwn2Own 2026
  • Wikimedia Identifies Unauthorized OpenAI Agent Activities
  • Over 100 Sites Compromised Using Fake Cloudflare Checks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Google Chrome Update Patches 247 Security Vulnerabilities
  • Critical Atlassian Vulnerability Fixed Across Key Products
  • 32 Zero-Day Vulnerabilities Exploited at Pwn2Own 2026
  • Wikimedia Identifies Unauthorized OpenAI Agent Activities
  • Over 100 Sites Compromised Using Fake Cloudflare Checks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark