Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
VEXAIoT Revolutionizes IoT Security Testing with AI

VEXAIoT Revolutionizes IoT Security Testing with AI

Posted on July 13, 2026 By CWS

Researchers have unveiled VEXAIoT, a cutting-edge AI-driven framework designed to automate the identification and exploitation of vulnerabilities in Internet of Things (IoT) devices. This innovative system employs multi-agent technology to streamline reconnaissance and attack execution in controlled test environments.

AI Agents Enhance Vulnerability Detection

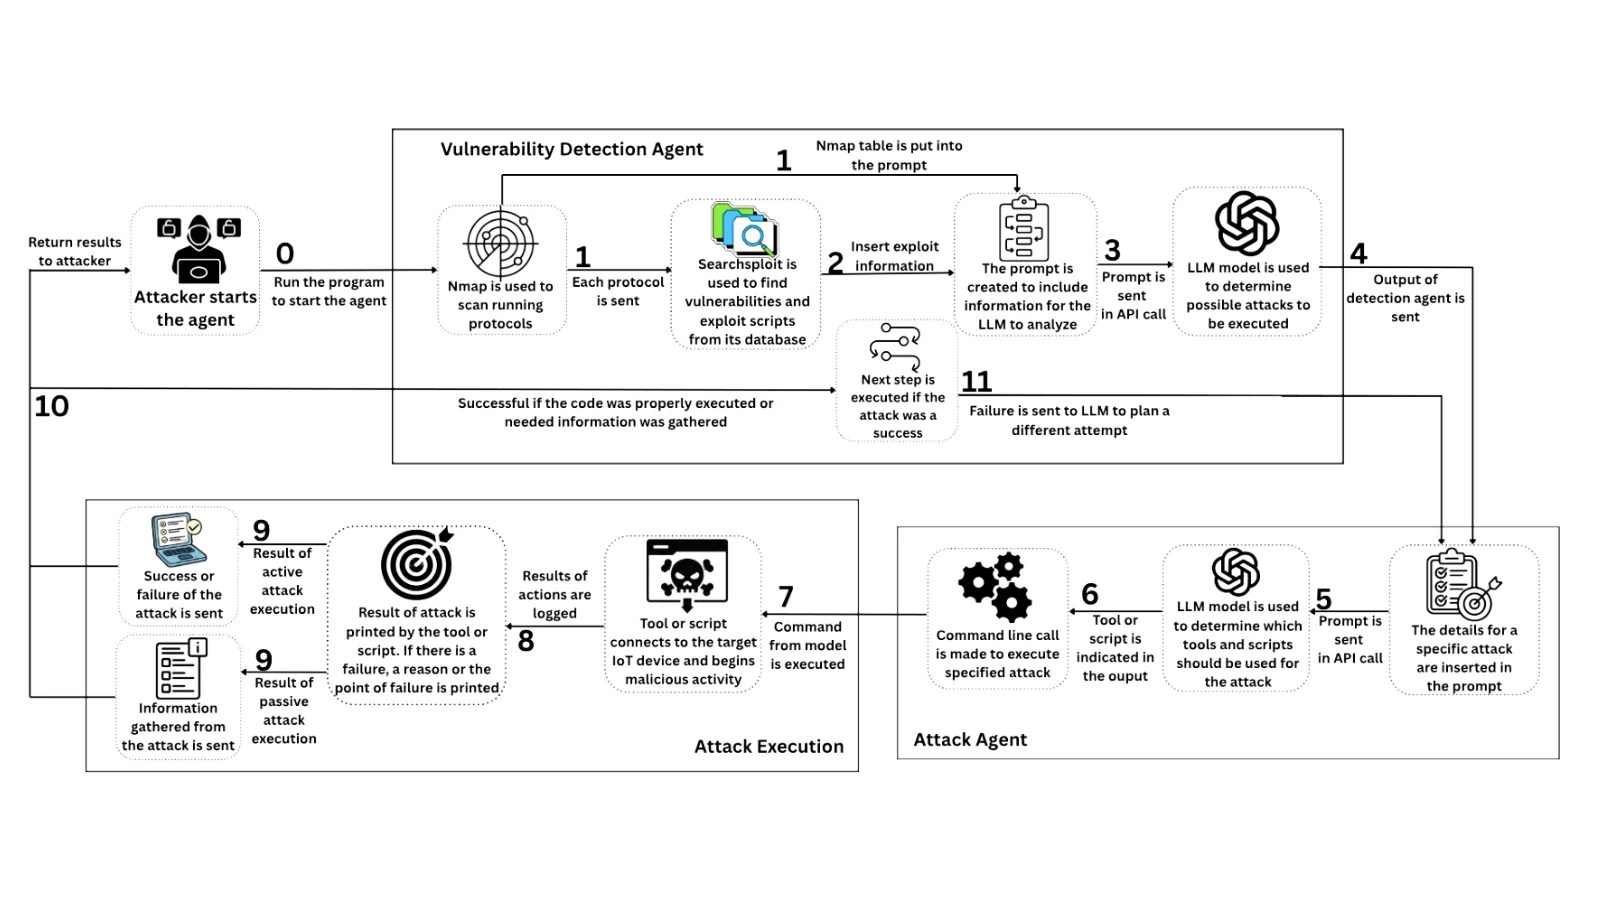
VEXAIoT leverages large language model agents to coordinate activities such as reconnaissance, strategy formulation, command creation, and result verification within isolated security setups. The system comprises two interconnected agents: a vulnerability detection agent and an attack execution agent.

The detection agent is responsible for scanning target devices, identifying open ports, services, and network protocols using tools like Nmap. It then cross-references this data with resources like Searchsploit and the Exploit Database to match software versions to known vulnerabilities and public proof-of-concept exploits.

Streamlined Attack Execution Process

Once vulnerabilities are identified, the attack execution agent selects appropriate tools, formulates commands, and attempts the planned exploits. It considers factors such as vulnerability severity and tool availability to devise an effective attack plan.

In scenarios requiring valid credentials, VEXAIoT initially attempts credential recovery or network traffic interception. The framework can adjust its approach based on error messages and execution outputs, enhancing its ability to successfully complete attacks.

Testing and Success Rates

VEXAIoT’s capabilities were tested on IoTGoat, a deliberately vulnerable OpenWrt-based IoT firmware, and Metasploitable2, a known vulnerable machine. In tests with IoTGoat, VEXAIoT achieved a 94.5% success rate across 200 attack attempts, with full success in scenarios like cross-site scripting and remote code execution.

In the Metasploitable2 tests, the framework successfully exploited vulnerabilities such as the VSFTPD backdoor and exposed database credentials, achieving a 95% success rate across 260 executions. Most attacks were completed swiftly, although password cracking required more time.

Future Implications and Challenges

The study emphasizes the potential of AI-powered agents in authorized IoT penetration testing, highlighting their efficiency in vulnerability assessment and exploit validation. However, challenges such as hallucinated outputs, invalid commands, and the need for enhanced human oversight remain significant obstacles.

While the framework demonstrated promising results in controlled environments, researchers caution against its use on systems without explicit authorization. Continued development and rigorous testing are necessary to ensure safety and efficacy in real-world applications.

Cyber Security News Tags:AI agents, AI in cybersecurity, Cybersecurity, exploit execution, IoT security, IoT testing, IoT vulnerabilities, security framework, VEXAIoT, vulnerability discovery

Post navigation

Previous Post: June 2026 Cybersecurity M&A: 37 Key Deals Unveiled
Next Post: Forg365 PhaaS Exploits Microsoft 365 with Advanced Tactics

Related Posts

FBI Shuts Down LeakBase Cybercrime Hub FBI Shuts Down LeakBase Cybercrime Hub Cyber Security News
ClingSTUN Backdoor Targets IoT Devices for Remote Access ClingSTUN Backdoor Targets IoT Devices for Remote Access Cyber Security News
Top SCA Tools of 2026: Comprehensive Review Top SCA Tools of 2026: Comprehensive Review Cyber Security News
AI-Powered Free Security-Audit Checklist 2026 AI-Powered Free Security-Audit Checklist 2026 Cyber Security News
Critical Fluentd Vulnerabilities Threaten System Security Critical Fluentd Vulnerabilities Threaten System Security Cyber Security News
Kazuar Malware: A Stealthy Tool for Cyber Espionage Kazuar Malware: A Stealthy Tool for Cyber Espionage Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical NGINX Vulnerabilities Risk Server Stability
  • Critical Flaw in Collabora CODE App Exploited by Hackers
  • Windows 11 Update Disrupts Remote Desktop Connectivity
  • Cisco Alerts on Exploited Vulnerability in Email Gateway
  • Optimize MSSP Efficiency by Reducing Tier 1 Bottlenecks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical NGINX Vulnerabilities Risk Server Stability
  • Critical Flaw in Collabora CODE App Exploited by Hackers
  • Windows 11 Update Disrupts Remote Desktop Connectivity
  • Cisco Alerts on Exploited Vulnerability in Email Gateway
  • Optimize MSSP Efficiency by Reducing Tier 1 Bottlenecks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark