Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
GitLab Addresses Critical AI Agent Security Vulnerability

GitLab Addresses Critical AI Agent Security Vulnerability

Posted on August 27, 2026 By CWS

GitLab has issued a crucial security update to address a high-severity vulnerability in its Duo Claude AI agent, potentially allowing authenticated developers to execute arbitrary commands within continuous integration (CI) pipeline environments. This vulnerability, identified as CVE-2026-18252, affects GitLab Enterprise Edition and has a CVSS score of 7.3.

Immediate Update Recommendations

The security flaw impacts various versions of GitLab EE, prompting the release of patched versions 19.3.1, 19.2.5, and 19.1.7 on August 26, 2026. GitLab urges self-managed users to update their systems immediately. The issue does not require action from GitLab Dedicated customers, as GitLab.com is already updated.

The vulnerability was caused by the AI agent processing configurations from user-controlled sources. Under specific circumstances, an authenticated user with Developer-role permissions could exploit this flaw to execute arbitrary commands in a CI environment, posing significant risks to organizations utilizing AI-assisted workflows in software development.

Potential Risks and Impacts

CI pipelines often manage sensitive resources like source code, build artifacts, and cloud tokens. An attacker with command execution capabilities could access such secrets, modify artifacts, or infiltrate connected development infrastructure. GitLab classified this as an Inclusion of Functionality from Untrusted Control Sphere issue, a vulnerability type that arises when applications execute functionality based on user-controlled input without adequate security measures.

The affected versions range from GitLab EE 18.9 through 19.3.1. Exploiting this flaw requires network access, low privileges, and user interaction, with significant impacts on confidentiality and integrity. However, there is no direct availability impact. This issue was reported through GitLab’s HackerOne bug bounty program by security researcher thwin_htet.

Security Enhancements and Recommendations

While GitLab has not shared technical proof-of-concept details or evidence of active exploitation, the patch also addresses other vulnerabilities affecting both the Community and Enterprise Editions. These include denial-of-service issues, improper access controls, compliance framework bypasses, and more.

Administrators are advised to prioritize upgrading to the latest supported versions. Single-node deployments may experience downtime during database migrations, whereas multi-node setups can leverage GitLab’s zero-downtime upgrade procedures. This incident underscores the growing security challenges posed by AI agents in developer platforms.

Organizations should treat AI automation as an extension of code-execution infrastructure, implement strict access controls on agent configurations, isolate CI jobs, limit accessible secrets, and continuously monitor pipeline activities to detect unauthorized command executions.
Cyber Security News Tags:AI security, CI pipeline, CVE-2026-18252, Cybersecurity, developer tools, enterprise software, GitLab, security patch, software update, Vulnerability

Post navigation

Previous Post: Operation Bluebird Revives Twitter Identity Amid X Corp Rebrand
Next Post: PaperCut Vulnerability Actively Exploited, Emergency Patch Released

Related Posts

Shai-Hulud 2.0 Malware Attack Compromised 30,000 Repositories and Stolen 500 GitHub Usernames and Tokens Shai-Hulud 2.0 Malware Attack Compromised 30,000 Repositories and Stolen 500 GitHub Usernames and Tokens Cyber Security News
Best Network Security Providers for Healthcare Best Network Security Providers for Healthcare Cyber Security News
Researchers Unmasked Russia’s Most Secretive FSB’s Spy Network Researchers Unmasked Russia’s Most Secretive FSB’s Spy Network Cyber Security News
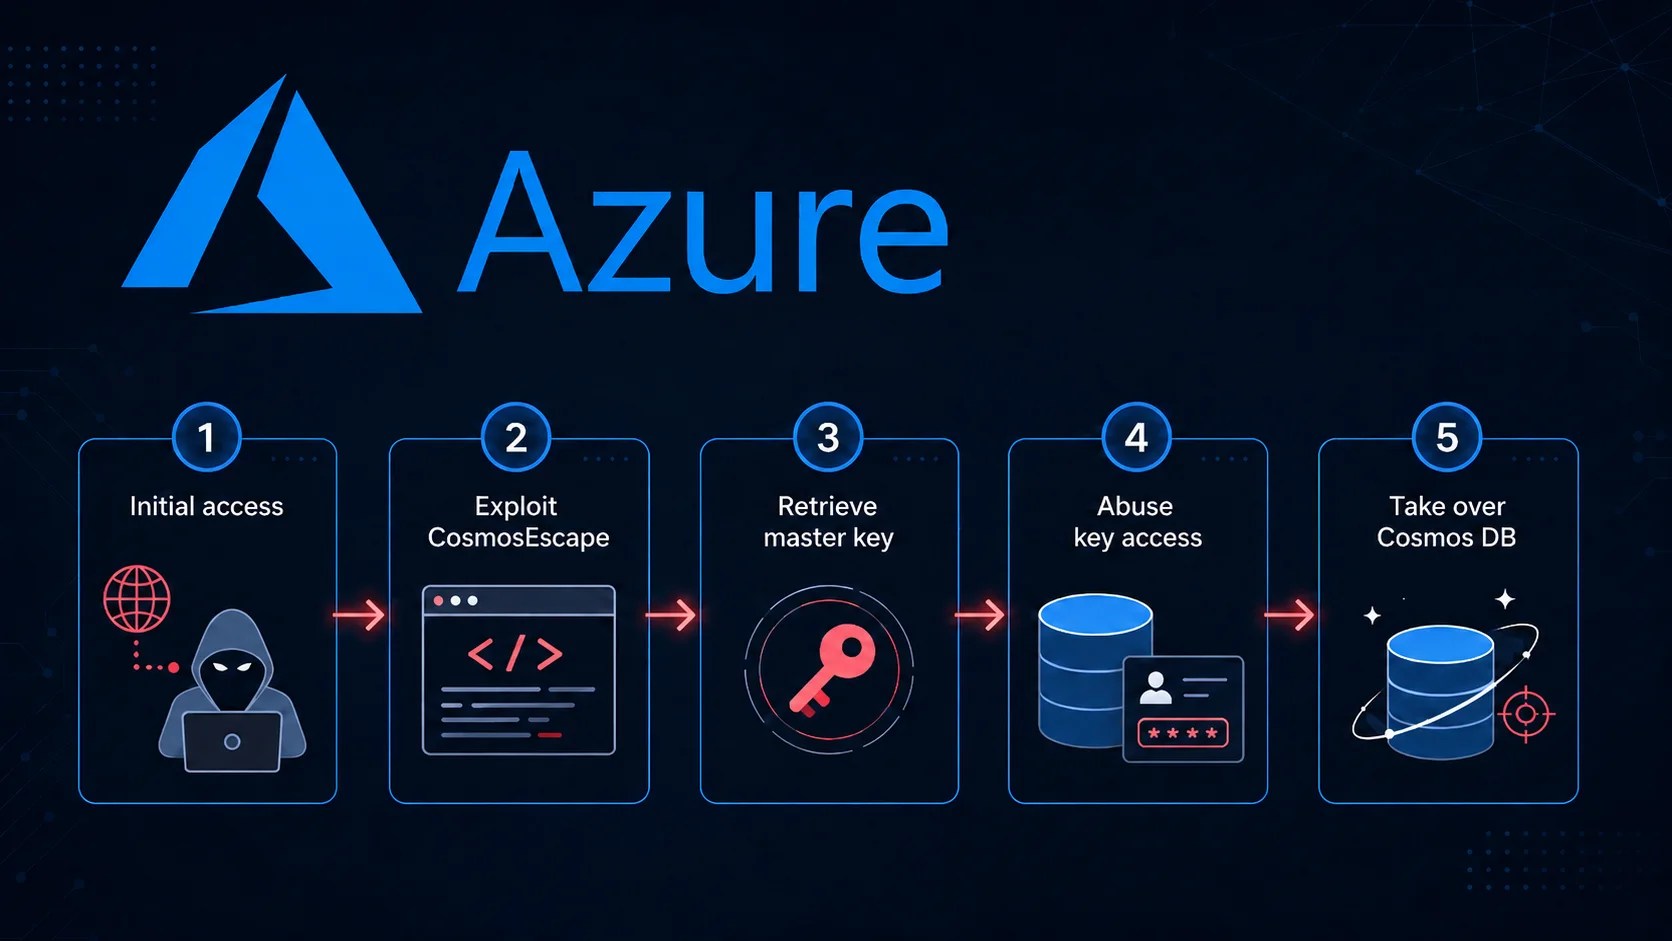
Critical CosmosEscape Flaw in Azure Cosmos DB Uncovered Critical CosmosEscape Flaw in Azure Cosmos DB Uncovered Cyber Security News
Apache Tomcat Patches Critical Security Vulnerabilities Apache Tomcat Patches Critical Security Vulnerabilities Cyber Security News
New Sophisticated Phishing Attack Mimic as Google Support to Steal Logins New Sophisticated Phishing Attack Mimic as Google Support to Steal Logins Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Urgent Patch for Major Check Point Vulnerability Released
  • Google Fixes Pixel Zero-Day Vulnerability Amid Attacks
  • Russian Enterprises Face Threats from Cyber Groups
  • TP-Link Camera Vulnerabilities Threaten User Privacy
  • AI-Driven Data Breach Notified to Spanish Authorities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Urgent Patch for Major Check Point Vulnerability Released
  • Google Fixes Pixel Zero-Day Vulnerability Amid Attacks
  • Russian Enterprises Face Threats from Cyber Groups
  • TP-Link Camera Vulnerabilities Threaten User Privacy
  • AI-Driven Data Breach Notified to Spanish Authorities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark