Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Chrome 151 Update Addresses Critical Security Flaws

Chrome 151 Update Addresses Critical Security Flaws

Posted on August 7, 2026 By CWS

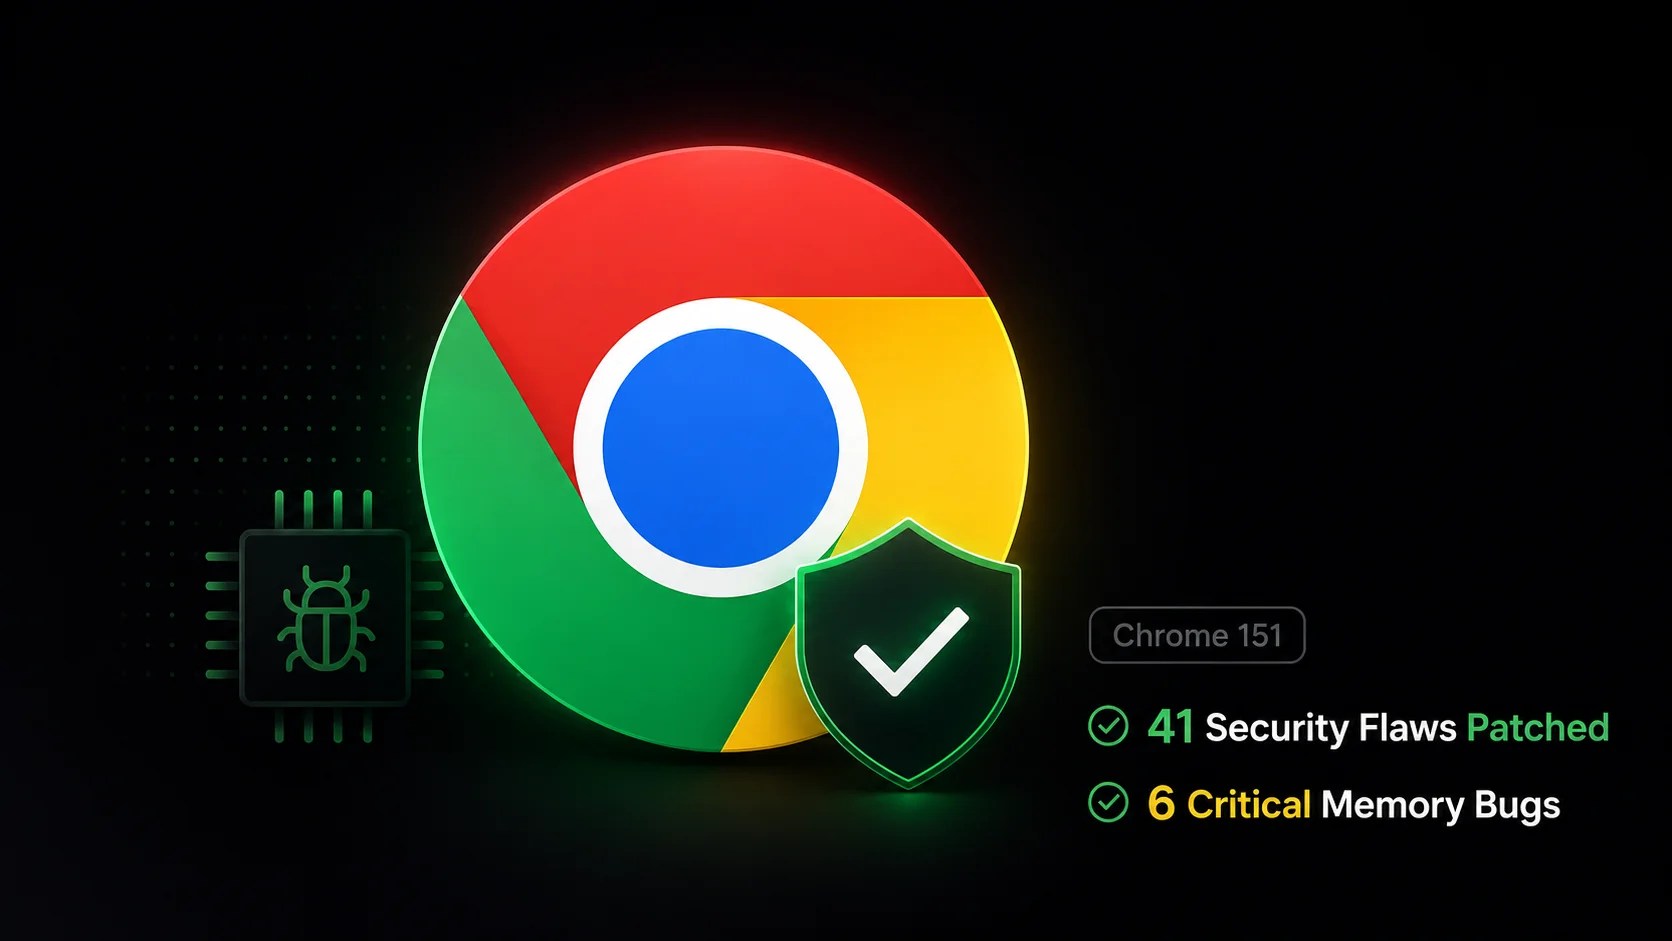
Google has initiated the release of Chrome version 151, targeting the mitigation of 41 security vulnerabilities, including six critical memory-safety issues. These flaws pose risks such as browser crashes, corruption of memory, and the potential for executing malicious code.

Details of the Chrome 151 Release

The new version, 151.0.7922.108/.109, is being distributed to Windows and macOS users, with Linux systems receiving version 151.0.7922.108. Google stated that the rollout would occur gradually over the coming days and weeks, advising users to update promptly once available.

Addressing Critical Memory Flaws

A significant focus of this update is on rectifying use-after-free vulnerabilities, which occur when a program continues to use memory that has already been freed. Such vulnerabilities can be exploited by attackers who may lure users to specially crafted websites.

Notably, two critical use-after-free issues impact WebGL, Chrome’s technology for rendering graphics. These are cataloged as CVE-2026-19137 and CVE-2026-19170. Additionally, issues with Chrome’s Aura UI framework, Skia graphics library, and Views interface component have been addressed.

Comprehensive Vulnerability Patching

In addition to the critical issues, Google has resolved CVE-2026-19157, an out-of-bounds write vulnerability in ANGLE, Chrome’s graphics translation layer. Furthermore, 35 high-severity vulnerabilities affecting various browser components are patched, including the V8 JavaScript engine, GPU process, HTML renderer, and more.

The update addresses a spectrum of memory-related issues, such as heap buffer overflows, out-of-bounds writes, and uninitialized memory usage, enhancing overall browser security.

Importance of Immediate Updates

Given that browsers handle untrusted data from diverse web sources, these updates are crucial. Externally reported issues include an insufficient validation flaw in Contextual Tasks (CVE-2026-19169), for which Google awarded $5,000 to researcher Sven Dysthe. Contributions from OpenAI Codex Security, Hap Security, and QED Audit were also recognized.

Details of the vulnerabilities and proof-of-concept information remain undisclosed until a majority of users have updated, minimizing the risk of exploitation. Users can update Chrome via the browser menu under Help > About Google Chrome, which will initiate the download and prompt a relaunch.

Organizations are advised to prioritize the deployment of Chrome 151 across managed environments to mitigate exposure to these vulnerabilities.
Cyber Security News Tags:ANGLE, browser safety, browser vulnerabilities, Chrome 151, critical bugs, Cybersecurity, Google Chrome, malicious code, memory corruption, memory flaws, security update, Skia, software update, use-after-free, WebGL

Post navigation

Previous Post: AI Impacts Cybersecurity: Key Developments Unveiled
Next Post: Malware Exploits Windows Hello Keys for Entra ID Access

Related Posts

Threat Actors Using Fake Travel Websites to Infect Users’ PCs with XWorm Malware Threat Actors Using Fake Travel Websites to Infect Users’ PCs with XWorm Malware Cyber Security News
Critical Rails Vulnerability Threatens Cloud Security Critical Rails Vulnerability Threatens Cloud Security Cyber Security News
Salesforce Fixes Major Marketing Cloud Security Flaws Salesforce Fixes Major Marketing Cloud Security Flaws Cyber Security News
Beyond CVEs – Turning Visibility into Action with ASM Beyond CVEs – Turning Visibility into Action with ASM Cyber Security News
Google to Flag Apps on Play Store that Use Excessive Amount of battery Google to Flag Apps on Play Store that Use Excessive Amount of battery Cyber Security News
Microsoft Teams Set to Introduce Highly Anticipated Multitasking Functionality Microsoft Teams Set to Introduce Highly Anticipated Multitasking Functionality Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AI Platform ARTEX Used in Massive Cybersecurity Breach
  • OpenSSH Urges Immediate Patch for Critical Authentication Flaw
  • Android Malware Exploits Streaming App Ads to Steal Data
  • Japan Unveils Urgent Cybersecurity Initiative Amid Attacks
  • OpenAI Introduces GPT-6 Cyber for Enhanced Security

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AI Platform ARTEX Used in Massive Cybersecurity Breach
  • OpenSSH Urges Immediate Patch for Critical Authentication Flaw
  • Android Malware Exploits Streaming App Ads to Steal Data
  • Japan Unveils Urgent Cybersecurity Initiative Amid Attacks
  • OpenAI Introduces GPT-6 Cyber for Enhanced Security

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark