Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Rails Vulnerability Threatens Cloud Security

Critical Rails Vulnerability Threatens Cloud Security

Posted on August 3, 2026 By CWS

A significant vulnerability in Ruby on Rails has sparked concerns about potential data breaches within cloud environments, particularly affecting companies utilizing Amazon Web Services (AWS) for hosting customer platforms.

Understanding the Vulnerability

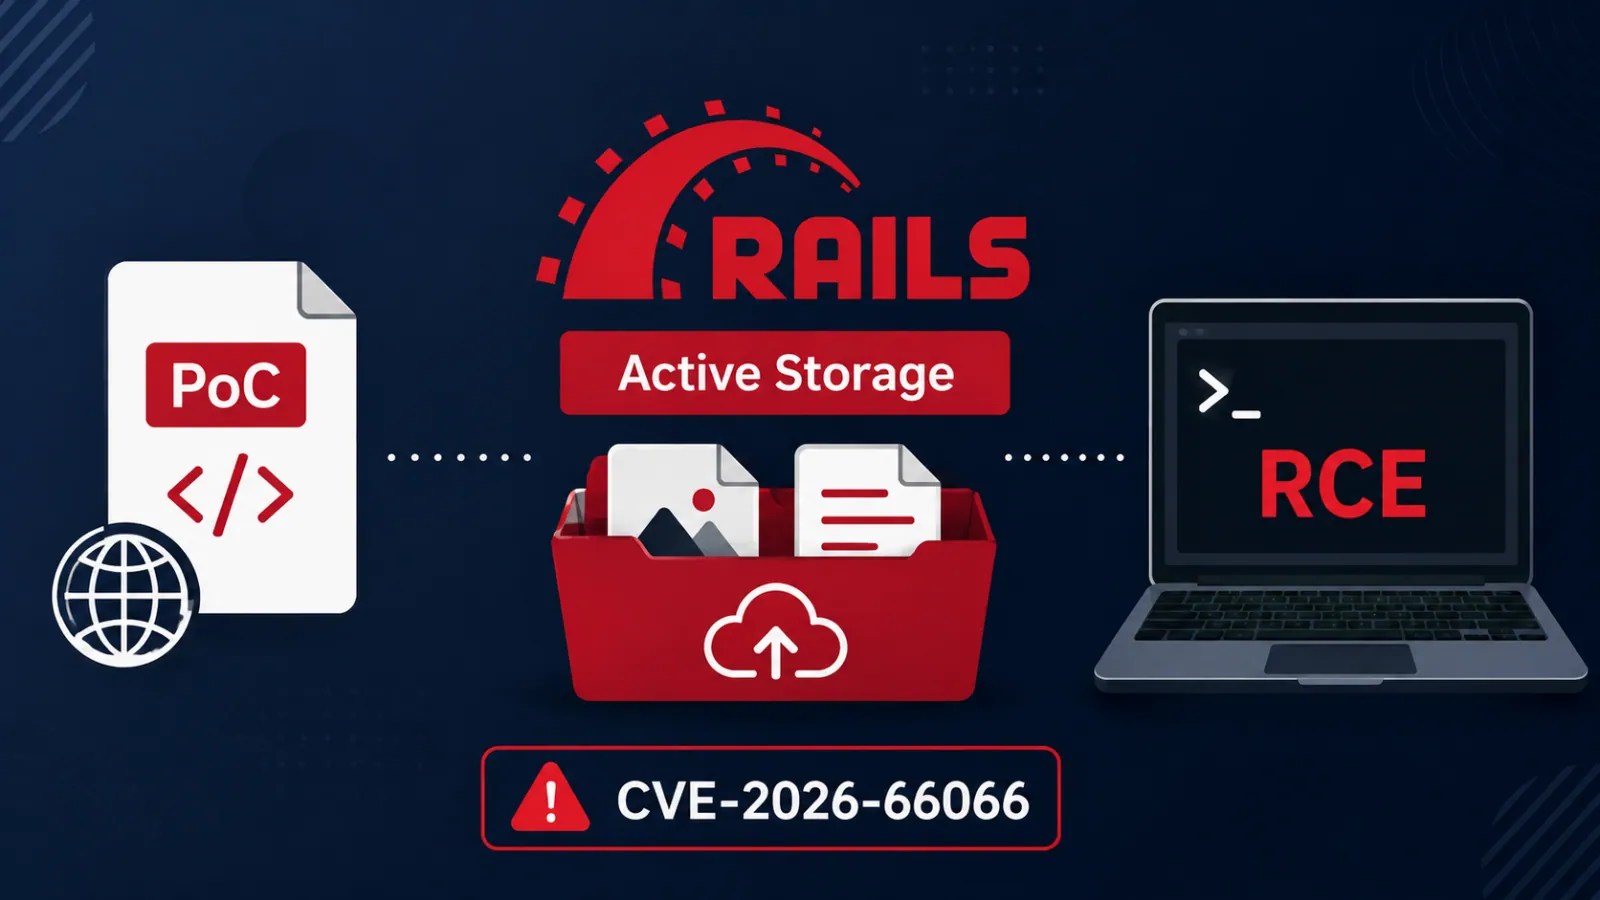
Identified as CVE-2026-66066 or KindaRails2Shell, this security flaw impacts Active Storage setups that incorporate the libvips image-processing library and allow uploads from untrusted sources. Although no confirmed incident involving 350,000 users has been reported, there is a risk of exposing cloud credentials and customer information if the vulnerability is exploited.

This issue stems from Rails Active Storage’s image variant processing, which inadvertently permitted unsafe libvips operations when handling untrusted content. Consequently, attackers could potentially submit crafted uploads, gaining unauthorized access to files within the Rails application environment.

Potential Risks and Implications

Sensitive files, such as environment variables, configuration files, database passwords, API tokens, and AWS access credentials, are at risk. For organizations leveraging AWS, these exposures could be devastating, granting attackers unauthorized access to S3 buckets, databases, backups, application logs, and other services, contingent on the permissions linked to the compromised identity.

If a company stores critical user data, identity information, or internal files within its AWS infrastructure, a breach could lead to significant data exposure, impacting hundreds of thousands of users. Researchers have warned that the vulnerability could extend beyond mere data disclosure.

Exploitation and Mitigation Strategies

Rails applications often store the secret_key_base in environment variables. Unauthorized access to this secret enables attackers to forge Rails-signed data, potentially executing remote code on the server. Such access would occur under the permissions assigned to the Rails process, leading to further data theft, changes in application behavior, or cloud service exploitation.

The vulnerability affects configurations using libvips-based Active Storage processing with untrusted image uploads. Versions of Rails prior to Active Storage 7.2.3.2, 8.0.5.1, and 8.1.3.1 are vulnerable. Additionally, Rails 6 applications configured to use the Vips processor are at risk. A proposed Metasploit module on GitHub demonstrates potential exploit chains for command execution.

Security teams must promptly patch affected Rails deployments, assess Active Storage upload endpoints, rotate Rails secrets and AWS credentials if exposure is suspected, and audit AWS CloudTrail, S3, and application logs for unusual access patterns. Enforcing least-privilege IAM roles and avoiding long-lived cloud secrets in environment variables are crucial steps.

The development of public exploits underscores the urgency for organizations to address exposed Rails services and implement necessary updates to safeguard their environments.
Cyber Security News Tags:Active Storage, AWS, cloud security, CVE-2026-66066, data breach, libvips, Rails, RCE, Security, Vulnerability

Post navigation

Previous Post: Malicious npm Packages Target Alibaba Users with RAT
Next Post: Critical VeloCloud Vulnerability Actively Exploited

Related Posts

Google Releases Guide to Harden Security Strategy and Detection Capabilities Against UNC6040 Google Releases Guide to Harden Security Strategy and Detection Capabilities Against UNC6040 Cyber Security News
Dutch Telecom Giant Hit by Massive Data Breach via Phone Scam Dutch Telecom Giant Hit by Massive Data Breach via Phone Scam Cyber Security News
Conducting Risk Assessments That Drive Business Value Conducting Risk Assessments That Drive Business Value Cyber Security News
Critical Zero-Day Flaws in PDF Software Risk Data Exposure Critical Zero-Day Flaws in PDF Software Risk Data Exposure Cyber Security News
SafePay Ransomware Leverages RDP and VPN for Intruding Into Organizations Network SafePay Ransomware Leverages RDP and VPN for Intruding Into Organizations Network Cyber Security News
Cisco Secure Firewall Snort 3 Detection Engine Vulnerability Enables DoS Attacks Cisco Secure Firewall Snort 3 Detection Engine Vulnerability Enables DoS Attacks Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Plugin4Shell Exploit Threatens AI Coding Tools
  • Security Flaw Exposes OpenAI Code via AI-Generated Exploit
  • Brevo Attack Compromises Over 100,000 WordPress Sites
  • Gyazo Data Breach Exposes 23 Million User Records
  • WeaselBiscuit Malware Detected in 13 npm Packages

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Plugin4Shell Exploit Threatens AI Coding Tools
  • Security Flaw Exposes OpenAI Code via AI-Generated Exploit
  • Brevo Attack Compromises Over 100,000 WordPress Sites
  • Gyazo Data Breach Exposes 23 Million User Records
  • WeaselBiscuit Malware Detected in 13 npm Packages

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark