Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
CISA and NIST Issue Guide to Strengthen Identity Token Security

CISA and NIST Issue Guide to Strengthen Identity Token Security

Posted on September 15, 2026 By CWS

The Cybersecurity and Infrastructure Security Agency (CISA) alongside the National Institute of Standards and Technology (NIST) have unveiled new technical instructions aimed at preventing the misuse of identity and access tokens by malicious entities. The guidance, published as NIST Interagency Report 8587 on September 15, 2026, serves as a comprehensive framework for federal bodies and cloud service providers to fortify single sign-on, identity federation, API accessibility, and machine-to-machine authentication systems.

Understanding the Importance of Identity Tokens

Identity tokens and their signed assertions allow applications to rely on authentication completed by an identity provider, removing the need to frequently prompt users for credentials. However, vulnerabilities arise when attackers steal legitimate tokens, compromise signing keys, or manipulate weak validation processes, enabling them to bypass multifactor authentication and pose as trusted users.

The report highlights incidents where forged SAML assertions and inadequately scoped signing keys led to significant breaches, such as the exposure of over 60,000 emails from a federal agency. This underscores the critical need for robust token security measures.

Implementing Robust Security Measures

The technical guidance emphasizes documenting token architectures, protocols, lifetimes, validation procedures, and incident response strategies. While conformance to this guidance is voluntary unless mandated by policy or contract, the terms “MUST” and “SHOULD” set clear expectations for implementation.

A key focus is on the protection of cryptographic keys used for signing tokens. These keys should utilize approved algorithms, be managed through secure channels, and never exported in plaintext. For systems with moderate to high impact, keys should be stored in hardware-backed or isolated environments, with frequent, risk-based key rotations recommended.

Technical Recommendations and Future Outlook

The checklist calls for stringent token verification practices, where assertions and tokens must include details such as issuer, audience, issuance time, and a unique identifier. Resource servers are tasked with verifying these elements before granting access, to prevent cross-environment key misuse.

Additionally, the report advises on short token lifetimes and the use of sender-constrained mechanisms like mutual TLS to enhance theft and replay resistance. Continuous monitoring of token activity is advocated, integrating with security tools while ensuring sensitive data is not logged.

As the report extends these protocols to AI systems using tokens, it also highlights the need for preparedness for post-quantum migration, given the potential strain on existing security frameworks. Ultimately, the message is clear: token security should be a dynamic, ongoing process rather than a static setup.

Cyber Security News Tags:access tokens, CISA, cloud service providers, cryptographic keys, Cybersecurity, federal agencies, identity tokens, NIST, NIST IR 8587, security guidelines, technical guidance, token misuse, token security, token theft, token validation

Post navigation

Previous Post: Microsoft Sets New AI Privacy Standards for Schools

Related Posts

Top 10 Smart Contract Risks in 2026 by OWASP Top 10 Smart Contract Risks in 2026 by OWASP Cyber Security News
NIST Releases Control Overlays to Manage Cybersecurity Risks in Use and Developments of AI Systems NIST Releases Control Overlays to Manage Cybersecurity Risks in Use and Developments of AI Systems Cyber Security News
How Microsoft Azure Storage Logs Aid Forensics Following a Security Breach How Microsoft Azure Storage Logs Aid Forensics Following a Security Breach Cyber Security News
Qualcomm Adreno GPU 0-Day Vulnerabilities Exploited to Attack Android Users Qualcomm Adreno GPU 0-Day Vulnerabilities Exploited to Attack Android Users Cyber Security News
Hackers Leverage Evilginx to Undermine MFA Security Mimicking Legitimate SSO Sites Hackers Leverage Evilginx to Undermine MFA Security Mimicking Legitimate SSO Sites Cyber Security News
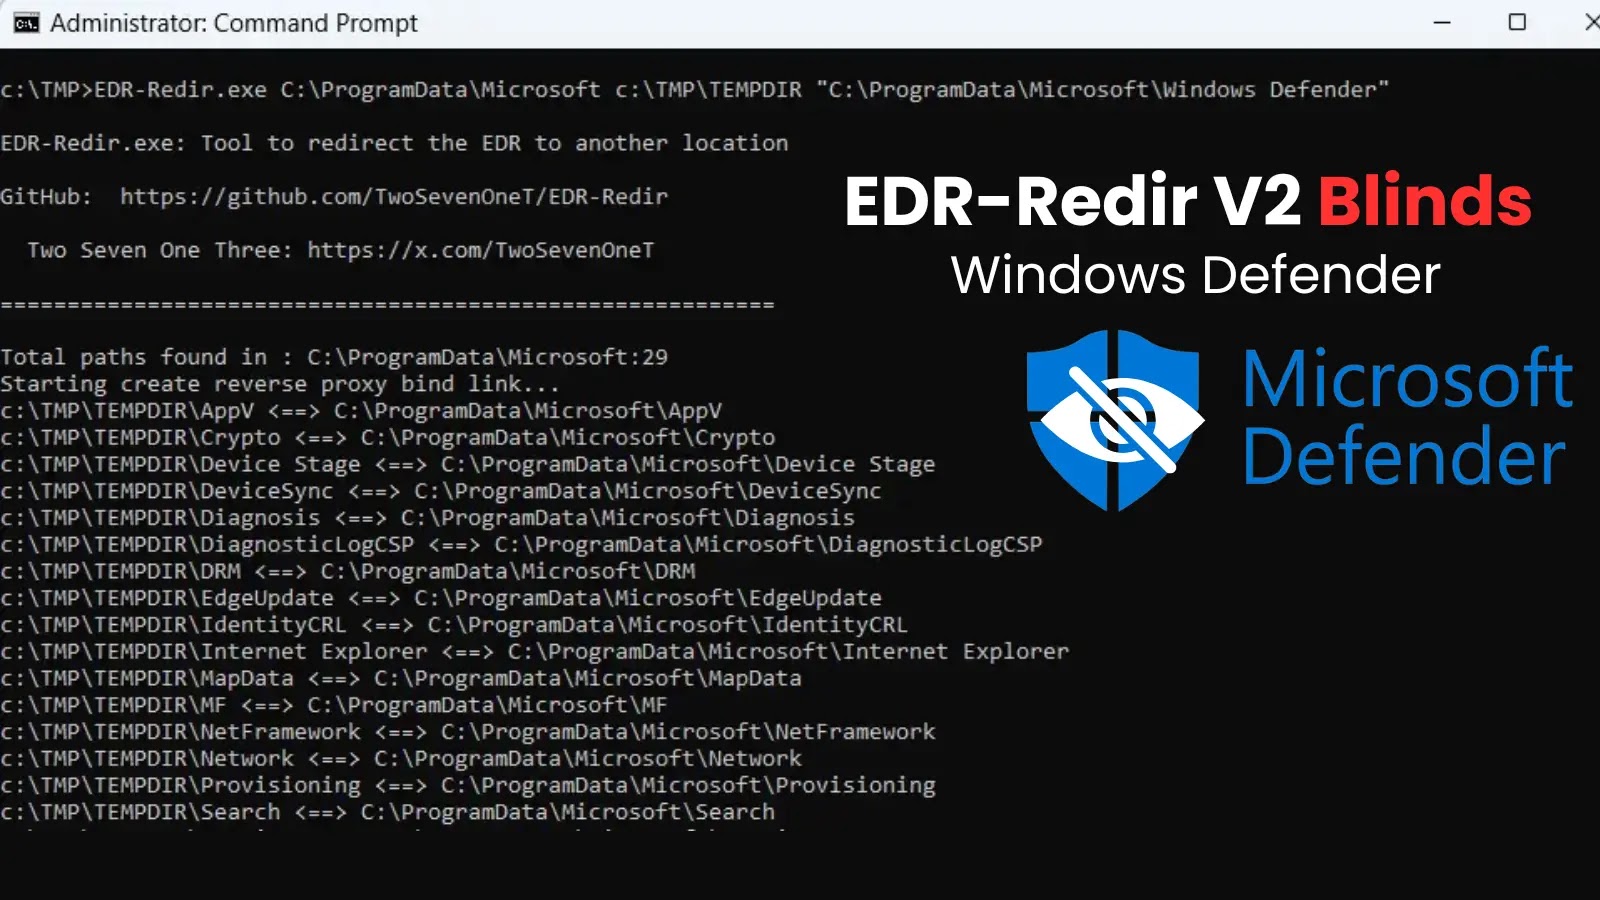
New EDR-Redir V2 Blinds Windows Defender on Windows 11 With Fake Program Files New EDR-Redir V2 Blinds Windows Defender on Windows 11 With Fake Program Files Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CISA and NIST Issue Guide to Strengthen Identity Token Security
  • Microsoft Sets New AI Privacy Standards for Schools
  • Combatting Evolving Malware Infrastructure in SOCs
  • Proving Security Controls: A Modern Necessity
  • KREMLIN Malware Exploits Browsers to Steal Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CISA and NIST Issue Guide to Strengthen Identity Token Security
  • Microsoft Sets New AI Privacy Standards for Schools
  • Combatting Evolving Malware Infrastructure in SOCs
  • Proving Security Controls: A Modern Necessity
  • KREMLIN Malware Exploits Browsers to Steal Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark