Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Open WebUI Flaw Enables Easy RCE Attacks

Critical Open WebUI Flaw Enables Easy RCE Attacks

Posted on May 12, 2026 By CWS

A significant security vulnerability in Open WebUI remains unpatched, posing a serious threat to AI workspaces. This flaw enables attackers to execute remote code, potentially hijacking accounts and accessing sensitive chat histories with just a single click.

Discovery of the Vulnerability

Security researcher Metin Yunus Kandemir identified the flaw, which is rooted in a Stored Cross-Site Scripting (XSS) issue within the platform’s profile image upload feature. Despite the findings, developers have not acknowledged the vulnerability, leading to the exploit code being made public.

The vulnerability arises from inadequate restrictions on media types during image uploads in the Open WebUI application. Specifically, attackers can upload malicious SVG files containing Base64-encoded JavaScript payloads, which are executed by the victim’s browser due to the application’s content handling mechanisms.

Impact on Different User Levels

The severity of this exploit varies based on the user’s permission level within the Open WebUI environment. If an administrator or user with high privileges encounters the malicious image link, the attacker can achieve 1-Click Remote Code Execution (RCE), creating a backdoor via the API.

Standard users are not immune, as the script can trigger an Account Takeover (ATO) by extracting authentication tokens and chat history, sending this data to an external server. This attack occurs without additional authentication if the user is already logged in.

Response and Mitigation Measures

This zero-day vulnerability persists in Open WebUI version 0.7.2, initially reported on March 10, 2026. However, the Open WebUI team dismissed the report as a duplicate on May 6, 2026, without providing an official fix, prompting Kandemir to publish the Proof of Concept (PoC) on May 8, 2026.

Organizations using Open WebUI are advised to implement manual defenses, including restricting file types to safe formats like JPEG and PNG while blocking SVG files. Users should be cautious of suspicious links, especially those directing to the Open WebUI application.

The absence of an official patch necessitates vigilant monitoring and proactive security measures to safeguard environments using Open WebUI.

Cyber Security News Tags:cyber threat, Cybersecurity, data breach, Open WebUI, RCE attack, remote code execution, security flaw, security patch, Vulnerability, XSS flaw

Post navigation

Previous Post: Adobe Releases Urgent Security Updates for 52 Vulnerabilities
Next Post: Critical Exim Vulnerability Puts GnuTLS Builds at Risk

Related Posts

New Tengu Botnet Enhances IoT Device Resilience New Tengu Botnet Enhances IoT Device Resilience Cyber Security News
Leaked Russian University Records Reveal GRU Cyber Training Leaked Russian University Records Reveal GRU Cyber Training Cyber Security News
New Scraper Botnet with 3,600+ Unique Devices Attacking Targets in US and UK New Scraper Botnet with 3,600+ Unique Devices Attacking Targets in US and UK Cyber Security News
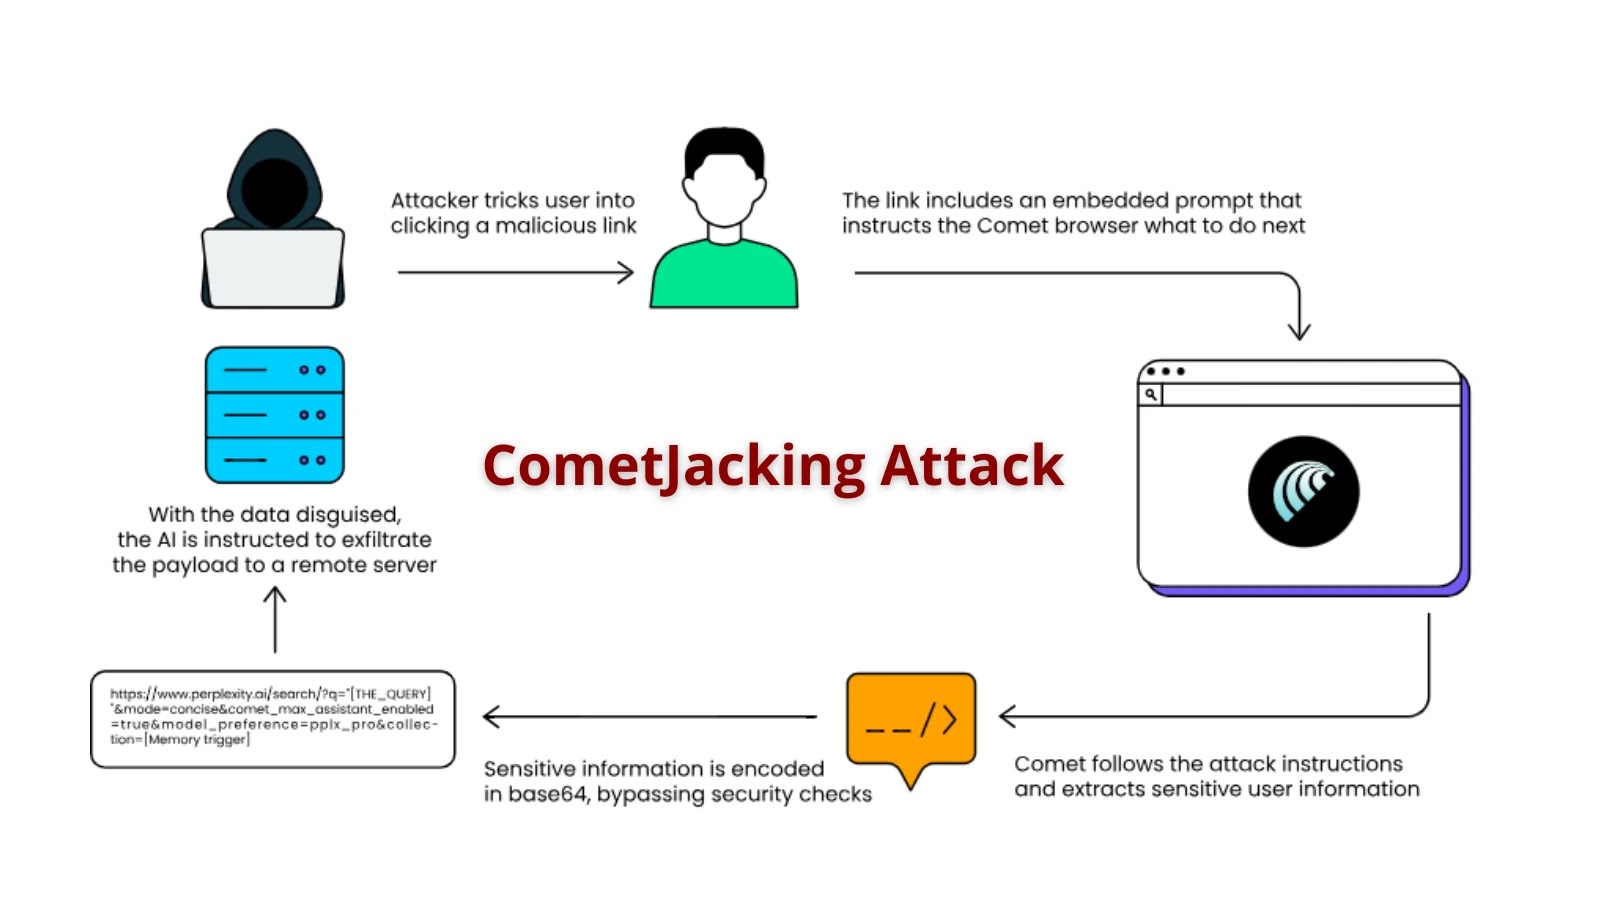
New CometJacking Attack Let Attackers Turn Perplexity Browser Against You in One Click New CometJacking Attack Let Attackers Turn Perplexity Browser Against You in One Click Cyber Security News
Massive Spike in Password Attacks Targeting Cisco ASA VPN Followed by Microsoft 365 Massive Spike in Password Attacks Targeting Cisco ASA VPN Followed by Microsoft 365 Cyber Security News
New SHUYAL Attacking 19 Popular Browsers to Steal Login Credentials New SHUYAL Attacking 19 Popular Browsers to Steal Login Credentials Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AI-Powered NotC2 Framework Exploits AWS Services
  • CISA Highlights SonicOS SSLVPN Security Weakness
  • GhostAction Campaign Targets 500 GitHub Accounts for Credentials
  • Notepad++ 8.9.9 Update Resolves Critical Security Flaws
  • Ethersphere Tools Breached, Malware Targets Wallets

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AI-Powered NotC2 Framework Exploits AWS Services
  • CISA Highlights SonicOS SSLVPN Security Weakness
  • GhostAction Campaign Targets 500 GitHub Accounts for Credentials
  • Notepad++ 8.9.9 Update Resolves Critical Security Flaws
  • Ethersphere Tools Breached, Malware Targets Wallets

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark