Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Ruby on Rails Flaw Enables Remote Code Execution

Critical Ruby on Rails Flaw Enables Remote Code Execution

Posted on July 30, 2026 By CWS

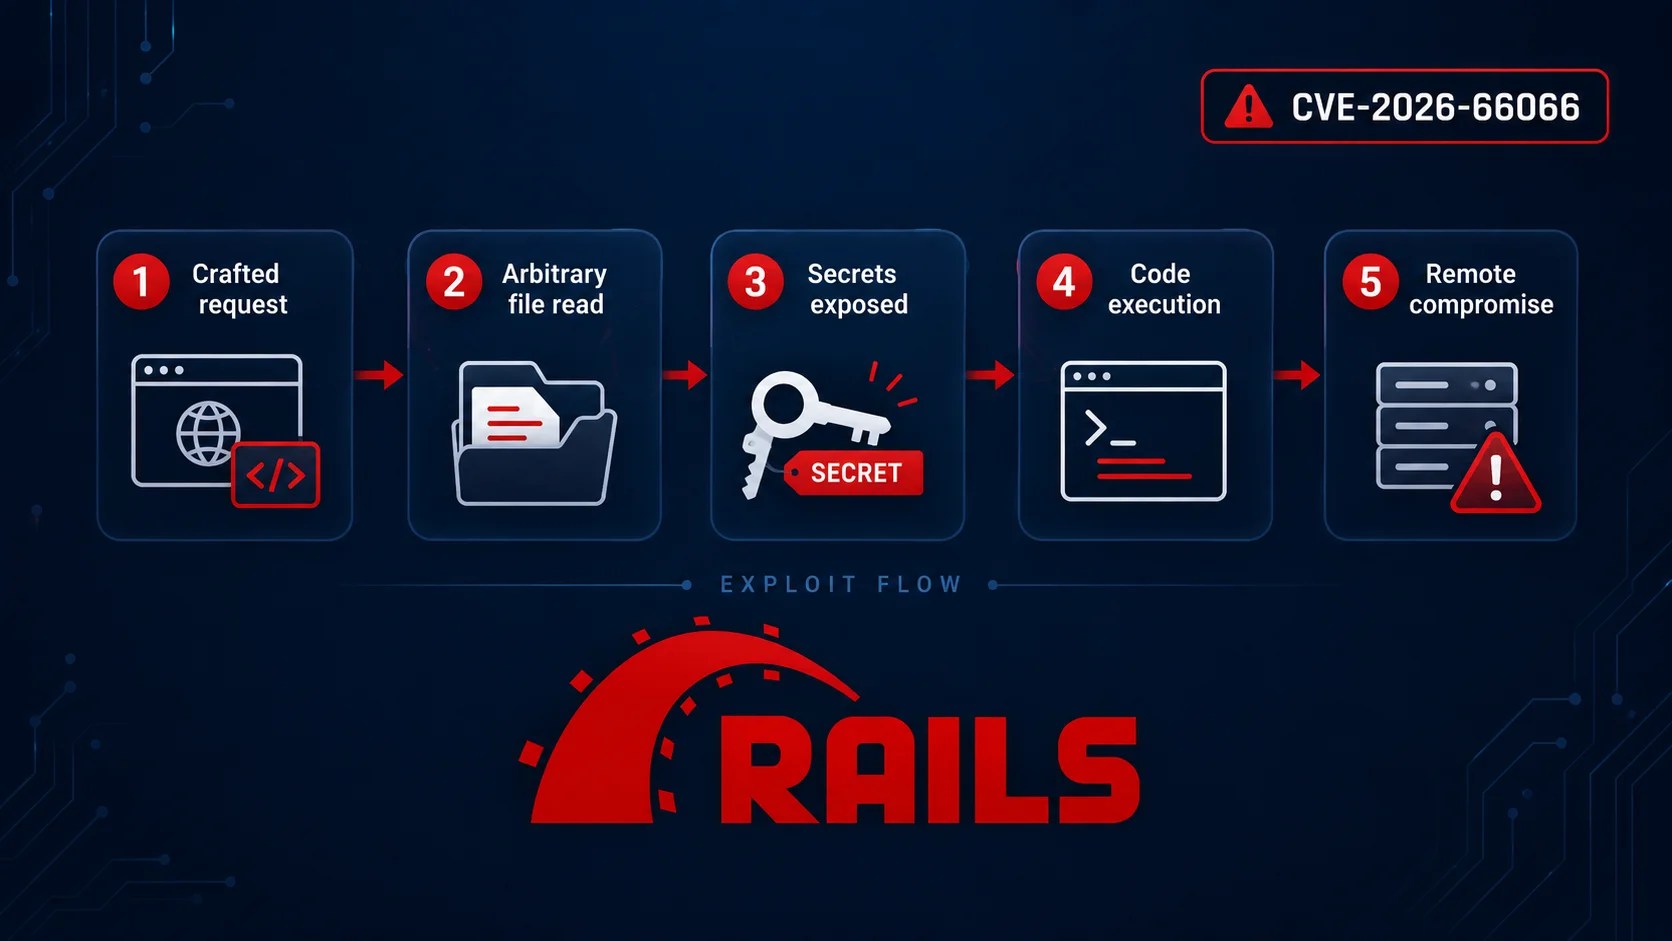
A significant security flaw identified in Ruby on Rails, specifically within Active Storage and tracked as CVE-2026-66066, poses a severe risk. This vulnerability allows unauthorized individuals to access sensitive files on a server, potentially leading to remote code execution.

Vulnerability Details and Risks

This security issue impacts applications utilizing libvips for processing image variants and accepting image uploads from users who are not trusted. The flaw exposes sensitive information like secret_key_base, cloud credentials, and database passwords, especially in cases where the vulnerability is not addressed.

In a typical Rails setup displaying image variants, an attacker could exploit the flaw by uploading a specifically crafted file. This triggers libvips to process the file format in a manner that could be manipulated for malicious purposes.

Technical Mechanisms Behind the Flaw

Libvips processes image formats using loaders and savers that rely on third-party libraries. Some operations within this process are marked as “unfuzzed,” indicating they are unsafe for handling content from untrusted sources. Active Storage fails to disable these risky operations, allowing a potential pathway for executing harmful code.

The vulnerability is a concern for applications using libvips in Active Storage for image processing, particularly with the configuration setting config.active_storage.variant_processor = :vips, which is the default from Rails 7.0 onwards. The issue is prevalent when allowing image uploads from unverified users.

Mitigation and Security Recommendations

Vulnerable versions include activestorage below 7.2.3.2, 8.0.x below 8.0.5.1, and 8.1.x below 8.1.3.1. Patches are now available through standard Rails distribution channels, and upgrading to libvips version 8.13 or later is essential for a secure setup.

System administrators must update activestorage to a secure release and ensure libvips is at least version 8.13 to prevent further exploitation. However, patching does not recover any compromised data, so all sensitive information accessible by the application process should be considered exposed and should undergo rotation.

Immediate Actions and Future Outlook

Key actions include upgrading Rails and libvips, rotating sensitive data such as secret_key_base, and ensuring untrusted operations are blocked before accepting new uploads. In cases where an upgrade is not feasible, setting the VIPS_BLOCK_UNTRUSTED environment variable for libvips 8.13 or newer may serve as a temporary measure.

Full technical details of the vulnerability are withheld to prevent misuse, with a complete disclosure planned by August 28, 2026. Organizations using Rails with Active Storage and libvips are urged to prioritize these security measures immediately.

Cyber Security News Tags:Active Storage, CVE-2026-66066, Cybersecurity, data protection, image processing, libvips, rails security, remote code execution, Ruby on Rails, secret rotation, security flaw, software patching, software vulnerability, untrusted uploads

Post navigation

Previous Post: Microsoft Word Copilot Vulnerability: AI Worm Threat
Next Post: Cisco Firewall Flaw Exploited, Risks Sensitive Data Exposure

Related Posts

PhantomVAI Loader Utilizes RunPE for Stealthy Attacks PhantomVAI Loader Utilizes RunPE for Stealthy Attacks Cyber Security News
Chinese UNC6384 Hackers Leverages Valid Code Signing Certificates to Evade Detection Chinese UNC6384 Hackers Leverages Valid Code Signing Certificates to Evade Detection Cyber Security News
Microsoft Probes Exchange Online Outage EX1464935 Microsoft Probes Exchange Online Outage EX1464935 Cyber Security News
Cybercriminal Cryptocurrency Transactions Peaked in 2025 Following Nation‑State Sanctions Evasion Moves Cybercriminal Cryptocurrency Transactions Peaked in 2025 Following Nation‑State Sanctions Evasion Moves Cyber Security News
Windows Remote Desktop Services Vulnerability Let Attackers Escalate Privileges Windows Remote Desktop Services Vulnerability Let Attackers Escalate Privileges Cyber Security News
Scammers Exploit Brand Trust to Lure Casino Traffic Scammers Exploit Brand Trust to Lure Casino Traffic Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • FBI Seizes Domain of Hosting Service Linked to Cybercrime
  • Ukrainian Involved in Nefilim Ransomware Sentenced in US
  • Critical UEFI Flaw Exposes Servers to Pre-Boot Attacks
  • Google Patches 52 Chrome Security Issues, Including Critical Flaws
  • Upwind Security Secures $400M, Reaches $3.8B Valuation

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • FBI Seizes Domain of Hosting Service Linked to Cybercrime
  • Ukrainian Involved in Nefilim Ransomware Sentenced in US
  • Critical UEFI Flaw Exposes Servers to Pre-Boot Attacks
  • Google Patches 52 Chrome Security Issues, Including Critical Flaws
  • Upwind Security Secures $400M, Reaches $3.8B Valuation

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark