Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
VLC Media Player Security Flaws Pose Serious Risks

VLC Media Player Security Flaws Pose Serious Risks

Posted on September 12, 2026 By CWS

VLC Media Player users are urged to stay vigilant due to two newly identified vulnerabilities that could jeopardize data security. These flaws can be exploited to corrupt heap memory or access confidential information from a user’s memory.

Understanding the Vulnerabilities

The vulnerabilities, cataloged as CVE-2026-56711 and CVE-2026-73324, impact VLC Media Player versions from 3.0.0 to 3.0.23. They require users to engage with specifically crafted media files or playlist entries, which highlights the importance of cautious media handling.

These issues were identified by Fabian Wahle from Hap Security, with CVE-2026-56711 rated as high severity due to its CVSS score of 8.6, and CVE-2026-73324 rated at medium severity with a score of 6.9. Disclosures for both vulnerabilities occurred on September 9, 2026.

Technical Breakdown of CVE-2026-56711

CVE-2026-56711 is identified as an integer overflow and out-of-bounds write vulnerability within VLC’s picture-buffer allocation mechanism. The flaw is linked to CWE-190, which addresses Integer Overflow or Wraparound, and CWE-787, concerning Out-of-bounds Write.

The problem lies in the AllocatePicture function in VLC’s src/misc/picture.c component. It calculates buffer sizes for decoded images using i_pitch * i_lines, defined as signed int fields. However, 32-bit arithmetic can lead to a wraparound, causing insufficient memory allocation for decoding.

Exploiting this, attackers can use manipulated PNG images with exaggerated dimensions to bypass existing checks, resulting in potential heap memory corruption and other serious impacts.

Details on CVE-2026-73324

CVE-2026-73324 involves VLC’s RTSP access module and the potential exposure of heap memory to malicious servers. This vulnerability is described by CWE-125 (Out-of-bounds Read) and CWE-170 (Improper Null Termination).

The flaw arises when VLC processes RTSP response lines without appending a null terminator, leading to memory being read beyond allocated buffers. This can be exploited via a realrtsp URL in a playlist, potentially exposing sensitive memory data to a malicious RTSP server.

Importantly, the RTSP module’s presence in builds varies, but it is active in official VideoLAN distributions, affecting exposure levels.

Protective Measures and Recommendations

Users of VLC Media Player versions 3.0.0 to 3.0.23 should remain alert for updates from VideoLAN’s repositories and advisories. Until patches are available, it is advisable to avoid engaging with untrusted PNG files, media playlists, and RTSP streams.

Organizations should consider restricting VLC usage in high-risk settings, blocking untrusted RTSP connections, and employing endpoint monitoring to identify suspicious activities.

By staying informed and cautious, users and organizations can mitigate the risks posed by these vulnerabilities while awaiting a secure update.

Cyber Security News Tags:buffer overflow, CVE-2026-56711, CVE-2026-73324, cybersecurity risks, data exposure, heap memory, heap memory flaws, integer overflow, media player security, RTSP module, security update, software patches, technology news, VideoLAN, VLC vulnerabilities

Post navigation

Previous Post: Enhancing Security: Tackling Cloud Supply-Chain Threats
Next Post: CISA Highlights Critical Security Flaws in Artifactory and RouterOS

Related Posts

AI Browsers Present New Security Risks with Prompt Injection AI Browsers Present New Security Risks with Prompt Injection Cyber Security News
Hackers Target Ivanti EPMM Devices with Hidden Backdoors Hackers Target Ivanti EPMM Devices with Hidden Backdoors Cyber Security News
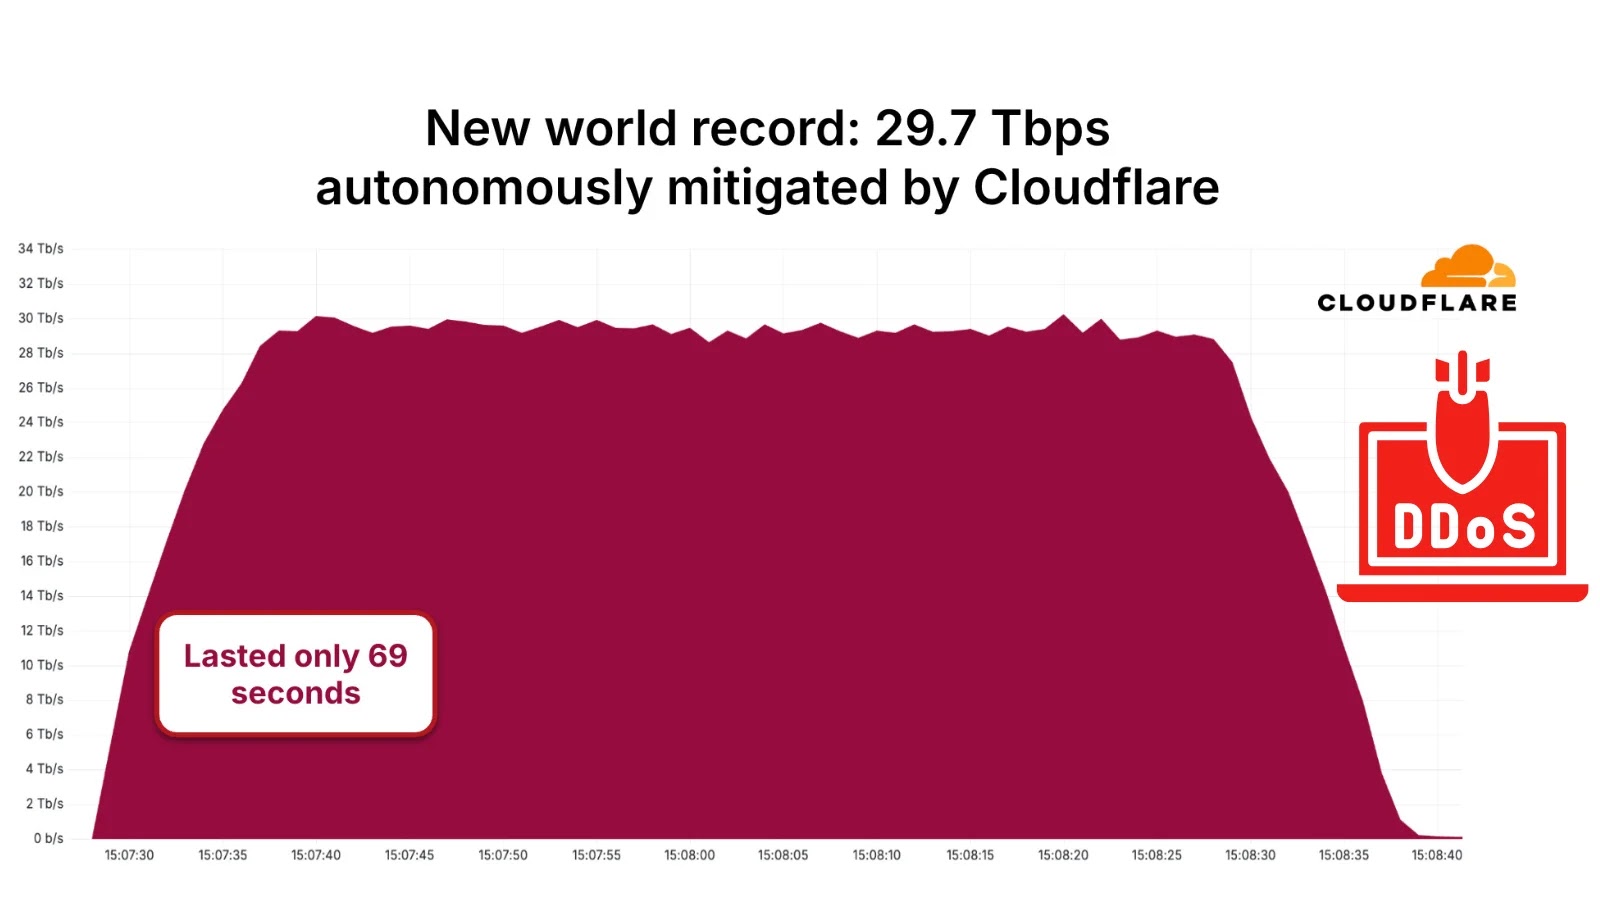
29.7 Tbps DDoS Attack Via Aisuru botnet Breaks Internet With New World Record 29.7 Tbps DDoS Attack Via Aisuru botnet Breaks Internet With New World Record Cyber Security News
87,000+ MongoDB Instances Vulnerable to MongoBleed Flaw Exposed Online 87,000+ MongoDB Instances Vulnerable to MongoBleed Flaw Exposed Online Cyber Security News
Global Expansion of Gentlemen Ransomware Threats Global Expansion of Gentlemen Ransomware Threats Cyber Security News
NordVPN Denies Data Breach Following Threat Actor Claim on Dark Web NordVPN Denies Data Breach Following Threat Actor Claim on Dark Web Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical Flaw in React Server Components Puts Next.js Servers at Risk
  • Android Devices with Preinstalled Malware Threaten Users Globally
  • GoBalance Bug Puts Dark Web Sites at Risk of Hijacking
  • Malicious PDF App on Google Play Spreads Anatsa Trojan
  • US Dismantles Chinese Hacking Tools Targeting Infrastructure

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical Flaw in React Server Components Puts Next.js Servers at Risk
  • Android Devices with Preinstalled Malware Threaten Users Globally
  • GoBalance Bug Puts Dark Web Sites at Risk of Hijacking
  • Malicious PDF App on Google Play Spreads Anatsa Trojan
  • US Dismantles Chinese Hacking Tools Targeting Infrastructure

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark