Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
FortiSandbox Flaw Risks Sensitive Data Exposure

FortiSandbox Flaw Risks Sensitive Data Exposure

Posted on September 9, 2026 By CWS

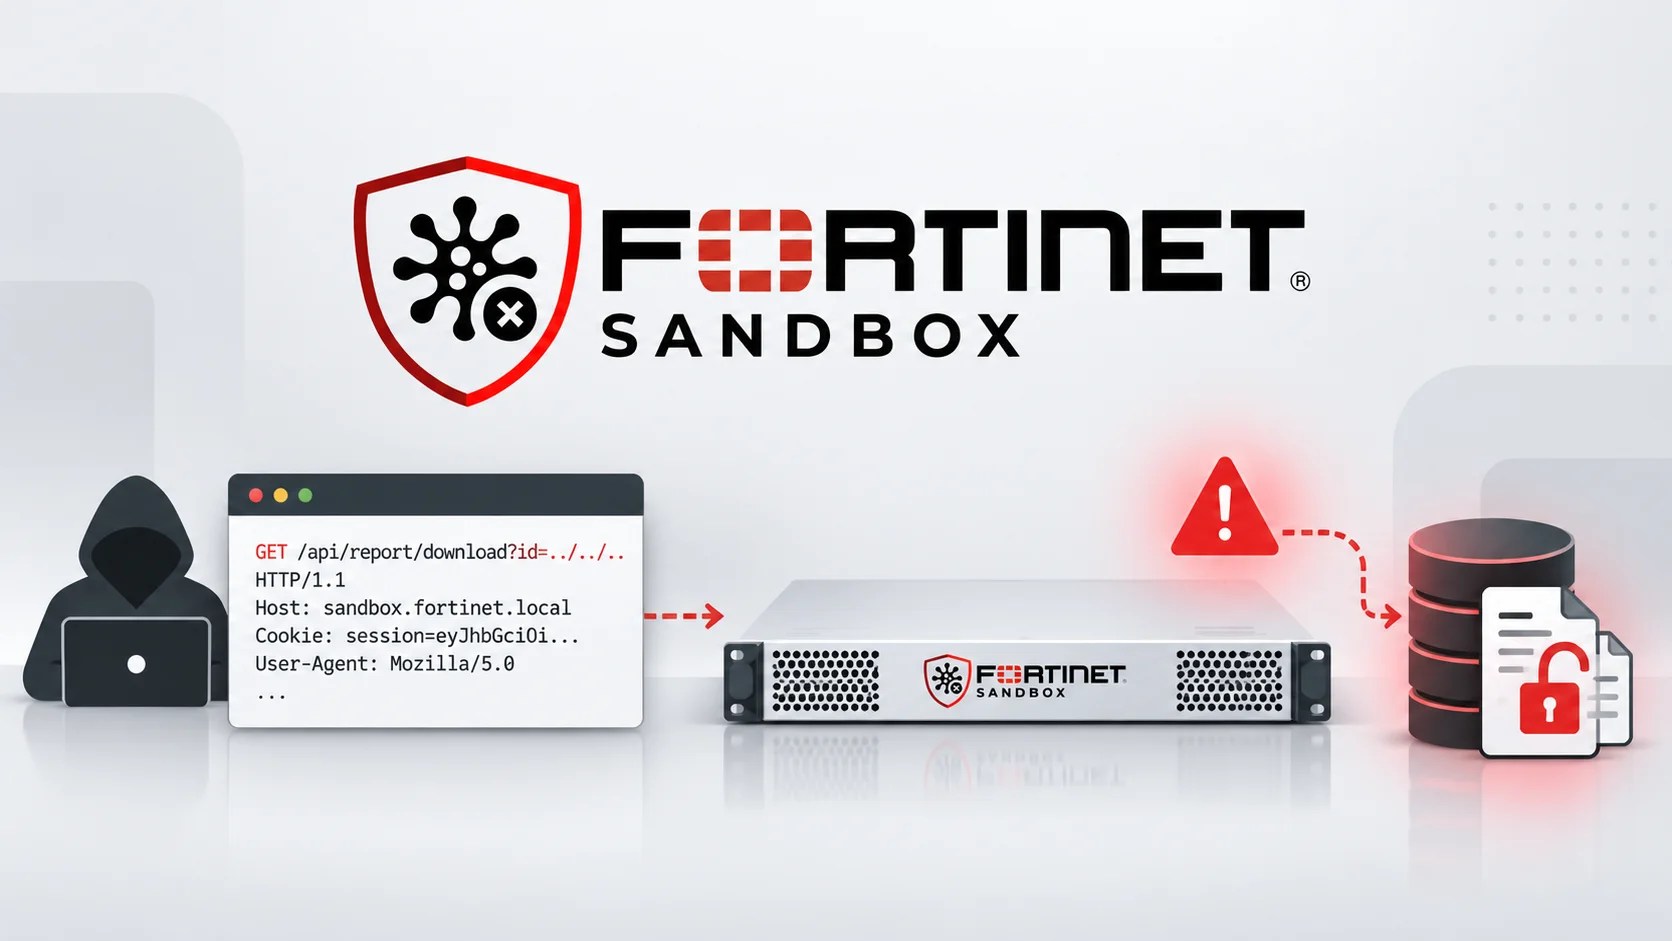
Fortinet has identified a critical security flaw within its FortiSandbox platform, alerting users that unauthorized individuals could exploit this vulnerability to access sensitive data. This flaw does not require attackers to have valid credentials, significantly increasing the risk of exploitation.

Understanding the FortiSandbox Vulnerability

The vulnerability, tagged as CVE-2026-26084, arises from insufficient access control in the graphical user interface shared by FortiSandbox, FortiSandbox Cloud, and FortiSandbox PaaS. With a CVSS v3.1 score of 8.9, it is categorized as a high-severity issue.

FortiSandbox is a widely utilized tool in enterprise and government networks for advanced threat detection. It employs sandboxing techniques to analyze suspicious files and network activities for zero-day threats and other sophisticated attacks.

Details of the Exploit

According to Fortinet’s advisory, the vulnerability is linked to CWE-284, indicating improper access control. This flaw means the web interface does not verify if a request is from an authorized session before providing sensitive information.

Attackers with knowledge of the application’s internal API can craft specific HTTP requests to bypass authentication checks on the FortiSandbox web interface. The exploitation does not require user interaction or any prior privileges, as noted in the CVSS vector’s classification of the attack as unauthenticated.

Although this vulnerability does not allow data modification or code execution, the potential exposure of sensitive information such as configuration details and logs is significant enough to necessitate immediate patching.

Recommended Actions

Fortinet credits Adham El Karn from its Product Security team for discovering this issue. The company states there is no current evidence of the vulnerability being exploited in the wild.

FortiSandbox version 5.2 remains unaffected, while versions 5.0 and 4.4 are vulnerable. Administrators are urged to upgrade to version 5.0.6 or later for 5.0 series, and to 4.4.9 or newer for the 4.4 series. FortiSandbox Cloud and PaaS versions also require similar upgrades to mitigate the risk.

This vulnerability highlights a broader pattern of authorization weaknesses in Fortinet’s product line. Organizations using any affected version of FortiSandbox should promptly update to the safer versions to safeguard their systems.

Stay informed about the latest in cybersecurity and download our free AI SOC Deployment Playbook 2026 to enhance your security operations.

Cyber Security News Tags:access control, CVE-2026-26084, Cybersecurity, data breach, Fortinet, FortiSandbox, network security, sandboxing, security patch, Vulnerability

Post navigation

Previous Post: ChatGPT Vulnerability Exposed Gmail Data Risks
Next Post: Critical N-able N-central Flaw Exploited, Urgent Patch Required

Related Posts

Google Engineer Accused of .2 Million Insider Trading Google Engineer Accused of $1.2 Million Insider Trading Cyber Security News
Critical Flaw in Grandstream VoIP Phones Exposes Networks Critical Flaw in Grandstream VoIP Phones Exposes Networks Cyber Security News
Russian Hackers Target Routers in Major DNS Hijacking Scheme Russian Hackers Target Routers in Major DNS Hijacking Scheme Cyber Security News
LeakNet Ramps Up Ransomware Attacks with New Techniques LeakNet Ramps Up Ransomware Attacks with New Techniques Cyber Security News
How Winning SOCs Always Stay Ahead of Threats  How Winning SOCs Always Stay Ahead of Threats  Cyber Security News
Critical OpenClaw Vulnerability Allows AI Agent Hijacking Critical OpenClaw Vulnerability Allows AI Agent Hijacking Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Google AI Features May Influence Targeted Ads
  • LiteLLM Security Breach Exposes GitHub Tokens
  • Brotli Decoder Flaw Impacts Major Software Platforms
  • Security Firm Halts Botnet Threat from Popcorn Time Updater
  • PHP Vulnerabilities Impact Palo Alto PAN-OS Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Google AI Features May Influence Targeted Ads
  • LiteLLM Security Breach Exposes GitHub Tokens
  • Brotli Decoder Flaw Impacts Major Software Platforms
  • Security Firm Halts Botnet Threat from Popcorn Time Updater
  • PHP Vulnerabilities Impact Palo Alto PAN-OS Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark